
![Excaliself]() Excaliself
Stack
Self-hosted Excalidraw whiteboards for teams, with accounts, live collaboration, a shared team space, folders and search. Drawings are stored in Postgres. Source: https://github.com/maciekzygmunt/excaliself
Source details
Configuration
TypeComposelinuxPOSTGRES_PASSWORD=''BETTER_AUTH_SECRET=''BASE_URL=''EXCALISELF_PORT=3000unless-stoppedTemplate by maciekzygmunt·Source
Report issueNotes
openssl rand -hex 24), the auth secret (openssl rand -base64 32) and the address you will open the app at, e.g. http://<your-host>:3000, before you deploy. The stack won't start without them. Then open that address: the first visitor creates the admin account, so do this right away. Drawings are stored in the pgdata volume. For a public server, put a reverse proxy with HTTPS in front. Docs: excaliself.com/docsServices
db
Configuration
Imagepostgres:17-alpine/var/lib/postgresql/data : pgdataPOSTGRES_USER=${POSTGRES_USER:-excaliself}POSTGRES_PASSWORD=${POSTGRES_PASSWORD:?Set POSTGRES_PASSWORD in .env}POSTGRES_DB=${POSTGRES_DB:-excaliself}unless-stoppedImage details
excaliself
Configuration
Imageghcr.io/maciekzygmunt/excaliself:${EXCALISELF_VERSION:-latest}${EXCALISELF_PORT:-3000}:3000DATABASE_URL=postgresql://${POSTGRES_USER:-excaliself}:${POSTGRES_PASSWORD}@db:5432/${POSTGRES_DB:-excaliself}BETTER_AUTH_SECRET=${BETTER_AUTH_SECRET:?Set BETTER_AUTH_SECRET in .env}BASE_URL=${BASE_URL:?Set BASE_URL to the address you open Excaliself at, e.g. http://192.168.1.10:3000}TRUSTED_ORIGINS=${TRUSTED_ORIGINS:-}GOOGLE_CLIENT_ID=${GOOGLE_CLIENT_ID:-}GOOGLE_CLIENT_SECRET=${GOOGLE_CLIENT_SECRET:-}MICROSOFT_CLIENT_ID=${MICROSOFT_CLIENT_ID:-}MICROSOFT_CLIENT_SECRET=${MICROSOFT_CLIENT_SECRET:-}MICROSOFT_TENANT_ID=${MICROSOFT_TENANT_ID:-}OIDC_ISSUER=${OIDC_ISSUER:-}OIDC_CLIENT_ID=${OIDC_CLIENT_ID:-}OIDC_CLIENT_SECRET=${OIDC_CLIENT_SECRET:-}OIDC_NAME=${OIDC_NAME:-}SSO_ALLOWED_DOMAINS=${SSO_ALLOWED_DOMAINS:-}IMAGE_UPLOADS_PER_MINUTE=${IMAGE_UPLOADS_PER_MINUTE:-}unless-stoppedStandalone Install
Select an install method, to see config/commands for deploying Excaliself
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
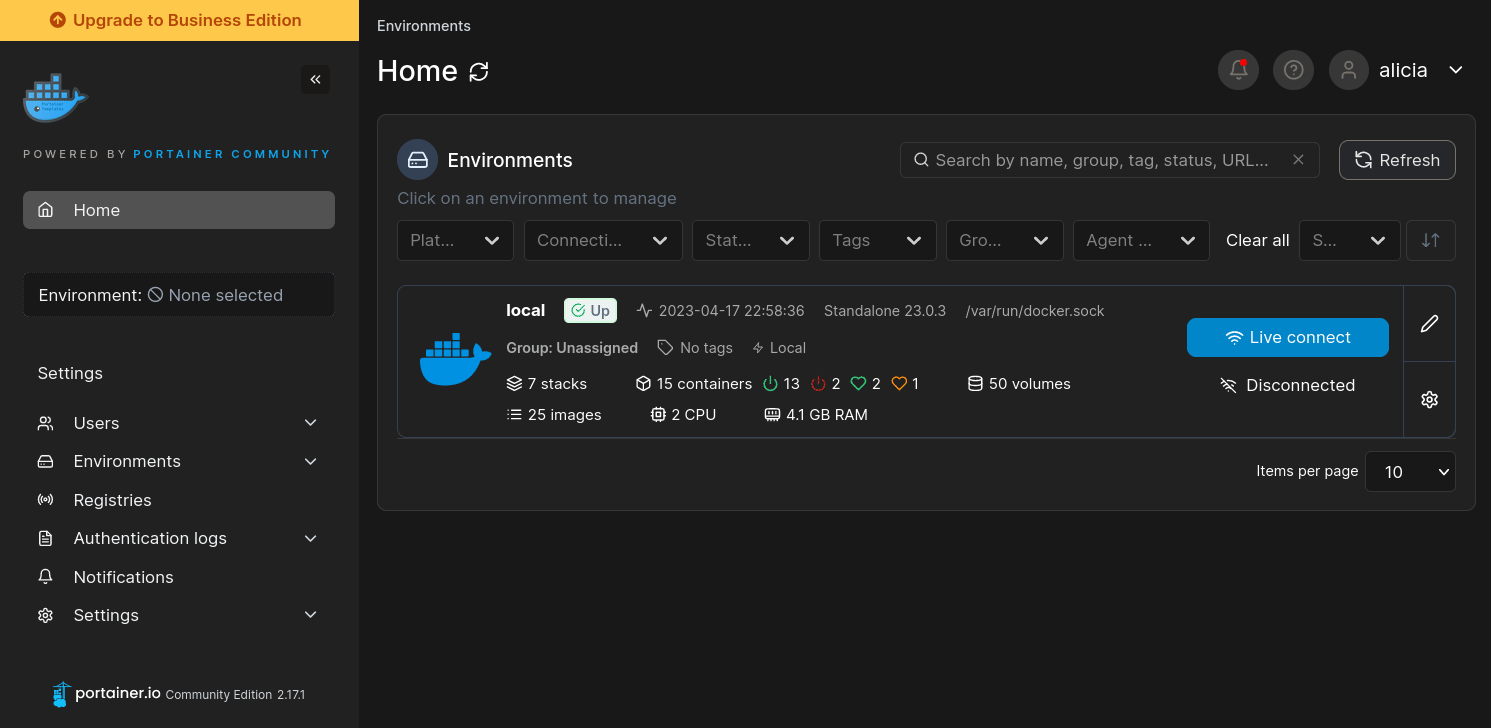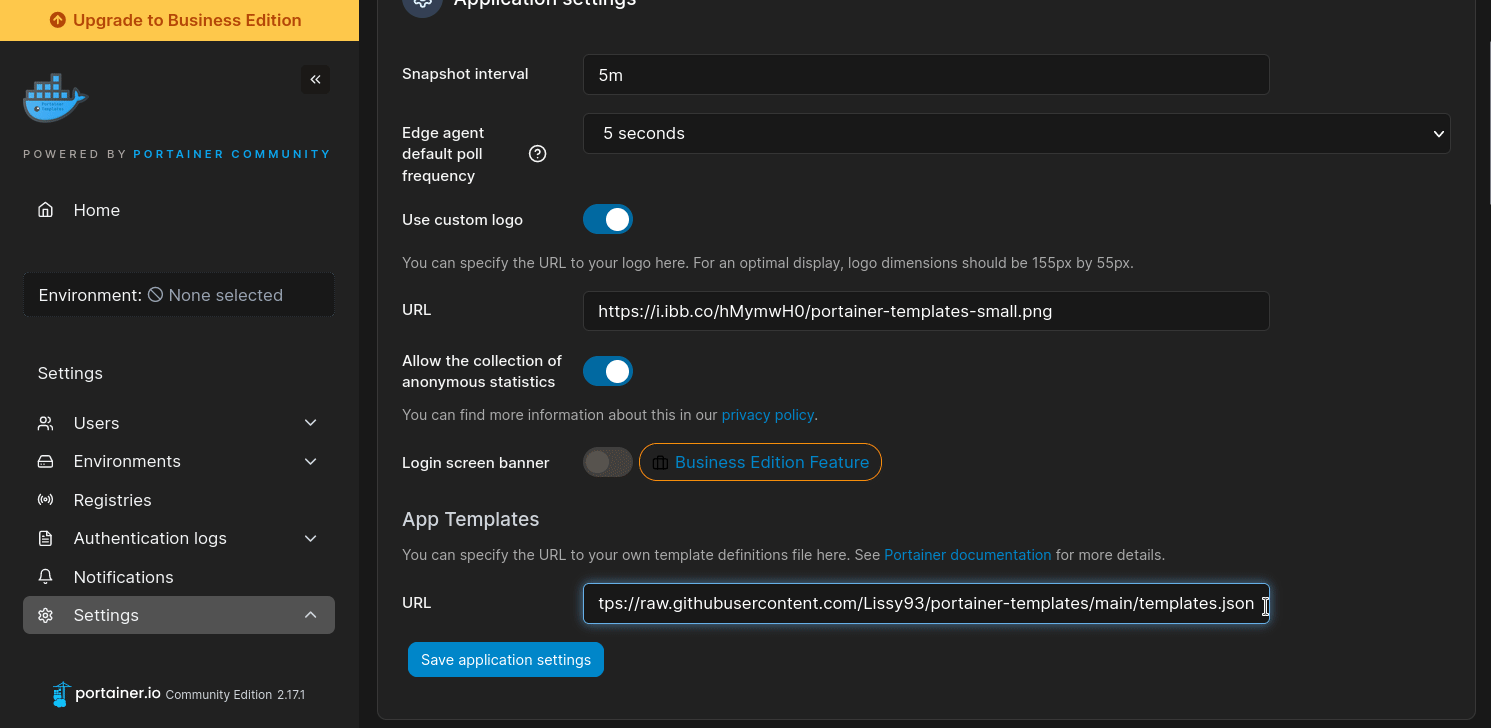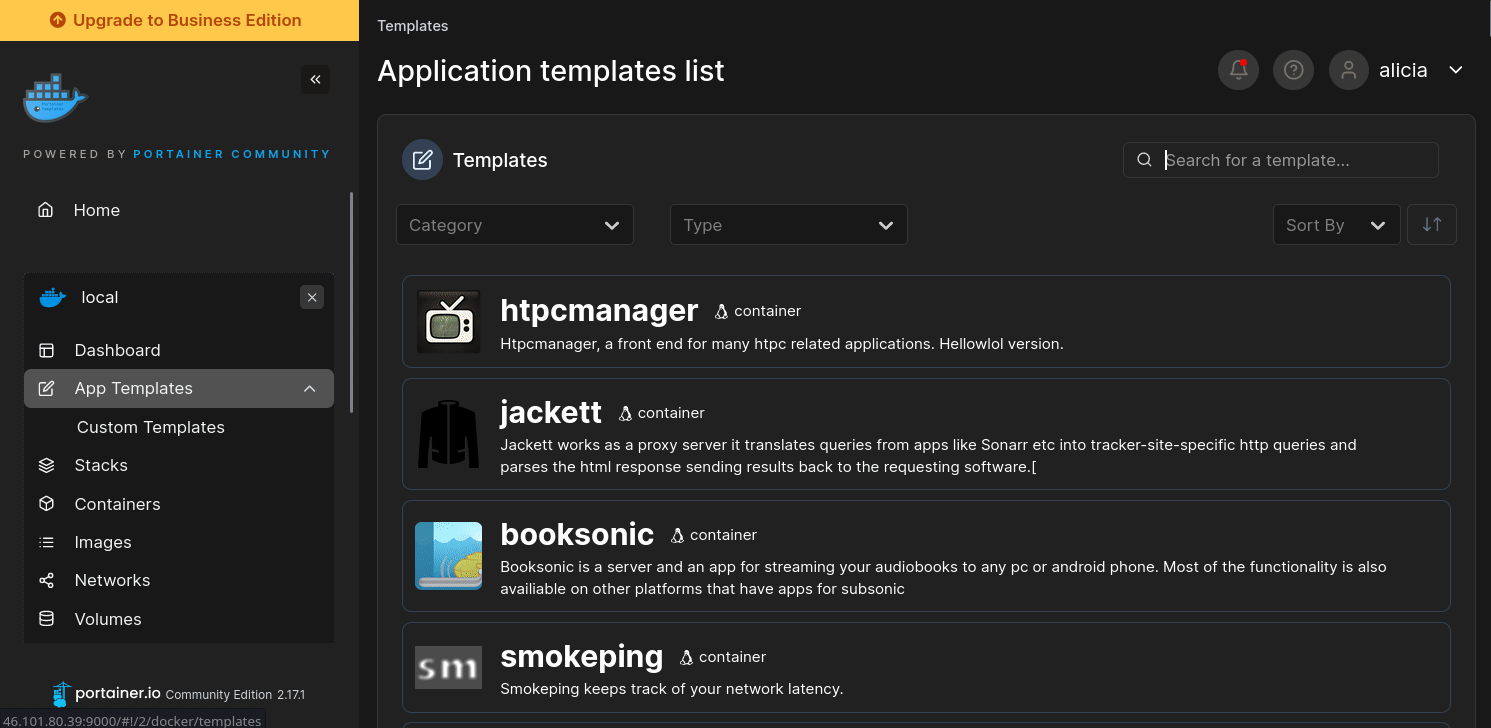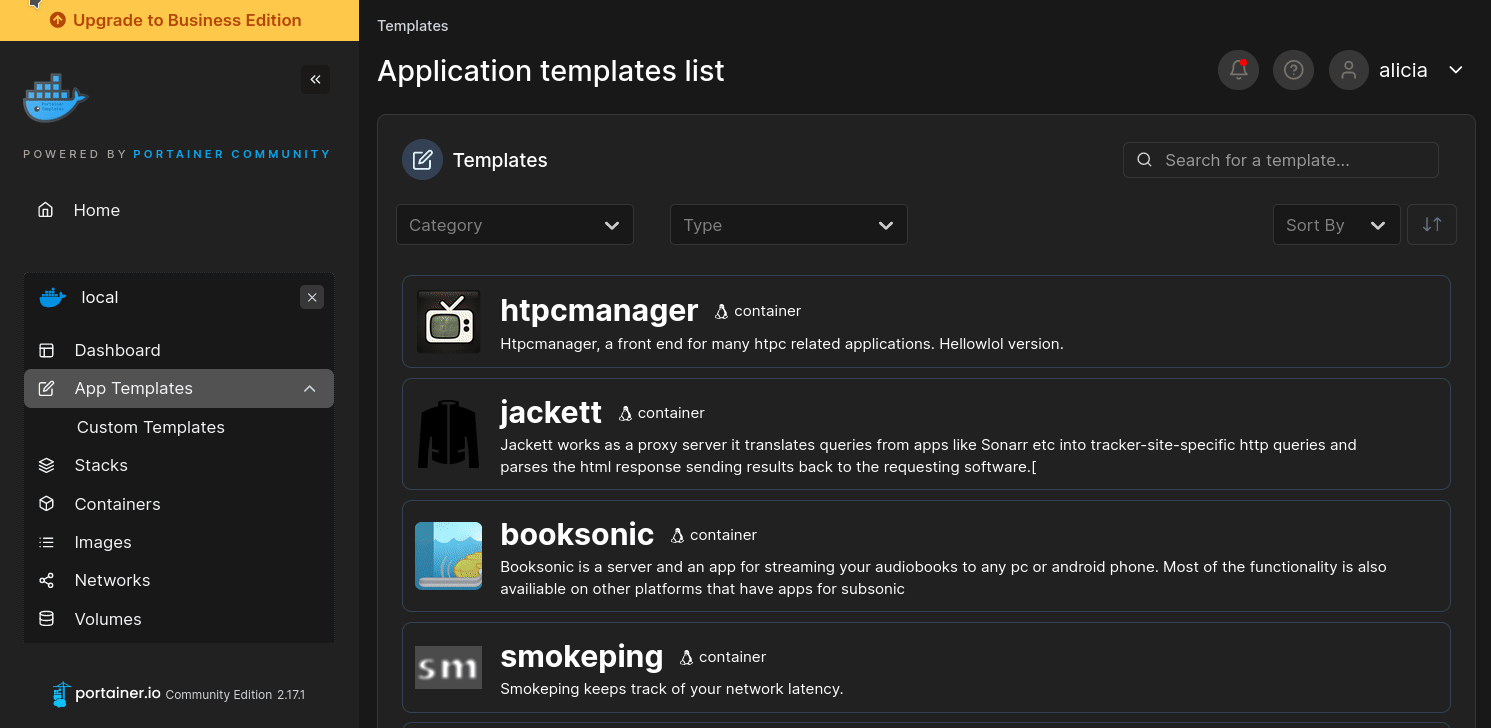
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select Excaliself, fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
Original stackfile
The compose file this template deploys, straight from its repo:
# Portainer deploy: the stack portainer-template.json points at.
# Same as docker-compose.yaml, except BASE_URL is required: Portainer users
# open the app from another machine, so the localhost default breaks sign-in.
# CI checks that both files render the same stack.
services:
  db:
    image: postgres:17-alpine
    environment:
      POSTGRES_USER: ${POSTGRES_USER:-excaliself}
      POSTGRES_PASSWORD: ${POSTGRES_PASSWORD:?Set POSTGRES_PASSWORD in .env}
      POSTGRES_DB: ${POSTGRES_DB:-excaliself}
    volumes:
      - pgdata:/var/lib/postgresql/data
    healthcheck:
      test: ["CMD-SHELL", "pg_isready -U $${POSTGRES_USER} -d $${POSTGRES_DB}"]
      interval: 5s
      timeout: 5s
      retries: 10
    restart: unless-stopped

  excaliself:
    image: ghcr.io/maciekzygmunt/excaliself:${EXCALISELF_VERSION:-latest}
    ports:
      - "${EXCALISELF_PORT:-3000}:3000"
    environment:
      DATABASE_URL: postgresql://${POSTGRES_USER:-excaliself}:${POSTGRES_PASSWORD}@db:5432/${POSTGRES_DB:-excaliself}
      BETTER_AUTH_SECRET: ${BETTER_AUTH_SECRET:?Set BETTER_AUTH_SECRET in .env}
      BASE_URL: ${BASE_URL:?Set BASE_URL to the address you open Excaliself at, e.g. http://192.168.1.10:3000}
      TRUSTED_ORIGINS: ${TRUSTED_ORIGINS:-}
      # Optional single sign-on, see https://excaliself.com/docs/single-sign-on/
      GOOGLE_CLIENT_ID: ${GOOGLE_CLIENT_ID:-}
      GOOGLE_CLIENT_SECRET: ${GOOGLE_CLIENT_SECRET:-}
      MICROSOFT_CLIENT_ID: ${MICROSOFT_CLIENT_ID:-}
      MICROSOFT_CLIENT_SECRET: ${MICROSOFT_CLIENT_SECRET:-}
      MICROSOFT_TENANT_ID: ${MICROSOFT_TENANT_ID:-}
      OIDC_ISSUER: ${OIDC_ISSUER:-}
      OIDC_CLIENT_ID: ${OIDC_CLIENT_ID:-}
      OIDC_CLIENT_SECRET: ${OIDC_CLIENT_SECRET:-}
      OIDC_NAME: ${OIDC_NAME:-}
      SSO_ALLOWED_DOMAINS: ${SSO_ALLOWED_DOMAINS:-}
      IMAGE_UPLOADS_PER_MINUTE: ${IMAGE_UPLOADS_PER_MINUTE:-}
    depends_on:
      db:
        condition: service_healthy
    restart: unless-stopped

volumes:
  pgdata:
Or deploy it directly from the source:
git clone https://github.com/maciekzygmunt/excaliself
cd excaliself
docker compose -f docker-compose.portainer.yaml up -d
More install options in our documentation, or see maciekzygmunt/excaliself for app-specific guidance.
Container Documentation
db Documentation
The PostgreSQL object-relational database system provides reliability and data integrity.
Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs <container> - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Image won't pull
Test the pull directly on the host: docker pull postgres:17-alpine
- "manifest unknown" means the tag no longer exists.
- "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect <container> --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Stack won't deploy
Compose stacks fail fast on small mistakes, and Portainer shows the reason just above the editor.
- YAML only accepts spaces for indentation, a single tab breaks the whole file.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue on maciekzygmunt/excaliself
- Template not working: Open an issue on maciekzygmunt/excaliself
- This website not working: Open an issue on lissy93/portainer-templates
A Compose stack
Excaliself is a Compose stack, a set of containers (2 of them) defined in one file and brought up together by Portainer, then started and stopped as a single app.
The services
This stack is built from 2 containers that run side by side. Here's each one, with the image it runs and anything it waits for first:
dbrunspostgres:17-alpineexcaliselfrunsghcr.io/maciekzygmunt/excaliself:latest, starts after db
Volumes
A volume is where Excaliself keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/var/lib/postgresql/datakept in thepgdatavolume Docker manages
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. Excaliself takes 18 of them, and 3 need a value before it'll start properly:
POSTGRES_USER, defaults toexcaliselfPOSTGRES_PASSWORD, needs a valuePOSTGRES_DB, defaults toexcaliselfDATABASE_URL, defaults topostgresql://excaliself:POSTGRES_PASSWORD@db:5432/excaliselfBETTER_AUTH_SECRET, needs a valueBASE_URL, needs a valueTRUSTED_ORIGINS, pulled from your own environmentGOOGLE_CLIENT_ID, pulled from your own environmentGOOGLE_CLIENT_SECRET, pulled from your own environmentMICROSOFT_CLIENT_ID, pulled from your own environmentMICROSOFT_CLIENT_SECRET, pulled from your own environmentMICROSOFT_TENANT_ID, pulled from your own environmentOIDC_ISSUER, pulled from your own environmentOIDC_CLIENT_ID, pulled from your own environmentOIDC_CLIENT_SECRET, pulled from your own environmentOIDC_NAME, pulled from your own environmentSSO_ALLOWED_DOMAINS, pulled from your own environmentIMAGE_UPLOADS_PER_MINUTE, pulled from your own environment
Restart policy
The restart policy here is unless-stopped, so Docker restarts Excaliself after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Networking
Portainer puts these services on one shared private network, so they can find each other by name (like db) while only the ports above are open to you.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Open source license
Excaliself is open source, released under the MIT license. In plain terms the code is out in the open, so you're free to run it and change it to fit what you need.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set Excaliself up. Add the template list to Portainer once, then deploying Excaliself is a click rather than a wall of config.