
![Vaultwarden (stack)]() Vaultwarden (stack)
Vaultwarden - the Bitwarden-compatible server in Rust: the official Bitwarden browser extensions, mobile and desktop apps, and CLI all connect to it unchanged. One ~tiny container + a 2 GB volume (SQLite, attachments, keys).
Image details
Configuration
TypeComposelinuxvaultwarden/server:1.36.05000:5000/data : vwdataROCKET_PORT=5000DOMAIN=${DOMAIN:-http://localhost:5000}SIGNUPS_ALLOWED=${SIGNUPS_ALLOWED:-true}ADMIN_TOKEN=${ADMIN_TOKEN:-}unless-stoppedTemplate by deployable-sh·Source
Report issueStandalone Install
Select an install method, to see config/commands for deploying Vaultwarden (stack)
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
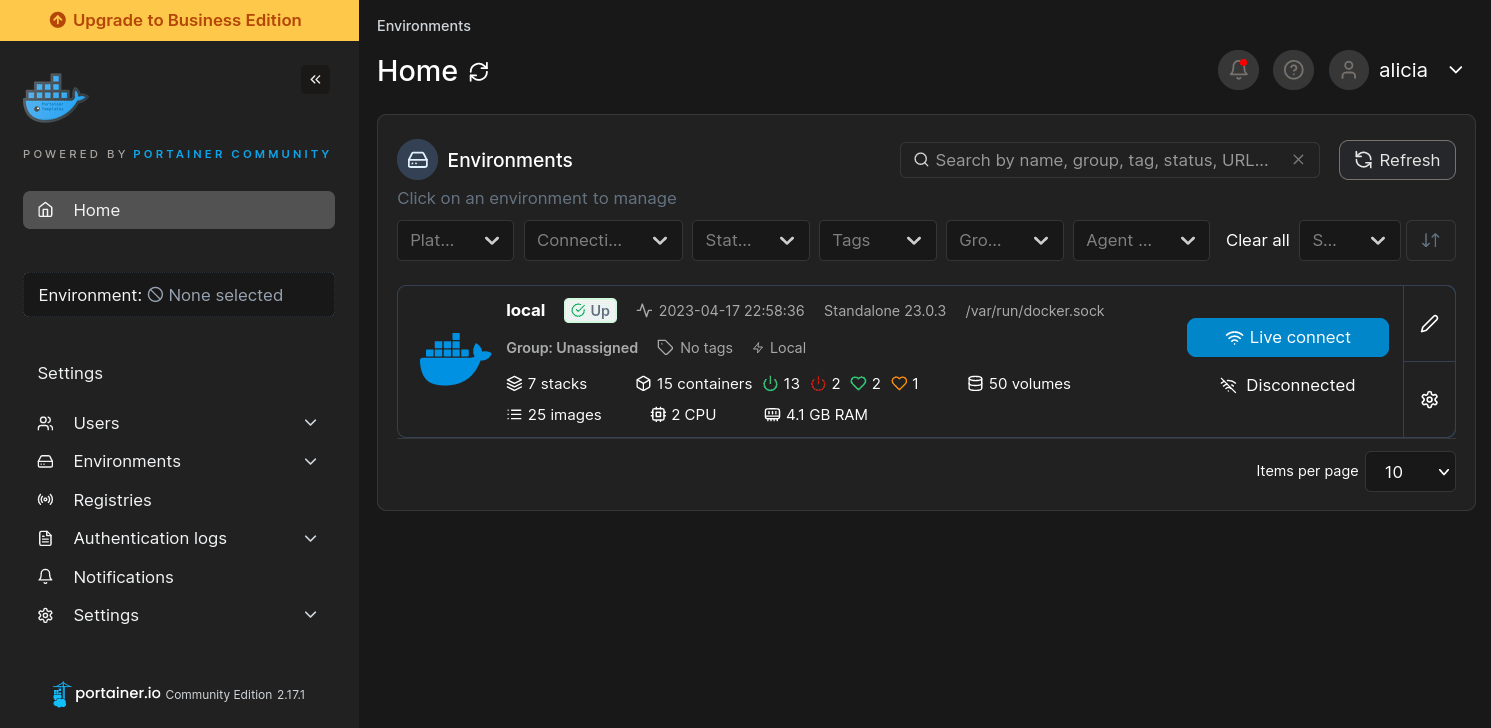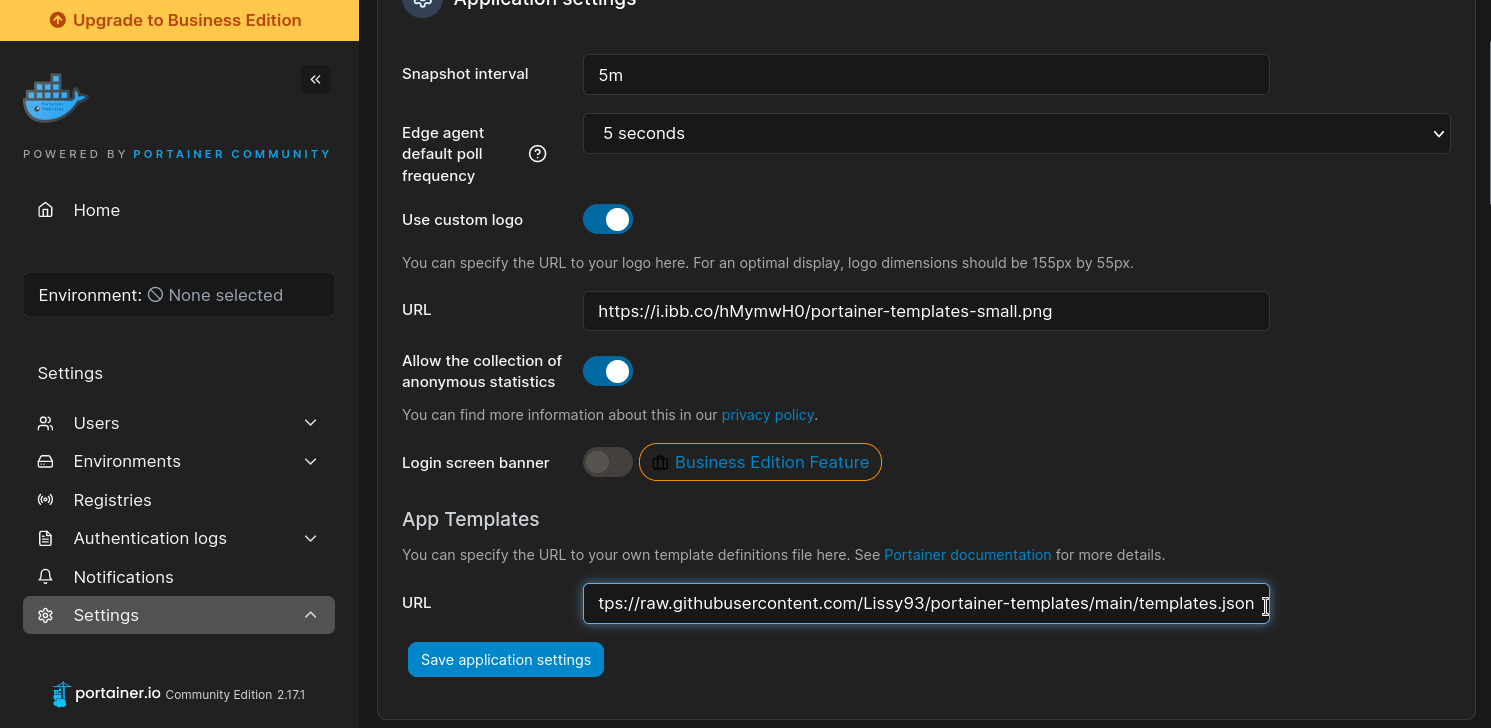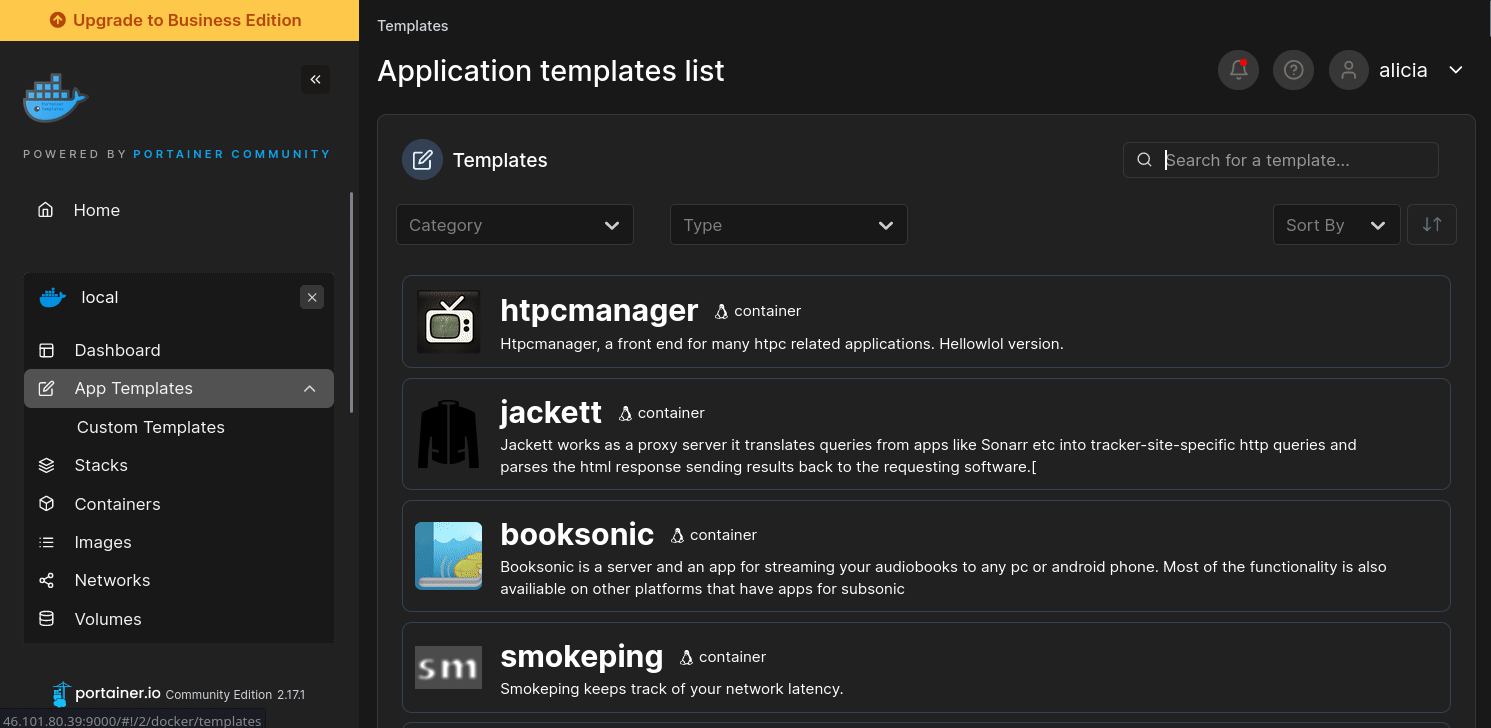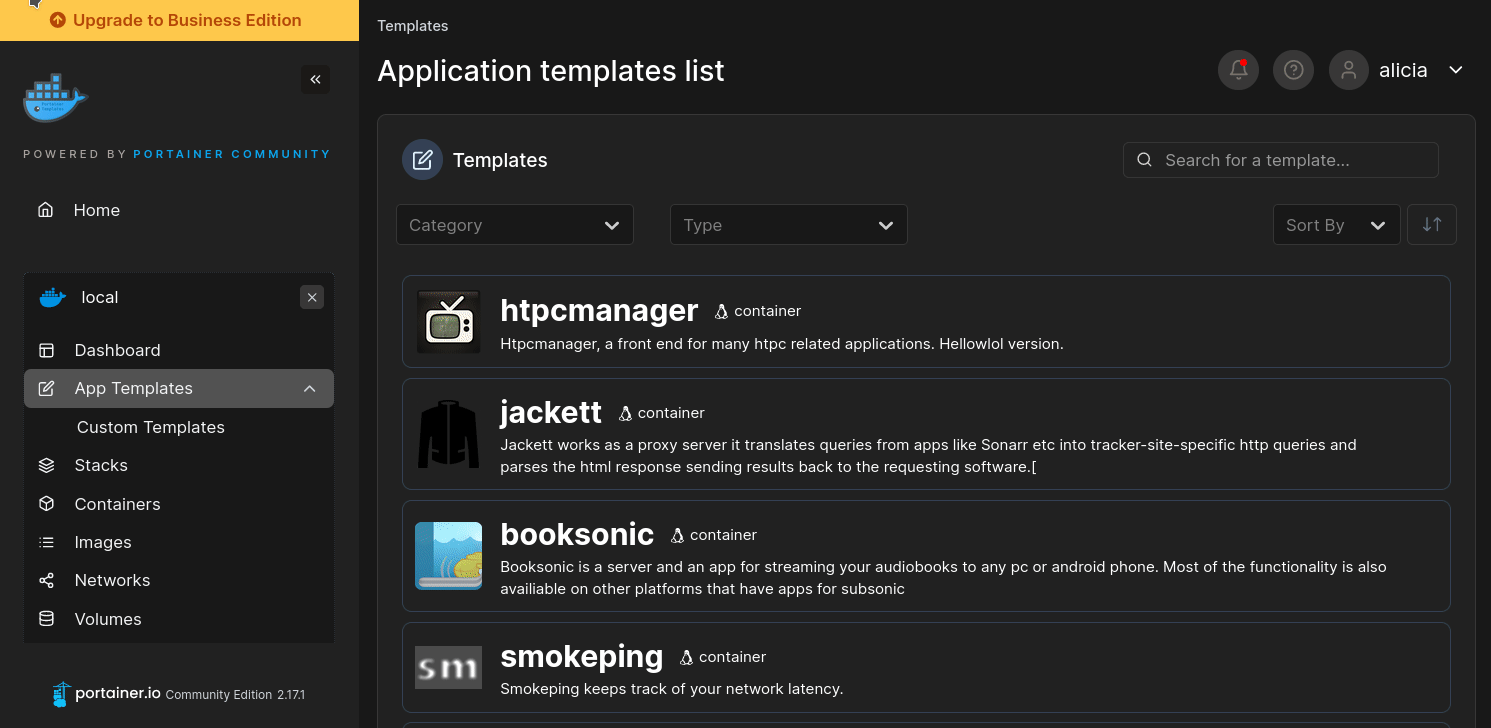
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select Vaultwarden (stack), fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
Original stackfile
The compose file this template deploys, straight from its repo:
name: vaultwarden

services:
  vaultwarden:
    image: vaultwarden/server:1.36.0
    restart: unless-stopped
    environment:
      ROCKET_PORT: "5000"
      DOMAIN: ${DOMAIN:-http://localhost:5000}
      SIGNUPS_ALLOWED: ${SIGNUPS_ALLOWED:-true}
      ADMIN_TOKEN: ${ADMIN_TOKEN:-}
    ports:
      - "5000:5000"
    volumes:
      - vwdata:/data

volumes:
  vwdata:
Or deploy it directly from the source:
git clone https://github.com/deployable-sh/stacks
cd stacks
docker compose -f vaultwarden/compose.yaml up -d
More install options in our documentation.
Alternative implementation of the Bitwarden server API written in Rust and compatible with upstream Bitwarden clients, perfect for self-hosted deployment where running the official resource-heavy service might not be ideal.
📢 Note: This project was known as BitwardenRS and has been renamed to separate itself from the official Bitwarden server in the hopes of avoiding confusion and trademark/branding issues. Please see #1642 for more explanation.


Image is based on Rust implementation of Bitwarden API.
This project is not associated with the Bitwarden project nor 8bit Solutions LLC.
⚠️IMPORTANT⚠️: When using this server, please report any bugs or suggestions to us directly (look at the bottom of this page for ways to get in touch), regardless of whatever clients you are using (mobile, desktop, browser...). DO NOT use the official support channels.
---Features
Basically full implementation of Bitwarden API is provided including:Organizations support Attachments Vault API support Serving the static files for Vault interface Website icons API Authenticator and U2F support YubiKey and Duo support
Installation
Pull the docker image and mount a volume from the host for persistent storage:docker pull vaultwarden/server:latest
docker run -d --name vaultwarden -v /vw-data/:/data/ -p 80:80 vaultwarden/server:latestIMPORTANT: Some web browsers, like Chrome, disallow the use of Web Crypto APIs in insecure contexts. In this case, you might get an error like
Cannot read property 'importKey'. To solve this problem, you need to access the web vault from HTTPS. This can be configured in vaultwarden directly or using a third-party reverse proxy (some examples).
If you have an available domain name, you can get HTTPS certificates with Let's Encrypt, or you can generate self-signed certificates with utilities like mkcert. Some proxies automatically do this step, like Caddy (see examples linked above).
Usage
See the vaultwarden wiki for more information on how to configure and run the vaultwarden server.Get in touch
To ask a question, offer suggestions or new features or to get help configuring or installing the software, please use the forum.If you spot any bugs or crashes with vaultwarden itself, please create an issue. Make sure there aren't any similar issues open, though!
If you prefer to chat, we're usually hanging around at #vaultwarden:matrix.org room on Matrix. Feel free to join us!
Sponsors
Thanks for your contribution to the project!Serve Vaultwarden (stack) on your own domain behind Caddy, Nginx or Traefik. Fill in your domain and copy the result. It's a starting point, some apps need their own base URL or extra headers set too.
Proxying vaultwarden-stack.example.com to http://vaultwarden:5000
Add this to your Caddyfile
vaultwarden-stack.example.com {
	reverse_proxy http://vaultwarden:5000
}Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs <container> - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Port already in use
If deployment fails with "Bind for 0.0.0.0:5000 failed: port is already allocated", something else on your server is using that port.
- Find what's using it:
sudo ss -tlnp | grep :5000 - Stop the other service, or pick a different host port. In
5000:5000only the left number is yours to change, the right one belongs to the app.
Running but the page won't load
The container is up but nothing appears in your browser.
- Use your server's real IP:
http://your-server-ip:5000. The 0.0.0.0 link Portainer shows isn't a real address. - Give it a minute after first deploy, vaultwarden can take a while to initialise.
- Make sure your firewall allows the port, e.g.
sudo ufw allow 5000
Image won't pull
Test the pull directly on the host: docker pull vaultwarden/server:1.36.0
- "manifest unknown" means the tag no longer exists.
- "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- This image supports:
amd64, arm64, arm/v7, arm/v6 - Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect <container> --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Stack won't deploy
Compose stacks fail fast on small mistakes, and Portainer shows the reason just above the editor.
- YAML only accepts spaces for indentation, a single tab breaks the whole file.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue within vaultwarden's repo
- Template not working: Open an issue on deployable-sh/stacks
- This website not working: Open an issue on lissy93/portainer-templates
A Compose stack
Vaultwarden (stack) is a Compose stack, a set of containers defined in one file and brought up together by Portainer, then started and stopped as a single app.
The app image
An image is the app packed up ready to go, everything Vaultwarden (stack) needs bundled into one download. This template pulls vaultwarden/server:1.36.0, which Docker fetches once (about 86 MB) and then starts your own copy from.
Where the image comes from
Docker pulls its images from registries, public libraries of ready-built apps. Vaultwarden (stack)'s comes from Docker Hub, published by vaultwarden.
Version tags
The bit after the colon in the image name is the version tag. This one pins 1.36.0, so every redeploy gives you that exact build until you bump it yourself.
Which machines it runs on
Every image is built for particular CPU types. This one ships for amd64, arm64, arm/v7, arm/v6, so it runs on both regular x86 servers and ARM boards like a Raspberry Pi.
Ports
A port is the door the app answers on. A mapping like 5000:5000 means it's reachable on port 5000 of your server, where the left number is yours to change and the right one belongs to the app. It opens:
5000:5000
Volumes
A volume is where Vaultwarden (stack) keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/datakept in thevwdatavolume Docker manages
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. Vaultwarden (stack) takes 4 of them, all with defaults you can leave alone or tweak:
ROCKET_PORT, defaults to5000DOMAIN, defaults tohttp://localhost:5000. Full public URL of the instance (https in production - WebAuthn and email links depend on it).SIGNUPS_ALLOWED, defaults totrue. Close after creating your accounts (org invitations still work).ADMIN_TOKEN, pulled from your own environment. Optional admin page token - argon2 PHC hash, NOT plaintext: docker run --rm -it vaultwarden/server /vaultwarden hash --preset owasp In .env files, keep the hash
Restart policy
The restart policy here is unless-stopped, so Docker restarts Vaultwarden (stack) after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Networking
Nothing custom is set, so Vaultwarden (stack) sits on Docker's default bridge network: its own private space that reaches the outside world only through the ports it publishes.
Container name
Once it's deployed, Portainer names the container vaultwarden. That's what you'll spot in the containers list and use in commands like docker logs vaultwarden.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set Vaultwarden (stack) up. Add the template list to Portainer once, then deploying Vaultwarden (stack) is a click rather than a wall of config.