
![RustFS]() RustFS
Stack
S3-compatible object storage written in Rust, an open-source alternative to MinIO, with a web console for browsing buckets and managing users, policies and access keys. Source: https://github.com/rustfs/rustfs
Image details
Source details
Configuration
TypeComposelinuxrustfs/rustfs:latest${RUSTFS_API_PORT:-9010}:9000${RUSTFS_CONSOLE_PORT:-9011}:9001/data : rustfs-dataRUSTFS_ACCESS_KEY=${RUSTFS_ADMIN_USER:-admin}RUSTFS_SECRET_KEY=${RUSTFS_SECRET_KEY:?Set a secret key}RUSTFS_OBS_LOG_DIRECTORY=RUSTFS_ADMIN_USER=adminRUSTFS_API_PORT=9010RUSTFS_CONSOLE_PORT=9011unless-stoppedTemplate by NotAFlightRisk·Source
Report issueNotes
http://<your-host>:9011 (or whichever port you picked) and log in with the admin user as the account (admin unless you changed it) and the secret key as the key. S3 clients and SDKs go to http://<your-host>:9010, with path-style addressing and region us-east-1. Buckets start private. Rather than hand the admin's keys to other apps, make them their own user under Users. Changing the secret key on the form and redeploying changes the admin's password, and other users carry on as they were. Everything lives in the rustfs-data volume, as a single drive with no redundancy, so back it up like any other data. Docs: docs.rustfs.comStandalone Install
Select an install method, to see config/commands for deploying RustFS
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select RustFS, fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
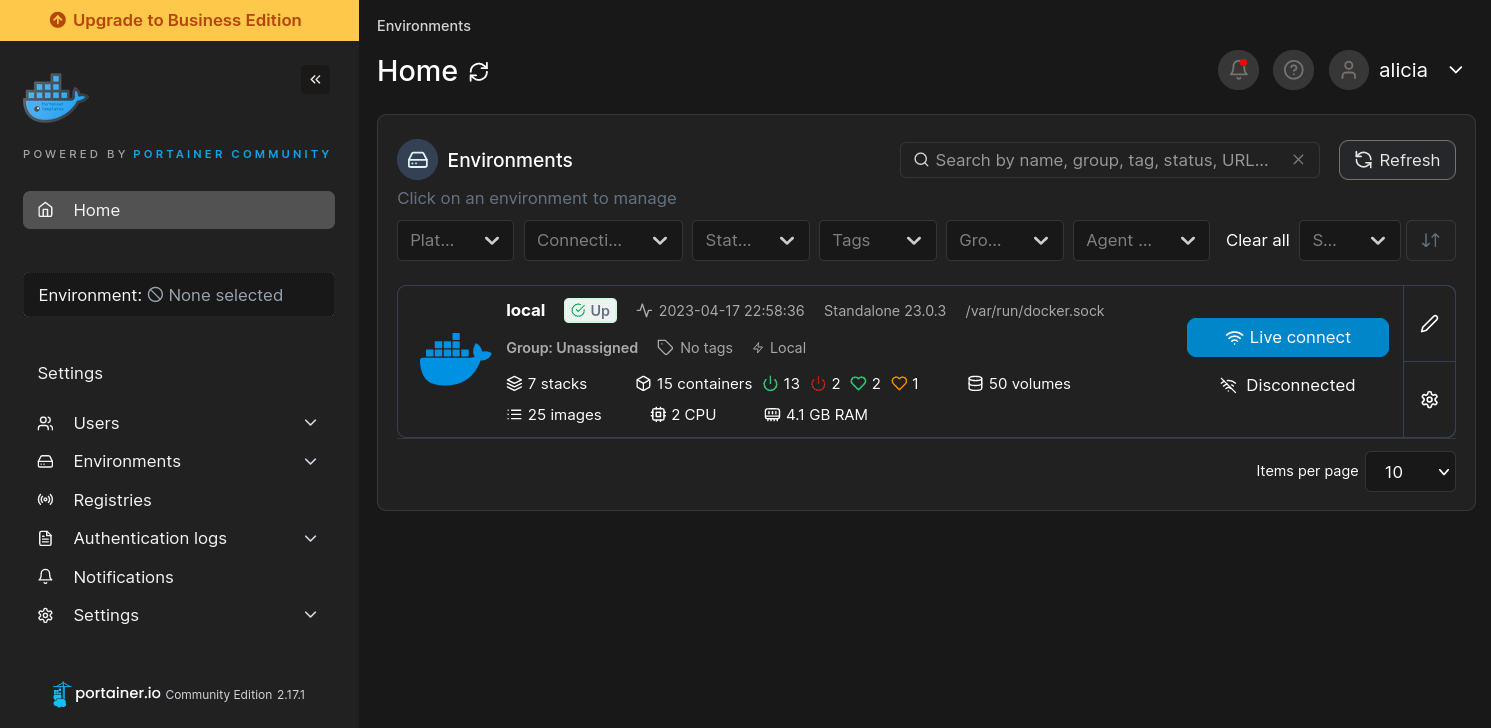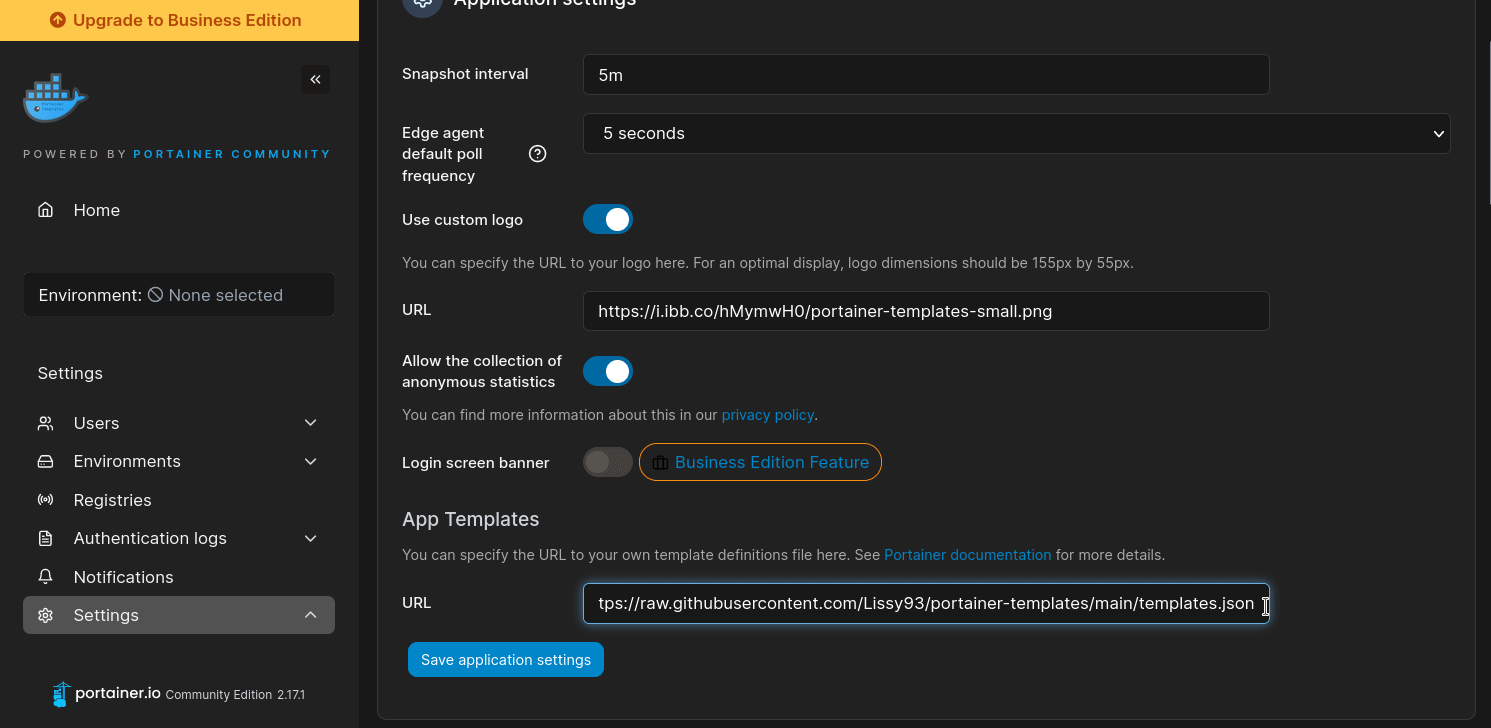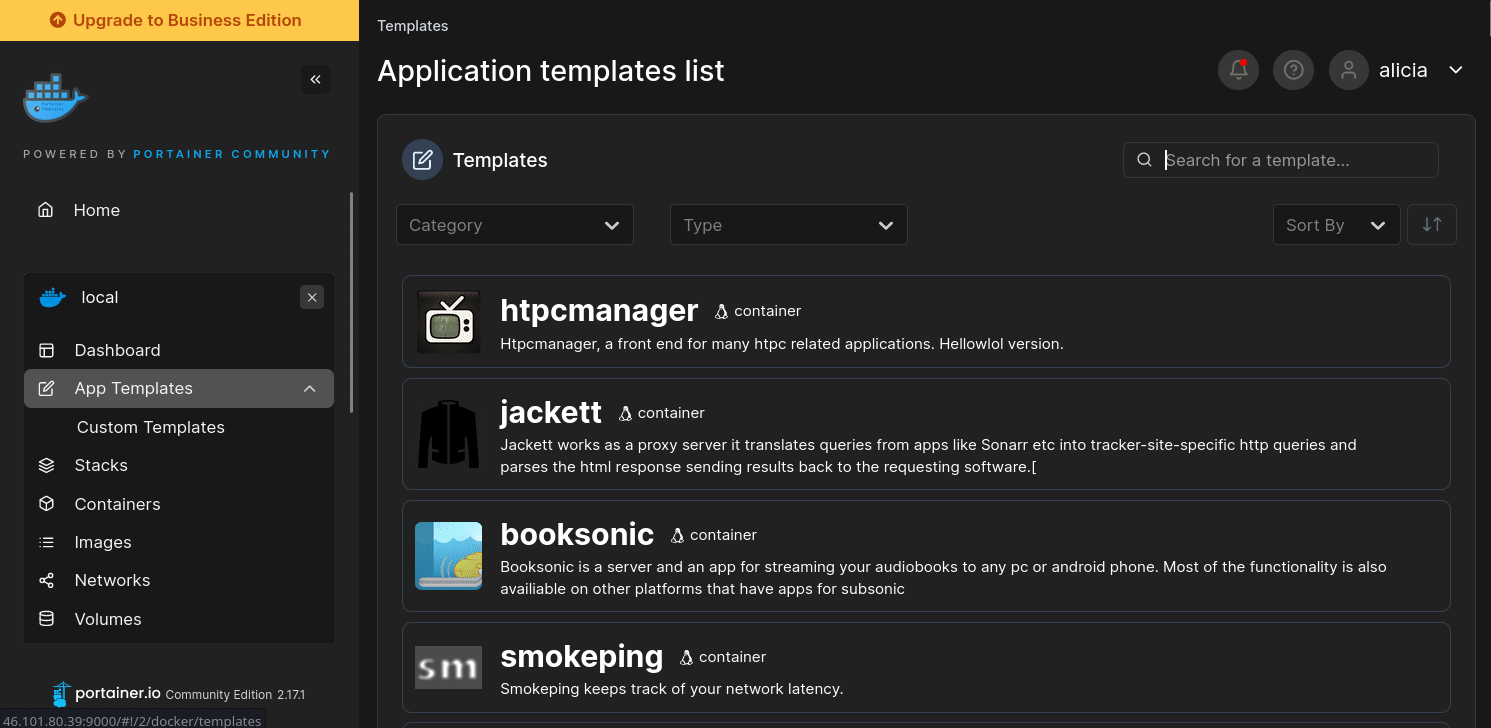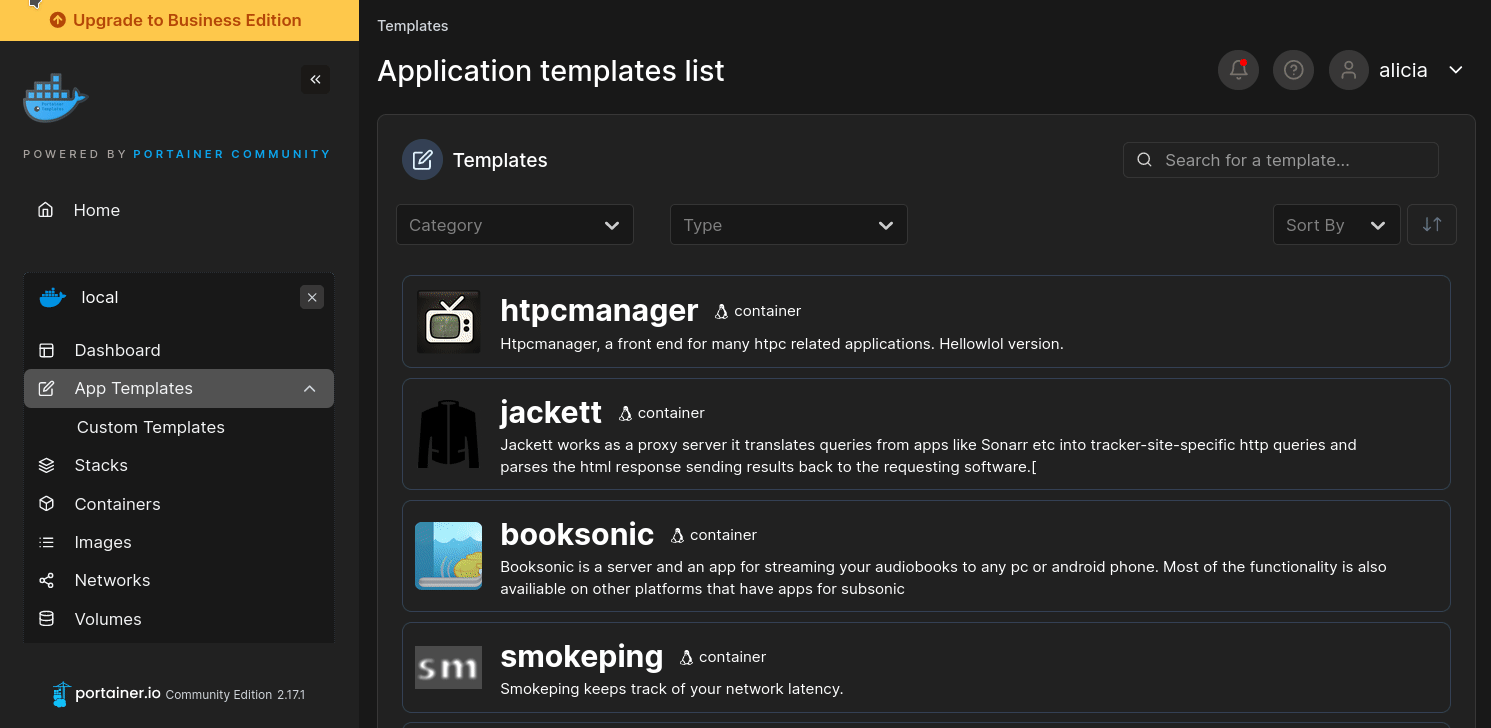
Original stackfile
The compose file this template deploys, straight from its repo:
services:
  rustfs:
    image: rustfs/rustfs:latest
    restart: unless-stopped
    ports:
      - "${RUSTFS_API_PORT:-9010}:9000"
      - "${RUSTFS_CONSOLE_PORT:-9011}:9001"
    environment:
      RUSTFS_ACCESS_KEY: ${RUSTFS_ADMIN_USER:-admin}
      RUSTFS_SECRET_KEY: ${RUSTFS_SECRET_KEY:?Set a secret key}
      RUSTFS_OBS_LOG_DIRECTORY: ""
    volumes:
      - rustfs-data:/data

volumes:
  rustfs-data:
Or deploy it directly from the source:
git clone https://github.com/NotAFlightRisk/portainer-templates-extras
cd portainer-templates-extras
docker compose -f apps/rustfs/compose.yml up -d
More install options in our documentation, or see rustfs/rustfs for app-specific guidance.
RustFS is a high-performance, distributed object storage system built in Rust.
 |
 |
 |
 |
 |
 |

Getting Started · Docs · Bug reports · Discussions
English | 简体中文 | Deutsch | Español | français | 日本語 | 한국어 | Portuguese | Русский
RustFS is a high-performance, distributed object storage system built in Rust—one of the most loved programming languages worldwide. RustFS combines the simplicity of MinIO with the memory safety and raw performance of Rust. It offers broad S3 API compatibility for supported features, is completely open-source, and is optimized for data lakes, AI, and big data workloads.
Unlike other storage systems, RustFS is released under the permissible Apache 2.0 license, avoiding the restrictions of AGPL. With Rust as its foundation, RustFS delivers superior speed and secure distributed features for next-generation object storage.
Feature & Status
- High Performance: Built with Rust to ensure maximum speed and resource efficiency.
- Distributed Architecture: Scalable and fault-tolerant design suitable for large-scale deployments.
- S3 Compatibility: Seamless integration with common S3-compatible applications and tools; current coverage is tracked in the S3 compatibility matrix.
- OpenStack Swift API: Native support for Swift protocol with Keystone authentication.
- OpenStack Keystone Integration: Native support for OpenStack Keystone authentication with X-Auth-Token headers.
- Data Lake Support: Optimized for high-throughput big data and AI workloads.
- Open Source: Licensed under Apache 2.0, encouraging unrestricted community contributions and commercial usage.
- User-Friendly: Designed with simplicity in mind for easy deployment and management.
Status legend: ✅ Available — shipped and covered by CI gates; 🧪 Preview — shipped behind an opt-in flag or with a bounded compatibility claim.
| Feature | Status | Feature | Status |
|---|---|---|---|
| S3 Core Features | ✅ Available | Distributed Mode | ✅ Available |
| Upload / Download | ✅ Available | Single Node Mode | ✅ Available |
| Versioning | ✅ Available | Bitrot Protection | ✅ Available |
| Object Lock (WORM) | ✅ Available | Healing & Scanner | ✅ Available |
| Server-Side Encryption | ✅ Available | Pool Expansion / Decommission | ✅ Available |
| RustFS KMS | ✅ Available | Bucket Replication | ✅ Available |
| Lifecycle Management (ILM) | ✅ Available | Site Replication | ✅ Available |
| ILM Tiering (Remote S3) | ✅ Available | Bucket Quota | ✅ Available |
| S3 Select | ✅ Available | Event Notifications | ✅ Available |
| S3 Tables (Iceberg REST) | 🧪 Preview | Audit Logging | ✅ Available |
| IAM / Policies | ✅ Available | Logging & Observability | ✅ Available |
| OIDC / SSO | ✅ Available | Web Console | ✅ Available |
| Keystone Auth | ✅ Available | K8s Helm Charts | ✅ Available |
| Swift API | ✅ Available | FTPS / WebDAV | ✅ Available |
| Multi-Tenancy | ✅ Available | SFTP | ✅ Available |
| MinIO On-Disk Compatibility | 🧪 Preview |
Notes:
- RustFS KMS: Vault (KV2 / Transit) and AWS KMS backends are supported for production. The
LocalandStaticbackends are for development and testing only. See KMS backend security properties. - Swift API / SFTP: opt-in cargo features (
--features swift,--features sftp, orfull). FTPS and WebDAV are enabled in the default build. - S3 Tables: ships as an Iceberg REST Catalog with automated PyIceberg and DuckDB coverage; other engines and vendor profiles carry bounded claims listed in the S3 Tables support matrix.
- MinIO On-Disk Compatibility: gated behind the
rio-v2feature and not part of the default build. Objects MinIO encrypted are not readable by RustFS. See MinIO file-format interoperability.
RustFS vs MinIO Performance
Stress Test Environment:| Type | Parameter | Remark |
|---|---|---|
| CPU | 2 Core | Intel Xeon (Sapphire Rapids) Platinum 8475B, 2.7/3.2 GHz |
| Memory | 4GB | |
| Network | 15Gbps | |
| Drive | 40GB x 4 | IOPS 3800 / Drive |
RustFS vs Other Object Storage
| Feature | RustFS | Other Object Storage |
|---|---|---|
| Console Experience | Powerful Console Comprehensive management interface. | Basic / Limited Console Often overly simple or lacking critical features. |
| Language & Safety | Rust-based Memory safety by design. | Go or C-based Potential for memory GC pauses or leaks. |
| Data Sovereignty | No Telemetry / Full Compliance Guards against unauthorized cross-border data egress. Compliant with GDPR (EU/UK), CCPA (US), and APPI (Japan). | Potential Risk Possible legal exposure and unwanted data telemetry. |
| Licensing | Permissive Apache 2.0 Business-friendly, no "poison pill" clauses. | Restrictive AGPL v3 Risk of license traps and intellectual property pollution. |
| Compatibility | S3-Compatible Core Works with common S3-compatible clients, with coverage tracked in the compatibility matrix. | Variable Compatibility May lack support for local cloud vendors or specific APIs. |
| Edge & IoT | Strong Edge Support Ideal for secure, innovative edge devices. | Weak Edge Support Often too heavy for edge gateways. |
| Risk Profile | Enterprise Risk Mitigation Clear IP rights and safe for commercial use. | Legal Risks Intellectual property ambiguity and usage restrictions. |
Staying ahead
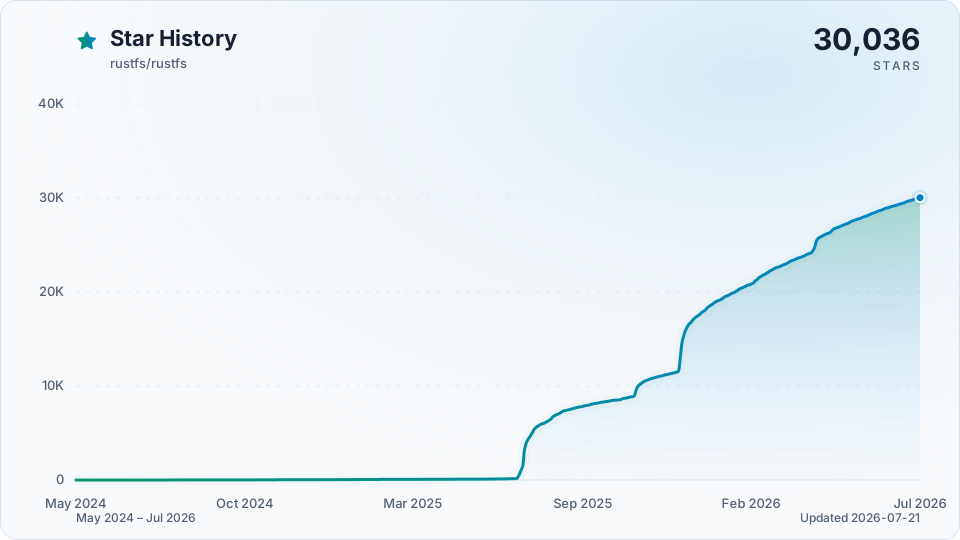
Star RustFS on GitHub and be instantly notified of new releases.Quickstart
Important — Pool expansion notice:- A single-node single-drive (SNSD) deployment is supported only as a standalone local path. It cannot expand in place or be added as a Pool. To move to a multi-drive topology, create a new deployment and migrate data through S3.
- Keep an existing multi-drive Pool's endpoints and Erasure Set width unchanged; expand by appending a new Pool. With ellipsis-based expansion, every Pool argument must contain an ellipsis expression and expand to at least two drive endpoints.
- Single-node multi-drive Pools and multi-node Pools with one drive per node are allowed, subject to valid Erasure Set geometry and EC settings; acceptance does not guarantee host-failure tolerance.
To get started with RustFS, follow these steps:
- One-click Installation (Option 1)
curl -O https://rustfs.com/install_rustfs.sh && bash install_rustfs.sh- Docker Quick Start (Option 2)
The RustFS container runs as a non-root user rustfs (UID/GID 10001:10001). If you bind-mount host directories with Docker or Compose, every mounted path must be writable by that user, otherwise startup may fail with permission denied errors. This applies to data directories, log directories, and TLS certificate directories when RUSTFS_TLS_PATH is enabled.# Create data and logs directories
mkdir -p data logs
# Change the owner of these directories
chown -R 10001:10001 data logs
# Using latest version
docker run -d -p 9000:9000 -p 9001:9001 -v $(pwd)/data:/data -v $(pwd)/logs:/logs rustfs/rustfs:latest
# Using specific version
docker run -d -p 9000:9000 -p 9001:9001 -v $(pwd)/data:/data -v $(pwd)/logs:/logs rustfs/rustfs:1.0.1If you use podman instead of docker, you can install the RustFS with the below command
# Create data and logs directories
mkdir -p data logs

# Run the container (podman will automatically set the folders ownership)
podman run -d -p 9000:9000 -p 9001:9001 -v $(pwd)/data:/data:Z,U -v $(pwd)/logs:/logs:Z,U rustfs/rustfs:latest
If you enable TLS with a bind-mounted certificate directory, prepare that mount the same way:
mkdir -p certs
chown -R 10001:10001 certs
You can also use Docker Compose. Using the
docker-compose-simple.yml file in the root directory:docker compose -f docker-compose-simple.yml up -dBefore running Compose with host bind mounts:
- Ensure every mounted host path is writable by
10001:10001. - If you enable TLS, ensure the certificate mount for
/opt/tlsis also readable by10001:10001. - If matching host ownership is not practical, run the
rustfsservice withuser: "<host-uid>:<host-gid>"instead. docker-compose-simple.ymlincludes avolume-permission-helperservice for named volumes.docker-compose-simple.ymlrelies on you to prepare bind-mounted host paths in advance.
Similarly, you can run the command with podman
podman compose -f docker-compose-simple.yml up -dWebhook notification quick start (Docker):
docker run -d --name rustfs -p 9000:9000 \
  -e RUSTFS_NOTIFY_ENABLE=true \
  -e RUSTFS_NOTIFY_WEBHOOK_ENABLE_PRIMARY=on \
  -e RUSTFS_NOTIFY_WEBHOOK_ENDPOINT_PRIMARY=http://<host-ip>:3020/webhook \
  -e RUSTFS_NOTIFY_WEBHOOK_QUEUE_DIR_PRIMARY=/tmp/rustfs-events \
  -e RUSTFS_OUTBOUND_ALLOW_ORIGINS=http://<host-ip>:3020 \
  rustfs/rustfs:latest
Notes:
RUSTFS_NOTIFY_ENABLE=trueenables the global notify module switch.- For ARN
arn:rustfs:sqs::primary:webhook, use instance-scoped env vars with_PRIMARY. - If queue dir is omitted, the official image maps
/opt/rustfs/eventsinto the persistent/datavolume so it is writable by the runtime user and pending events survive container recreation. Overridequeue_dirwhen using another deployment layout. RUSTFS_NOTIFY_WEBHOOK_SKIP_TLS_VERIFY_PRIMARYdefaults tofalse; enabling it skips webhook TLS certificate verification, allows MITM attacks, and emits a startup warning. PreferRUSTFS_NOTIFY_WEBHOOK_CLIENT_CA_PRIMARYfor private CAs.- Since
1.0.0-beta.11, webhook endpoints on private or container networks
Docker Compose service names, host.docker.internal, RFC 1918 addresses) are
blocked unless their exact scheme://host:port origin is listed in
RUSTFS_OUTBOUND_ALLOW_ORIGINS (the origin only, without the path). See
Outbound Connection Policy.NOTE: We recommend reviewing the
docker-compose.yml file before running. It defines several services including Grafana, Prometheus, and Jaeger, which are helpful for RustFS observability. If you wish to start Redis or Nginx containers, you can specify the corresponding profiles.3\. Build from Source (Option 3) - Advanced Users
For developers who want to build RustFS Docker images from source with multi-architecture support:# Build multi-architecture images locally
./docker-buildx.sh
# Build a single-platform image locally
./docker-buildx.sh -p linux/amd64
# Build and push to registry
./docker-buildx.sh --push
# Build specific version
./docker-buildx.sh --release 1.0.1 --push
# Build for custom registry
./docker-buildx.sh --registry your-registry.com --namespace yourname --pushThe
docker-buildx.sh script supports:- Multi-architecture builds:
linux/amd64,linux/arm64 - Automatic version detection: Uses git tags or commit hashes
- Registry flexibility: Supports Docker Hub, GitHub Container Registry, etc.
- Build optimization: Includes caching and parallel builds
You can also use Make targets for convenience:
make docker-buildx                    # Build locally
make docker-buildx-push               # Build and push
make docker-buildx-version VERSION=1.0.1  # Build specific version
make help-docker                      # Show all Docker-related commands
Heads-up (macOS cross-compilation): macOS keeps the default
ulimit -n at 256, so cargo zigbuild or ./build-rustfs.sh --platform ... may fail with ProcessFdQuotaExceeded when targeting Linux. The build script attempts to raise the limit automatically, but if you still see the warning, run ulimit -n 4096 (or higher) in your shell before building.4\. Build with Helm Chart (Option 4) - Cloud Native
Follow the instructions in the Helm Chart README to install RustFS on a Kubernetes cluster.For scanner pacing, cycle budgets, bitrot cadence, lifecycle transition status, and single-node single-disk idle CPU tuning, see Scanner Runtime Controls. For repeatable scanner-pressure validation, see Scanner Benchmark Runbook. For drive timeout knobs on slow storage — including the walk stall budget that governs
ListObjects on large prefixes — see
Drive Timeout Tuning.5\. Nix Flake (Option 5)
If you have Nix with flakes enabled:# Run directly without installing
nix run github:rustfs/rustfs
# Build the binary
nix build github:rustfs/rustfs
./result/bin/rustfs --help
# Or from a local checkout
nix build
nix runThe flake also exports a NixOS module and the RustFS
rc client. Add the
module to your system and provide credentials through runtime files (for
example, sops-nix or agenix) so secrets are never stored in the Nix store:imports = [ inputs.rustfs.nixosModules.rustfs ];
services.rustfs = {
enable = true;
accessKeyFile = "/run/secrets/rustfs-access-key";
secretKeyFile = "/run/secrets/rustfs-secret-key";
volumes = [ "/var/lib/rustfs" ];
};Install the S3-compatible client with
nix profile install github:rustfs/rustfs#rustfs-client (the executable is named
rc), or use inputs.rustfs.packages.${pkgs.system}.rustfs-client in a system
configuration.6\. X-CMD (Option 6)
If you are an x-cmd user:# Run directly without installing
x rustfs
# Download the binary and install it to the global environment
x env use rustfs
rustfs --helpAccessing RustFS
- Access the Console: Open your web browser and navigate to
http://localhost:9001to access the RustFS console.
- Default credentials: `rustfsadmin` / `rustfsadmin`- Create a Bucket: Use the console to create a new bucket for your objects.
- Upload Objects: You can upload files directly through the console or use S3-compatible APIs/clients to interact with your RustFS instance.
NOTE: To access the RustFS instance via
https, please refer to the TLS Configuration Docs.OIDC Roles Claim (Microsoft Entra ID)
RustFS supports mapping an OIDC claim containing role values into the existing authorization pipeline. Theroles_claim setting is optional: when unset or
empty, only the groups claim contributes to authorization (same as older
RustFS releases). For Microsoft Entra ID app roles, set roles_claim=roles so
both console admin checks and bucket IAM policies can evaluate those roles.Example environment configuration (opt-in roles claim):
RUSTFS_IDENTITY_OPENID_ENABLE=on
RUSTFS_IDENTITY_OPENID_CONFIG_URL="https://login.microsoftonline.com/<tenant-id>/v2.0/.well-known/openid-configuration"
RUSTFS_IDENTITY_OPENID_CLIENT_ID="<client-id>"
RUSTFS_IDENTITY_OPENID_CLIENT_SECRET="<client-secret>"
RUSTFS_IDENTITY_OPENID_SCOPES="openid,profile,email"
RUSTFS_IDENTITY_OPENID_GROUPS_CLAIM="groups"
RUSTFS_IDENTITY_OPENID_ROLES_CLAIM="roles"
Policy condition example (evaluate app roles directly with
jwt:roles; when
roles_claim is configured, RustFS also merges those values into jwt:groups
for backward compatibility with older policies):{
"Version": "2012-10-17",
"Statement": [
{
"Effect": "Allow",
"Action": ["admin:*"],
"Resource": ["arn:aws:s3:::*"],
"Condition": {
"ForAnyValue:StringEquals": {
"jwt:roles": ["RustFS.ConsoleAdmin"]
}
}
}
]
}Documentation
For detailed documentation, including configuration options, API references, and advanced usage, please visit our Documentation.Getting Help
If you have any questions or need assistance:- Check the FAQ for common issues and solutions.
- Join our GitHub Discussions to ask questions and share your experiences.
- Open an issue on our GitHub Issues page for bug reports or feature requests.
Links
- Documentation - The manual you should read
- Changelog - What we broke and fixed
- GitHub Discussions - Where the community lives
- Discord - Chat with the RustFS community
Contact
- Bugs: GitHub Issues
- Business: [email protected]
- Jobs: [email protected]
- General Discussion: GitHub Discussions
- Contributing: CONTRIBUTING.md
Contributors
RustFS is a community-driven project, and we appreciate all contributions. Check out the Contributors page to see the amazing people who have helped make RustFS better.
Star History
License
Apache 2.0RustFS is a trademark of RustFS, Inc. All other trademarks are the property of their respective owners.
Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs <container> - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Image won't pull
Test the pull directly on the host: docker pull rustfs/rustfs:latest
- "manifest unknown" means the tag no longer exists. This template uses
latest, so try pinning a specific version instead. - "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- This image supports:
amd64, arm64 - Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect <container> --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Required settings are blank
RUSTFS_OBS_LOG_DIRECTORY has no default value, and rustfs may crash or misbehave if left empty.
- Fill it in on the deploy screen before hitting deploy.
Stack won't deploy
Compose stacks fail fast on small mistakes, and Portainer shows the reason just above the editor.
- YAML only accepts spaces for indentation, a single tab breaks the whole file.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue on rustfs/rustfs
- Template not working: Open an issue on NotAFlightRisk/portainer-templates-extras
- This website not working: Open an issue on lissy93/portainer-templates
A Compose stack
RustFS is a Compose stack, a set of containers defined in one file and brought up together by Portainer, then started and stopped as a single app.
The app image
An image is the app packed up ready to go, everything RustFS needs bundled into one download. This template pulls rustfs/rustfs:latest, which Docker fetches once (about 157 MB) and then starts your own copy from.
Where the image comes from
Docker pulls its images from registries, public libraries of ready-built apps. RustFS's comes from Docker Hub, published by rustfs.
Version tags
The bit after the colon in the image name is the version tag. Here it's latest, which always points at the newest build, so a redeploy can bump you to a newer release without you asking. Newest right now is 1.0.3-glibc. Pin a specific tag if you would rather stay on one version.
Which machines it runs on
Every image is built for particular CPU types. This one ships for amd64, arm64, so it runs on both regular x86 servers and ARM boards like a Raspberry Pi.
Volumes
A volume is where RustFS keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/datakept in therustfs-datavolume Docker manages
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. RustFS takes 6 of them, and 2 need a value before it'll start properly:
RUSTFS_ACCESS_KEY, defaults toadminRUSTFS_SECRET_KEY, needs a value. Generate one with: openssl rand -hex 16. To change it later, change it here and redeploy.RUSTFS_OBS_LOG_DIRECTORY, needs a valueRUSTFS_ADMIN_USER, defaults toadmin. Admin user (access key)RUSTFS_API_PORT, defaults to9010. Host port for the S3 APIRUSTFS_CONSOLE_PORT, defaults to9011. Host port for the web console
Restart policy
The restart policy here is unless-stopped, so Docker restarts RustFS after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Networking
Nothing custom is set, so RustFS sits on Docker's default bridge network: its own private space that reaches the outside world only through the ports it publishes.
Container name
Once it's deployed, Portainer names the container rustfs. That's what you'll spot in the containers list and use in commands like docker logs rustfs.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Open source license
RustFS is open source, released under the Apache-2.0 license. In plain terms the code is out in the open, so you're free to run it and change it to fit what you need.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set RustFS up. Add the template list to Portainer once, then deploying RustFS is a click rather than a wall of config.