
![Supabase]() Supabase
Stack
The full Supabase stack, Postgres (supabase image with extensions), Auth (GoTrue), REST (PostgREST), Realtime, Storage, postgres-meta, Studio, behind the Kong gateway, adapted from the official self-hosting compose.
Configuration
TypeComposelinuxADDITIONAL_REDIRECT_URLS=''ANON_KEY=''ANON_KEY_ASYMMETRIC=''API_EXTERNAL_URL=''DASHBOARD_PASSWORD=''DASHBOARD_USERNAME=''DISABLE_SIGNUP=falseENABLE_ANONYMOUS_USERS=falseENABLE_EMAIL_AUTOCONFIRM=trueENABLE_EMAIL_SIGNUP=trueENABLE_PHONE_AUTOCONFIRM=falseENABLE_PHONE_SIGNUP=falseFUNCTIONS_VERIFY_JWT=falseGLOBAL_S3_BUCKET=''IMGPROXY_AUTO_WEBP=trueJWT_EXPIRY=3600JWT_SECRET=''MAILER_URLPATHS_CONFIRMATION=/auth/v1/verifyMAILER_URLPATHS_EMAIL_CHANGE=/auth/v1/verifyMAILER_URLPATHS_INVITE=/auth/v1/verifyMAILER_URLPATHS_RECOVERY=/auth/v1/verifyOPENAI_API_KEY=''PGRST_DB_EXTRA_SEARCH_PATH=publicPGRST_DB_MAX_ROWS=1000PGRST_DB_SCHEMAS=public,storage,graphql_publicPG_META_CRYPTO_KEY=''POOLER_DB_POOL_SIZE=5POOLER_DEFAULT_POOL_SIZE=20POOLER_MAX_CLIENT_CONN=100POOLER_PROXY_PORT_TRANSACTION=6543POOLER_TENANT_ID=supabasePOSTGRES_DB=postgresPOSTGRES_HOST=supabase-dbPOSTGRES_PASSWORD=''POSTGRES_PORT=5432REGION=localS3_PROTOCOL_ACCESS_KEY_ID=''S3_PROTOCOL_ACCESS_KEY_SECRET=''SECRET_KEY_BASE=''SERVICE_ROLE_KEY=''SERVICE_ROLE_KEY_ASYMMETRIC=''SITE_URL=''[email protected]SMTP_HOST=''SMTP_PASS=''SMTP_PORT=587SMTP_SENDER_NAME=SupabaseSMTP_USER=''STORAGE_TENANT_ID=supabaseSTUDIO_DEFAULT_ORGANIZATION=Default OrganizationSTUDIO_DEFAULT_PROJECT=Default ProjectSUPABASE_PUBLIC_URL=''SUPABASE_PUBLISHABLE_KEY=''SUPABASE_SECRET_KEY=''VAULT_ENC_KEY=''Template by deployable-sh·Source
Report issueServices
studio
Configuration
Imagesupabase/studio:2026.06.03-sha-0bca6013000/app/edge-functions : ./functions/app/snippets : ./snippetsHOSTNAME=0.0.0.0STUDIO_PG_META_URL=http://supabase-meta:8080POSTGRES_PORT=${POSTGRES_PORT:-5432}POSTGRES_HOST=${POSTGRES_HOST:-supabase-db}POSTGRES_DB=${POSTGRES_DB:-postgres}POSTGRES_PASSWORD=${POSTGRES_PASSWORD}PG_META_CRYPTO_KEY=${PG_META_CRYPTO_KEY}PGRST_DB_SCHEMAS=${PGRST_DB_SCHEMAS:-public,storage,graphql_public}PGRST_DB_MAX_ROWS=${PGRST_DB_MAX_ROWS:-1000}PGRST_DB_EXTRA_SEARCH_PATH=${PGRST_DB_EXTRA_SEARCH_PATH:-public}DEFAULT_ORGANIZATION_NAME=${STUDIO_DEFAULT_ORGANIZATION:-Default Organization}DEFAULT_PROJECT_NAME=${STUDIO_DEFAULT_PROJECT:-Default Project}OPENAI_API_KEY=${OPENAI_API_KEY:-}SUPABASE_URL=http://supabase-kong:5000SUPABASE_PUBLIC_URL=${SUPABASE_PUBLIC_URL}SUPABASE_ANON_KEY=${ANON_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoiYW5vbiIsImlzcyI6InN1cGFiYXNlIiwiaWF0IjoxNzAwMDAwMDAwLCJleHAiOjIwMDAwMDAwMDB9.6ldkvHM8WjwyHI_tKbJOgWu-VbulTx9jmeuEvNGSFkY}SUPABASE_SERVICE_KEY=${SERVICE_ROLE_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoic2VydmljZV9yb2xlIiwiaXNzIjoic3VwYWJhc2UiLCJpYXQiOjE3MDAwMDAwMDAsImV4cCI6MjAwMDAwMDAwMH0.mjENke8J4x_734atFXjInx76tWeHpG_5y1KaXY_3Smg}AUTH_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}SUPABASE_PUBLISHABLE_KEY=${SUPABASE_PUBLISHABLE_KEY:-}SUPABASE_SECRET_KEY=${SUPABASE_SECRET_KEY:-}ENABLED_FEATURES_LOGS_ALL=falseSNIPPETS_MANAGEMENT_FOLDER=/app/snippetsEDGE_FUNCTIONS_MANAGEMENT_FOLDER=/app/edge-functionsunless-stoppedImage details
kong
Configuration
Ports5000:5000KONG_DATABASE=offKONG_DECLARATIVE_CONFIG=/usr/local/kong/kong.ymlKONG_DNS_ORDER=LAST,A,CNAMEKONG_DNS_NOT_FOUND_TTL=1KONG_PLUGINS=request-transformer,cors,key-auth,acl,basic-auth,request-termination,ip-restriction,post-functionKONG_NGINX_PROXY_PROXY_BUFFER_SIZE=160kKONG_NGINX_PROXY_PROXY_BUFFERS=64 160kKONG_NGINX_WORKER_PROCESSES=2KONG_PROXY_ACCESS_LOG=/dev/stdout combinedSUPABASE_ANON_KEY=${ANON_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoiYW5vbiIsImlzcyI6InN1cGFiYXNlIiwiaWF0IjoxNzAwMDAwMDAwLCJleHAiOjIwMDAwMDAwMDB9.6ldkvHM8WjwyHI_tKbJOgWu-VbulTx9jmeuEvNGSFkY}SUPABASE_SERVICE_KEY=${SERVICE_ROLE_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoic2VydmljZV9yb2xlIiwiaXNzIjoic3VwYWJhc2UiLCJpYXQiOjE3MDAwMDAwMDAsImV4cCI6MjAwMDAwMDAwMH0.mjENke8J4x_734atFXjInx76tWeHpG_5y1KaXY_3Smg}SUPABASE_PUBLISHABLE_KEY=${SUPABASE_PUBLISHABLE_KEY:-}SUPABASE_SECRET_KEY=${SUPABASE_SECRET_KEY:-}ANON_KEY_ASYMMETRIC=${ANON_KEY_ASYMMETRIC:-}SERVICE_ROLE_KEY_ASYMMETRIC=${SERVICE_ROLE_KEY_ASYMMETRIC:-}DASHBOARD_USERNAME=${DASHBOARD_USERNAME}DASHBOARD_PASSWORD=${DASHBOARD_PASSWORD}KONG_PROXY_LISTEN=0.0.0.0:5000unless-stopped./kongauth
Configuration
Imagesupabase/gotrue:v2.189.09999GOTRUE_API_HOST=0.0.0.0GOTRUE_API_PORT=9999API_EXTERNAL_URL=${API_EXTERNAL_URL}GOTRUE_DB_DRIVER=postgresGOTRUE_DB_DATABASE_URL=postgres://supabase_auth_admin:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}GOTRUE_SITE_URL=${SITE_URL}GOTRUE_URI_ALLOW_LIST=${ADDITIONAL_REDIRECT_URLS:-}GOTRUE_DISABLE_SIGNUP=${DISABLE_SIGNUP:-false}GOTRUE_JWT_ADMIN_ROLES=service_roleGOTRUE_JWT_AUD=authenticatedGOTRUE_JWT_DEFAULT_GROUP_NAME=authenticatedGOTRUE_JWT_EXP=${JWT_EXPIRY:-3600}GOTRUE_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}GOTRUE_JWT_ISSUER=${API_EXTERNAL_URL}/auth/v1GOTRUE_EXTERNAL_EMAIL_ENABLED=${ENABLE_EMAIL_SIGNUP:-true}GOTRUE_EXTERNAL_ANONYMOUS_USERS_ENABLED=${ENABLE_ANONYMOUS_USERS:-false}GOTRUE_MAILER_AUTOCONFIRM=${ENABLE_EMAIL_AUTOCONFIRM:-true}GOTRUE_SMTP_ADMIN_EMAIL=${SMTP_ADMIN_EMAIL:[email protected]}GOTRUE_SMTP_HOST=${SMTP_HOST:-}GOTRUE_SMTP_PORT=${SMTP_PORT:-587}GOTRUE_SMTP_USER=${SMTP_USER:-}GOTRUE_SMTP_PASS=${SMTP_PASS:-}GOTRUE_SMTP_SENDER_NAME=${SMTP_SENDER_NAME:-Supabase}GOTRUE_MAILER_URLPATHS_INVITE=${MAILER_URLPATHS_INVITE:-/auth/v1/verify}GOTRUE_MAILER_URLPATHS_CONFIRMATION=${MAILER_URLPATHS_CONFIRMATION:-/auth/v1/verify}GOTRUE_MAILER_URLPATHS_RECOVERY=${MAILER_URLPATHS_RECOVERY:-/auth/v1/verify}GOTRUE_MAILER_URLPATHS_EMAIL_CHANGE=${MAILER_URLPATHS_EMAIL_CHANGE:-/auth/v1/verify}GOTRUE_EXTERNAL_PHONE_ENABLED=${ENABLE_PHONE_SIGNUP:-false}GOTRUE_SMS_AUTOCONFIRM=${ENABLE_PHONE_AUTOCONFIRM:-false}unless-stoppedImage details
rest
Configuration
Imagepostgrest/postgrest:v14.12postgrest3000PGRST_DB_URI=postgres://authenticator:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}PGRST_DB_SCHEMAS=${PGRST_DB_SCHEMAS:-public,storage,graphql_public}PGRST_DB_MAX_ROWS=${PGRST_DB_MAX_ROWS:-1000}PGRST_DB_EXTRA_SEARCH_PATH=${PGRST_DB_EXTRA_SEARCH_PATH:-public}PGRST_DB_ANON_ROLE=anonPGRST_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}PGRST_DB_USE_LEGACY_GUCS=falsePGRST_APP_SETTINGS_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}PGRST_APP_SETTINGS_JWT_EXP=${JWT_EXPIRY:-3600}unless-stoppedImage details
realtime
Configuration
Imagesupabase/realtime:v2.102.34000PORT=4000DB_HOST=${POSTGRES_HOST:-supabase-db}DB_PORT=${POSTGRES_PORT:-5432}DB_USER=supabase_adminDB_PASSWORD=${POSTGRES_PASSWORD}DB_NAME=${POSTGRES_DB:-postgres}DB_AFTER_CONNECT_QUERY=SET search_path TO _realtimeDB_ENC_KEY=supabaserealtimeAPI_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}SECRET_KEY_BASE=${SECRET_KEY_BASE}METRICS_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}ERL_AFLAGS=-proto_dist inet_tcpDNS_NODES=''RLIMIT_NOFILE=10000APP_NAME=realtimeSEED_SELF_HOST=trueRUN_JANITOR=trueDISABLE_HEALTHCHECK_LOGGING=trueunless-stoppedImage details
storage
Configuration
Imagesupabase/storage-api:v1.60.45000/var/lib/storage : ./storageANON_KEY=${ANON_KEY:-}SERVICE_KEY=${SERVICE_ROLE_KEY:-}POSTGREST_URL=http://supabase-rest:3000AUTH_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}DATABASE_URL=postgres://supabase_storage_admin:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}STORAGE_PUBLIC_URL=${SUPABASE_PUBLIC_URL}REQUEST_ALLOW_X_FORWARDED_PATH=trueFILE_SIZE_LIMIT=52428800STORAGE_BACKEND=fileGLOBAL_S3_BUCKET=${GLOBAL_S3_BUCKET}FILE_STORAGE_BACKEND_PATH=/var/lib/storageTENANT_ID=${STORAGE_TENANT_ID:-supabase}REGION=${REGION:-local}ENABLE_IMAGE_TRANSFORMATION=trueIMGPROXY_URL=http://supabase-imgproxy:5001S3_PROTOCOL_ACCESS_KEY_ID=${S3_PROTOCOL_ACCESS_KEY_ID}S3_PROTOCOL_ACCESS_KEY_SECRET=${S3_PROTOCOL_ACCESS_KEY_SECRET}unless-stoppedImage details
imgproxy
Configuration
Imagedarthsim/imgproxy:v3.30.15001/var/lib/storage : ./storageIMGPROXY_BIND=:5001IMGPROXY_LOCAL_FILESYSTEM_ROOT=/IMGPROXY_USE_ETAG=trueIMGPROXY_AUTO_WEBP=${IMGPROXY_AUTO_WEBP:-true}IMGPROXY_MAX_SRC_RESOLUTION=16.8unless-stoppedImage details
meta
Configuration
Imagesupabase/postgres-meta:v0.96.68080PG_META_PORT=8080PG_META_DB_HOST=${POSTGRES_HOST:-supabase-db}PG_META_DB_PORT=${POSTGRES_PORT:-5432}PG_META_DB_NAME=${POSTGRES_DB:-postgres}PG_META_DB_USER=supabase_adminPG_META_DB_PASSWORD=${POSTGRES_PASSWORD}CRYPTO_KEY=${PG_META_CRYPTO_KEY}unless-stoppedImage details
functions
Configuration
Imagesupabase/edge-runtime:v1.74.0start,--main-service,/home/deno/functions/main9000/root/.cache/deno : deno-cache/home/deno/functions : ./functionsJWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}SUPABASE_URL=http://supabase-kong:5000SUPABASE_PUBLIC_URL=${SUPABASE_PUBLIC_URL}SUPABASE_ANON_KEY=${ANON_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoiYW5vbiIsImlzcyI6InN1cGFiYXNlIiwiaWF0IjoxNzAwMDAwMDAwLCJleHAiOjIwMDAwMDAwMDB9.6ldkvHM8WjwyHI_tKbJOgWu-VbulTx9jmeuEvNGSFkY}SUPABASE_SERVICE_ROLE_KEY=${SERVICE_ROLE_KEY:-}SUPABASE_PUBLISHABLE_KEYS={"default":"${SUPABASE_PUBLISHABLE_KEY:-}"}SUPABASE_SECRET_KEYS={"default":"${SUPABASE_SECRET_KEY:-}"}SUPABASE_DB_URL=postgresql://postgres:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}VERIFY_JWT=${FUNCTIONS_VERIFY_JWT:-false}unless-stoppedImage details
db
Configuration
Commandpostgres,-c,config_file=/etc/postgresql/postgresql.conf,-c,data_directory=/var/lib/postgresql/data/pgdata,-c,log_min_messages=fatal5432/var/lib/postgresql/data : dbdataPOSTGRES_HOST=/var/run/postgresqlPGPORT=${POSTGRES_PORT:-5432}POSTGRES_PORT=${POSTGRES_PORT:-5432}PGPASSWORD=${POSTGRES_PASSWORD}POSTGRES_PASSWORD=${POSTGRES_PASSWORD}PGDATABASE=${POSTGRES_DB:-postgres}POSTGRES_DB=${POSTGRES_DB:-postgres}JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}JWT_EXP=${JWT_EXPIRY:-3600}unless-stopped./dbsupavisor
Configuration
Imagesupabase/supavisor:2.9.5/bin/sh,-c,/app/bin/migrate && /app/bin/supavisor eval "$$(cat /etc/pooler/pooler.exs)" && /app/bin/server${POSTGRES_PORT:-5432}:5432${POOLER_PROXY_PORT_TRANSACTION:-6543}:6543PORT=4000POSTGRES_PORT=${POSTGRES_PORT:-5432}POSTGRES_HOST=${POSTGRES_HOST:-supabase-db}POSTGRES_DB=${POSTGRES_DB:-postgres}POSTGRES_PASSWORD=${POSTGRES_PASSWORD}DATABASE_URL=ecto://supabase_admin:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/_supabaseCLUSTER_POSTGRES=trueSECRET_KEY_BASE=${SECRET_KEY_BASE}VAULT_ENC_KEY=${VAULT_ENC_KEY}API_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}METRICS_JWT_SECRET=${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}REGION=localERL_AFLAGS=-proto_dist inet_tcpPOOLER_TENANT_ID=${POOLER_TENANT_ID:-supabase}POOLER_DEFAULT_POOL_SIZE=${POOLER_DEFAULT_POOL_SIZE:-20}POOLER_MAX_CLIENT_CONN=${POOLER_MAX_CLIENT_CONN:-100}POOLER_POOL_MODE=transactionDB_POOL_SIZE=${POOLER_DB_POOL_SIZE:-5}unless-stoppedImage details
Standalone Install
Select an install method, to see config/commands for deploying Supabase
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
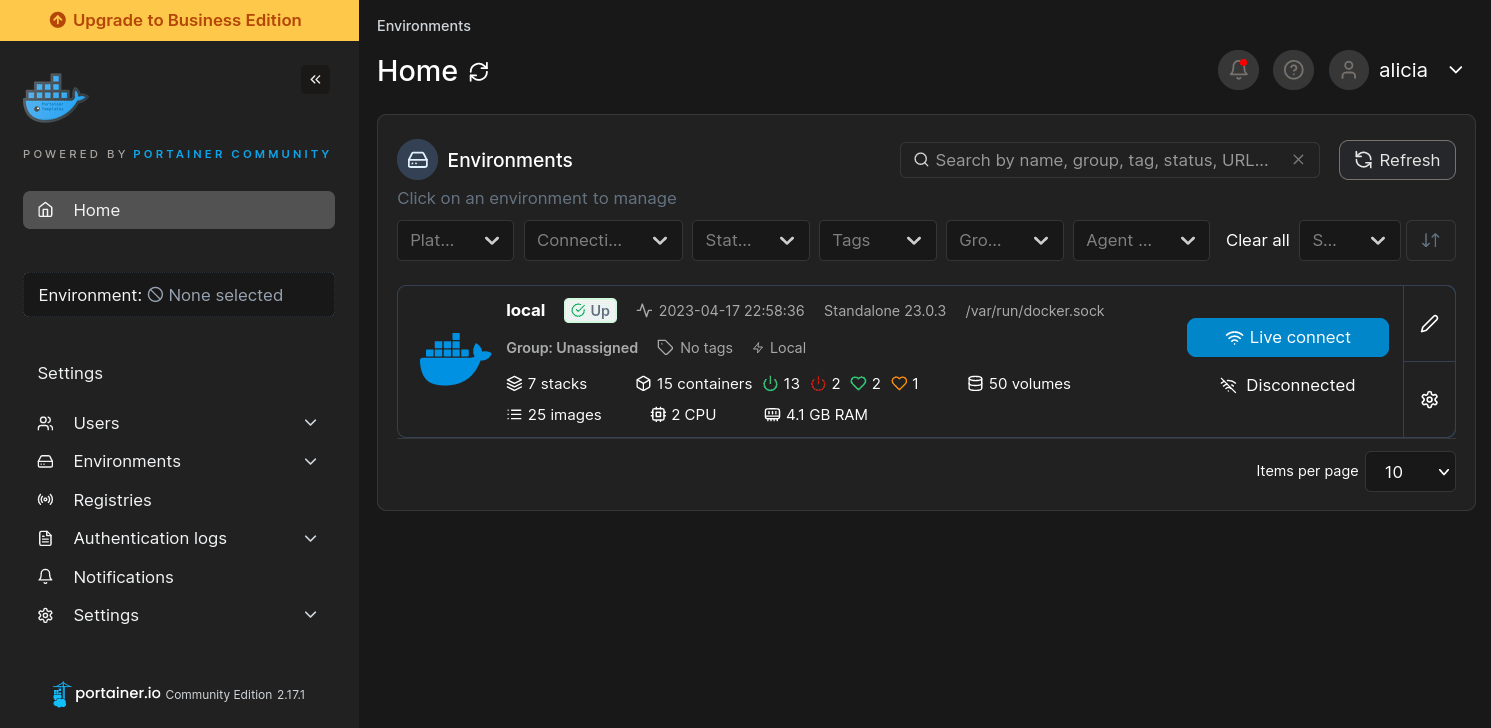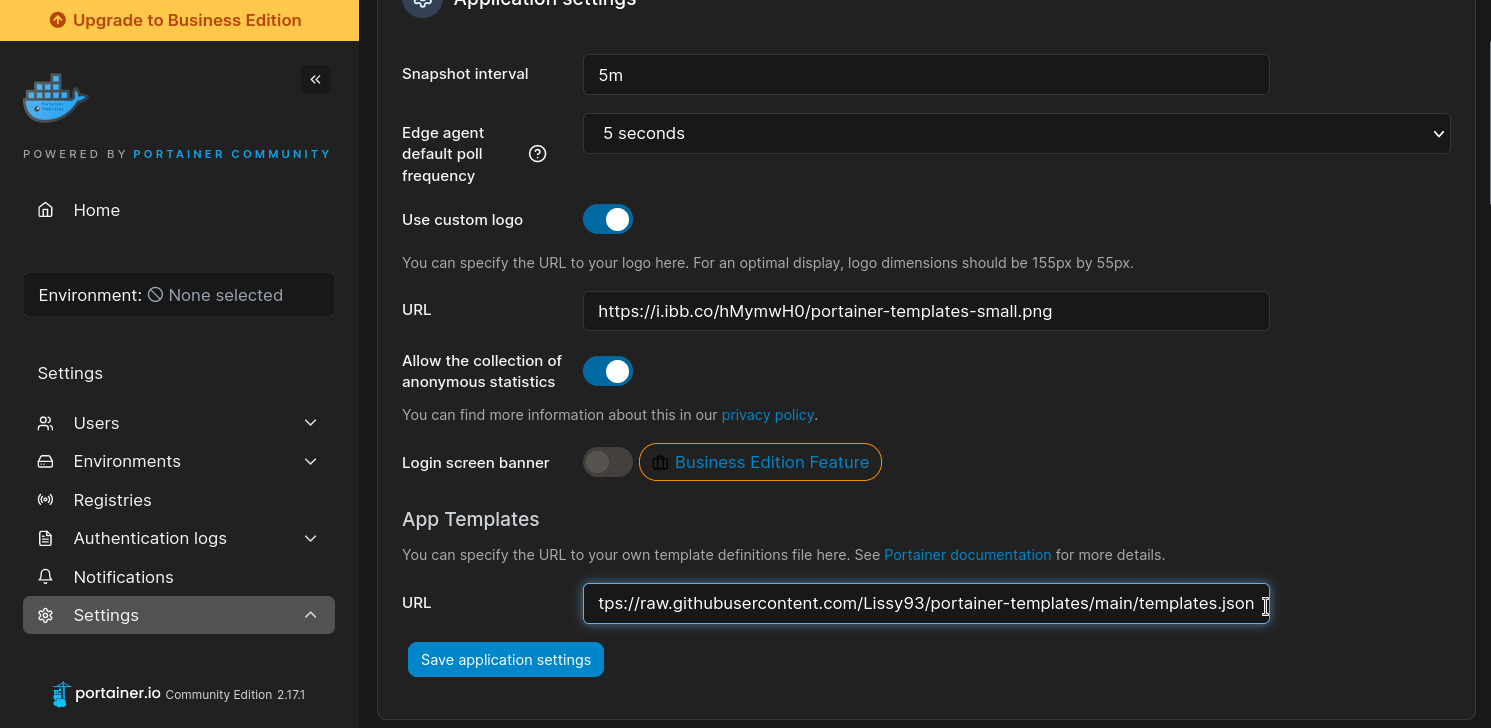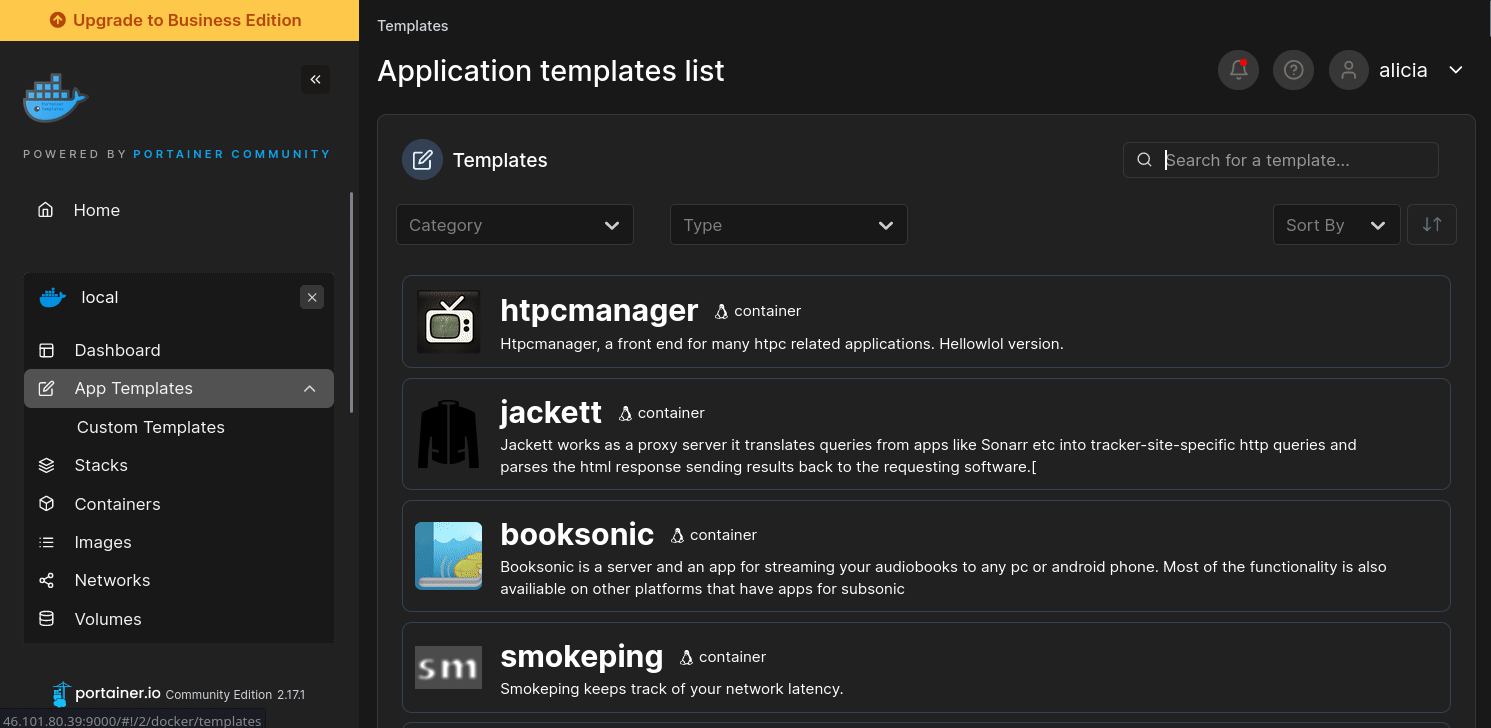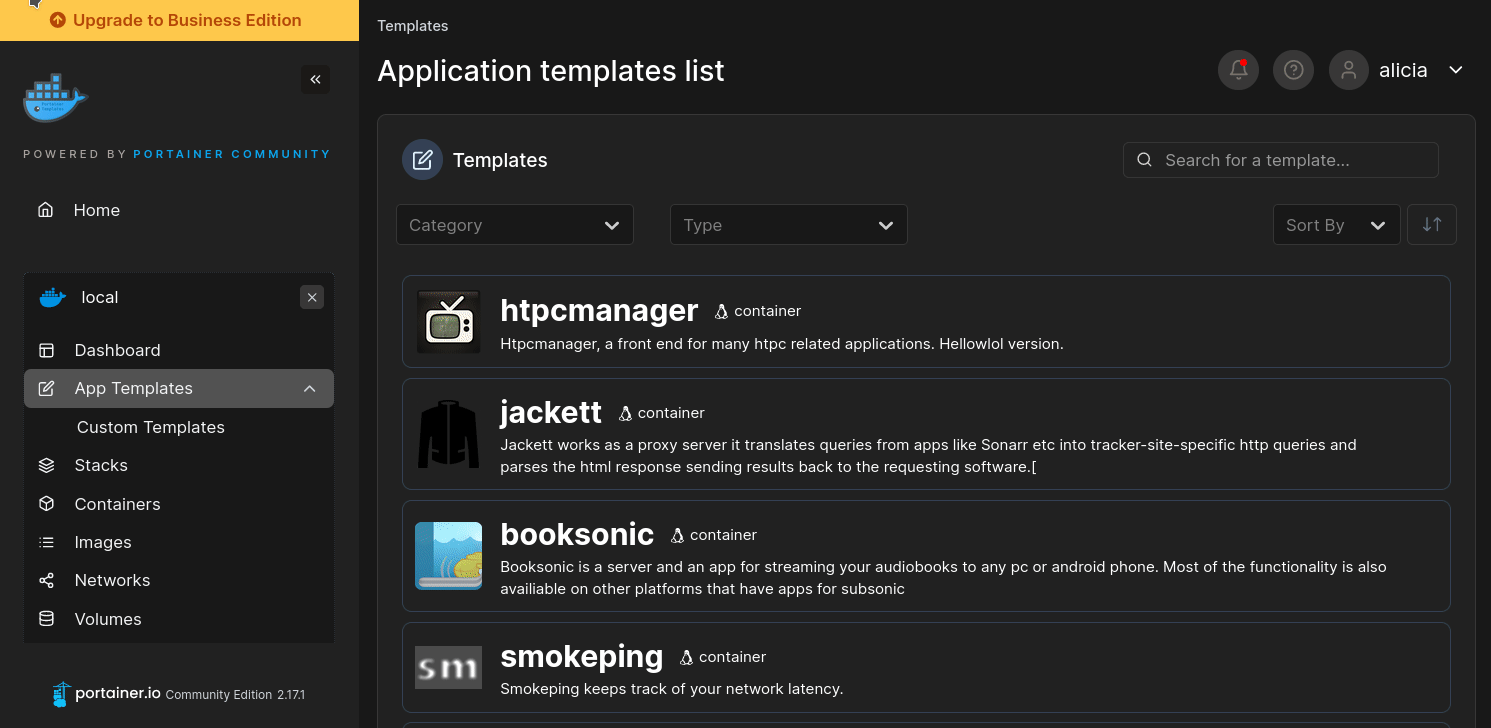
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select Supabase, fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
Original stackfile
The compose file this template deploys, straight from its repo:
name: supabase
services:
  studio:
    ports:
    - "3000"
    image: supabase/studio:2026.06.03-sha-0bca601
    restart: unless-stopped
    volumes:
    - ./functions:/app/edge-functions:ro,z
    - ./snippets:/app/snippets:z
    healthcheck:
      test:
      - CMD-SHELL
      - node -e "fetch('http://localhost:3000/api/platform/profile').then((r) => {if (r.status !== 200) throw new Error(r.status)})"
      timeout: 10s
      interval: 5s
      retries: 3
      start_period: 20s
    environment:
      HOSTNAME: 0.0.0.0
      STUDIO_PG_META_URL: http://supabase-meta:8080
      POSTGRES_PORT: ${POSTGRES_PORT:-5432}
      POSTGRES_HOST: ${POSTGRES_HOST:-supabase-db}
      POSTGRES_DB: ${POSTGRES_DB:-postgres}
      POSTGRES_PASSWORD: ${POSTGRES_PASSWORD}
      PG_META_CRYPTO_KEY: ${PG_META_CRYPTO_KEY}
      PGRST_DB_SCHEMAS: ${PGRST_DB_SCHEMAS:-public,storage,graphql_public}
      PGRST_DB_MAX_ROWS: ${PGRST_DB_MAX_ROWS:-1000}
      PGRST_DB_EXTRA_SEARCH_PATH: ${PGRST_DB_EXTRA_SEARCH_PATH:-public}
      DEFAULT_ORGANIZATION_NAME: ${STUDIO_DEFAULT_ORGANIZATION:-Default Organization}
      DEFAULT_PROJECT_NAME: ${STUDIO_DEFAULT_PROJECT:-Default Project}
      OPENAI_API_KEY: ${OPENAI_API_KEY:-}
      SUPABASE_URL: http://supabase-kong:5000
      SUPABASE_PUBLIC_URL: ${SUPABASE_PUBLIC_URL}
      SUPABASE_ANON_KEY: ${ANON_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoiYW5vbiIsImlzcyI6InN1cGFiYXNlIiwiaWF0IjoxNzAwMDAwMDAwLCJleHAiOjIwMDAwMDAwMDB9.6ldkvHM8WjwyHI_tKbJOgWu-VbulTx9jmeuEvNGSFkY}
      SUPABASE_SERVICE_KEY: ${SERVICE_ROLE_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoic2VydmljZV9yb2xlIiwiaXNzIjoic3VwYWJhc2UiLCJpYXQiOjE3MDAwMDAwMDAsImV4cCI6MjAwMDAwMDAwMH0.mjENke8J4x_734atFXjInx76tWeHpG_5y1KaXY_3Smg}
      AUTH_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      SUPABASE_PUBLISHABLE_KEY: ${SUPABASE_PUBLISHABLE_KEY:-}
      SUPABASE_SECRET_KEY: ${SUPABASE_SECRET_KEY:-}
      ENABLED_FEATURES_LOGS_ALL: 'false'
      SNIPPETS_MANAGEMENT_FOLDER: /app/snippets
      EDGE_FUNCTIONS_MANAGEMENT_FOLDER: /app/edge-functions
  kong:
    restart: unless-stopped
    healthcheck:
      test:
      - CMD
      - kong
      - health
      interval: 5s
      timeout: 5s
      retries: 5
    depends_on:
      studio:
        condition: service_healthy
    environment:
      KONG_DATABASE: 'off'
      KONG_DECLARATIVE_CONFIG: /usr/local/kong/kong.yml
      KONG_DNS_ORDER: LAST,A,CNAME
      KONG_DNS_NOT_FOUND_TTL: 1
      KONG_PLUGINS: request-transformer,cors,key-auth,acl,basic-auth,request-termination,ip-restriction,post-function
      KONG_NGINX_PROXY_PROXY_BUFFER_SIZE: 160k
      KONG_NGINX_PROXY_PROXY_BUFFERS: 64 160k
      # worker_processes defaults to auto (one per core): ~100 MiB per
      # worker on a many-core node, blowing straight past the 512 MiB
      # allocation. Two workers are plenty for a gateway this size.
      KONG_NGINX_WORKER_PROCESSES: "2"
      KONG_PROXY_ACCESS_LOG: /dev/stdout combined
      SUPABASE_ANON_KEY: ${ANON_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoiYW5vbiIsImlzcyI6InN1cGFiYXNlIiwiaWF0IjoxNzAwMDAwMDAwLCJleHAiOjIwMDAwMDAwMDB9.6ldkvHM8WjwyHI_tKbJOgWu-VbulTx9jmeuEvNGSFkY}
      SUPABASE_SERVICE_KEY: ${SERVICE_ROLE_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoic2VydmljZV9yb2xlIiwiaXNzIjoic3VwYWJhc2UiLCJpYXQiOjE3MDAwMDAwMDAsImV4cCI6MjAwMDAwMDAwMH0.mjENke8J4x_734atFXjInx76tWeHpG_5y1KaXY_3Smg}
      SUPABASE_PUBLISHABLE_KEY: ${SUPABASE_PUBLISHABLE_KEY:-}
      SUPABASE_SECRET_KEY: ${SUPABASE_SECRET_KEY:-}
      ANON_KEY_ASYMMETRIC: ${ANON_KEY_ASYMMETRIC:-}
      SERVICE_ROLE_KEY_ASYMMETRIC: ${SERVICE_ROLE_KEY_ASYMMETRIC:-}
      DASHBOARD_USERNAME: ${DASHBOARD_USERNAME}
      DASHBOARD_PASSWORD: ${DASHBOARD_PASSWORD}
      KONG_PROXY_LISTEN: 0.0.0.0:5000
    build: ./kong
    ports:
    - 5000:5000
  auth:
    ports:
    - "9999"
    image: supabase/gotrue:v2.189.0
    restart: unless-stopped
    healthcheck:
      test:
      - CMD
      - wget
      - --no-verbose
      - --tries=1
      - --spider
      - http://localhost:9999/health
      timeout: 5s
      interval: 5s
      retries: 3
    depends_on:
      db:
        condition: service_healthy
    environment:
      GOTRUE_API_HOST: 0.0.0.0
      GOTRUE_API_PORT: 9999
      API_EXTERNAL_URL: ${API_EXTERNAL_URL}
      GOTRUE_DB_DRIVER: postgres
      GOTRUE_DB_DATABASE_URL: postgres://supabase_auth_admin:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}
      GOTRUE_SITE_URL: ${SITE_URL}
      GOTRUE_URI_ALLOW_LIST: ${ADDITIONAL_REDIRECT_URLS:-}
      GOTRUE_DISABLE_SIGNUP: ${DISABLE_SIGNUP:-false}
      GOTRUE_JWT_ADMIN_ROLES: service_role
      GOTRUE_JWT_AUD: authenticated
      GOTRUE_JWT_DEFAULT_GROUP_NAME: authenticated
      GOTRUE_JWT_EXP: ${JWT_EXPIRY:-3600}
      GOTRUE_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      GOTRUE_JWT_ISSUER: ${API_EXTERNAL_URL}/auth/v1
      GOTRUE_EXTERNAL_EMAIL_ENABLED: ${ENABLE_EMAIL_SIGNUP:-true}
      GOTRUE_EXTERNAL_ANONYMOUS_USERS_ENABLED: ${ENABLE_ANONYMOUS_USERS:-false}
      GOTRUE_MAILER_AUTOCONFIRM: ${ENABLE_EMAIL_AUTOCONFIRM:-true}
      GOTRUE_SMTP_ADMIN_EMAIL: ${SMTP_ADMIN_EMAIL:[email protected]}
      GOTRUE_SMTP_HOST: ${SMTP_HOST:-}
      GOTRUE_SMTP_PORT: ${SMTP_PORT:-587}
      GOTRUE_SMTP_USER: ${SMTP_USER:-}
      GOTRUE_SMTP_PASS: ${SMTP_PASS:-}
      GOTRUE_SMTP_SENDER_NAME: ${SMTP_SENDER_NAME:-Supabase}
      GOTRUE_MAILER_URLPATHS_INVITE: ${MAILER_URLPATHS_INVITE:-/auth/v1/verify}
      GOTRUE_MAILER_URLPATHS_CONFIRMATION: ${MAILER_URLPATHS_CONFIRMATION:-/auth/v1/verify}
      GOTRUE_MAILER_URLPATHS_RECOVERY: ${MAILER_URLPATHS_RECOVERY:-/auth/v1/verify}
      GOTRUE_MAILER_URLPATHS_EMAIL_CHANGE: ${MAILER_URLPATHS_EMAIL_CHANGE:-/auth/v1/verify}
      GOTRUE_EXTERNAL_PHONE_ENABLED: ${ENABLE_PHONE_SIGNUP:-false}
      GOTRUE_SMS_AUTOCONFIRM: ${ENABLE_PHONE_AUTOCONFIRM:-false}
  rest:
    ports:
    - "3000"
    image: postgrest/postgrest:v14.12
    restart: unless-stopped
    depends_on:
      db:
        condition: service_healthy
    environment:
      PGRST_DB_URI: postgres://authenticator:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}
      PGRST_DB_SCHEMAS: ${PGRST_DB_SCHEMAS:-public,storage,graphql_public}
      PGRST_DB_MAX_ROWS: ${PGRST_DB_MAX_ROWS:-1000}
      PGRST_DB_EXTRA_SEARCH_PATH: ${PGRST_DB_EXTRA_SEARCH_PATH:-public}
      PGRST_DB_ANON_ROLE: anon
      PGRST_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      PGRST_DB_USE_LEGACY_GUCS: 'false'
      PGRST_APP_SETTINGS_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      PGRST_APP_SETTINGS_JWT_EXP: ${JWT_EXPIRY:-3600}
    command:
    - postgrest
  realtime:
    ports:
    - "4000"
    image: supabase/realtime:v2.102.3
    restart: unless-stopped
    depends_on:
      db:
        condition: service_healthy
    healthcheck:
      test:
      - CMD-SHELL
      - 'curl -sSfL --head -o /dev/null -H "Authorization: Bearer ${ANON_KEY:-}" http://localhost:4000/api/tenants/realtime-dev/health'
      timeout: 5s
      interval: 30s
      retries: 3
      start_period: 10s
    environment:
      PORT: 4000
      DB_HOST: ${POSTGRES_HOST:-supabase-db}
      DB_PORT: ${POSTGRES_PORT:-5432}
      DB_USER: supabase_admin
      DB_PASSWORD: ${POSTGRES_PASSWORD}
      DB_NAME: ${POSTGRES_DB:-postgres}
      DB_AFTER_CONNECT_QUERY: SET search_path TO _realtime
      DB_ENC_KEY: supabaserealtime
      API_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      SECRET_KEY_BASE: ${SECRET_KEY_BASE}
      METRICS_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      ERL_AFLAGS: -proto_dist inet_tcp
      DNS_NODES: ''''''
      RLIMIT_NOFILE: '10000'
      APP_NAME: realtime
      SEED_SELF_HOST: 'true'
      RUN_JANITOR: 'true'
      DISABLE_HEALTHCHECK_LOGGING: 'true'
  storage:
    ports:
    - "5000"
    image: supabase/storage-api:v1.60.4
    restart: unless-stopped
    volumes:
    - ./storage:/var/lib/storage:z
    depends_on:
      db:
        condition: service_healthy
      rest:
        condition: service_started
    healthcheck:
      test:
      - CMD
      - wget
      - --no-verbose
      - --tries=1
      - --spider
      - http://supabase-storage:5000/status
      timeout: 5s
      interval: 5s
      retries: 3
      start_period: 10s
    environment:
      ANON_KEY: ${ANON_KEY:-}
      SERVICE_KEY: ${SERVICE_ROLE_KEY:-}
      POSTGREST_URL: http://supabase-rest:3000
      AUTH_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      DATABASE_URL: postgres://supabase_storage_admin:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}
      STORAGE_PUBLIC_URL: ${SUPABASE_PUBLIC_URL}
      REQUEST_ALLOW_X_FORWARDED_PATH: 'true'
      FILE_SIZE_LIMIT: 52428800
      STORAGE_BACKEND: file
      GLOBAL_S3_BUCKET: ${GLOBAL_S3_BUCKET}
      FILE_STORAGE_BACKEND_PATH: /var/lib/storage
      TENANT_ID: ${STORAGE_TENANT_ID:-supabase}
      REGION: ${REGION:-local}
      ENABLE_IMAGE_TRANSFORMATION: 'true'
      IMGPROXY_URL: http://supabase-imgproxy:5001
      S3_PROTOCOL_ACCESS_KEY_ID: ${S3_PROTOCOL_ACCESS_KEY_ID}
      S3_PROTOCOL_ACCESS_KEY_SECRET: ${S3_PROTOCOL_ACCESS_KEY_SECRET}
  imgproxy:
    ports:
    - "5001"
    image: darthsim/imgproxy:v3.30.1
    restart: unless-stopped
    volumes:
    - ./storage:/var/lib/storage:z
    healthcheck:
      test:
      - CMD
      - imgproxy
      - health
      timeout: 5s
      interval: 5s
      retries: 3
    environment:
      IMGPROXY_BIND: :5001
      IMGPROXY_LOCAL_FILESYSTEM_ROOT: /
      IMGPROXY_USE_ETAG: 'true'
      IMGPROXY_AUTO_WEBP: ${IMGPROXY_AUTO_WEBP:-true}
      IMGPROXY_MAX_SRC_RESOLUTION: 16.8
    profiles:
    - imgproxy
  meta:
    ports:
    - "8080"
    image: supabase/postgres-meta:v0.96.6
    restart: unless-stopped
    depends_on:
      db:
        condition: service_healthy
    environment:
      PG_META_PORT: 8080
      PG_META_DB_HOST: ${POSTGRES_HOST:-supabase-db}
      PG_META_DB_PORT: ${POSTGRES_PORT:-5432}
      PG_META_DB_NAME: ${POSTGRES_DB:-postgres}
      PG_META_DB_USER: supabase_admin
      PG_META_DB_PASSWORD: ${POSTGRES_PASSWORD}
      CRYPTO_KEY: ${PG_META_CRYPTO_KEY}
  functions:
    ports:
    - "9000"
    image: supabase/edge-runtime:v1.74.0
    restart: unless-stopped
    volumes:
    - deno-cache:/root/.cache/deno
    - ./functions:/home/deno/functions:z
    depends_on:
      kong:
        condition: service_healthy
    healthcheck:
      test:
      - CMD-SHELL
      - timeout 1 bash -c '</dev/tcp/127.0.0.1/9000'
      interval: 5s
      timeout: 5s
      retries: 3
    environment:
      JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      SUPABASE_URL: http://supabase-kong:5000
      SUPABASE_PUBLIC_URL: ${SUPABASE_PUBLIC_URL}
      SUPABASE_ANON_KEY: ${ANON_KEY:-eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoiYW5vbiIsImlzcyI6InN1cGFiYXNlIiwiaWF0IjoxNzAwMDAwMDAwLCJleHAiOjIwMDAwMDAwMDB9.6ldkvHM8WjwyHI_tKbJOgWu-VbulTx9jmeuEvNGSFkY}
      SUPABASE_SERVICE_ROLE_KEY: ${SERVICE_ROLE_KEY:-}
      SUPABASE_PUBLISHABLE_KEYS: '{"default":"${SUPABASE_PUBLISHABLE_KEY:-}"}'
      SUPABASE_SECRET_KEYS: '{"default":"${SUPABASE_SECRET_KEY:-}"}'
      SUPABASE_DB_URL: postgresql://postgres:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/${POSTGRES_DB:-postgres}
      VERIFY_JWT: ${FUNCTIONS_VERIFY_JWT:-false}
    command:
    - start
    - --main-service
    - /home/deno/functions/main
    profiles:
    - functions
  db:
    ports:
    - "5432"
    restart: unless-stopped
    volumes:
    - dbdata:/var/lib/postgresql/data
    healthcheck:
      test:
      - CMD
      - pg_isready
      - -U
      - postgres
      - -h
      - localhost
      interval: 5s
      timeout: 5s
      retries: 10
    environment:
      POSTGRES_HOST: /var/run/postgresql
      PGPORT: ${POSTGRES_PORT:-5432}
      POSTGRES_PORT: ${POSTGRES_PORT:-5432}
      PGPASSWORD: ${POSTGRES_PASSWORD}
      POSTGRES_PASSWORD: ${POSTGRES_PASSWORD}
      PGDATABASE: ${POSTGRES_DB:-postgres}
      POSTGRES_DB: ${POSTGRES_DB:-postgres}
      JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      JWT_EXP: ${JWT_EXPIRY:-3600}
    command:
    - postgres
    - -c
    - config_file=/etc/postgresql/postgresql.conf
    - -c
    - data_directory=/var/lib/postgresql/data/pgdata
    - -c
    - log_min_messages=fatal
    build: ./db
  supavisor:
    image: supabase/supavisor:2.9.5
    restart: unless-stopped
    ports:
    - ${POSTGRES_PORT:-5432}:5432
    - ${POOLER_PROXY_PORT_TRANSACTION:-6543}:6543
    healthcheck:
      test:
      - CMD
      - curl
      - -sSfL
      - --head
      - -o
      - /dev/null
      - http://127.0.0.1:4000/api/health
      interval: 10s
      timeout: 5s
      retries: 10
      start_period: 30s
    depends_on:
      db:
        condition: service_healthy
    environment:
      PORT: 4000
      POSTGRES_PORT: ${POSTGRES_PORT:-5432}
      POSTGRES_HOST: ${POSTGRES_HOST:-supabase-db}
      POSTGRES_DB: ${POSTGRES_DB:-postgres}
      POSTGRES_PASSWORD: ${POSTGRES_PASSWORD}
      DATABASE_URL: ecto://supabase_admin:${POSTGRES_PASSWORD}@${POSTGRES_HOST:-supabase-db}:${POSTGRES_PORT:-5432}/_supabase
      CLUSTER_POSTGRES: 'true'
      SECRET_KEY_BASE: ${SECRET_KEY_BASE}
      VAULT_ENC_KEY: ${VAULT_ENC_KEY}
      API_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      METRICS_JWT_SECRET: ${JWT_SECRET:-super-secret-jwt-token-with-at-least-32-characters-long}
      REGION: local
      ERL_AFLAGS: -proto_dist inet_tcp
      POOLER_TENANT_ID: ${POOLER_TENANT_ID:-supabase}
      POOLER_DEFAULT_POOL_SIZE: ${POOLER_DEFAULT_POOL_SIZE:-20}
      POOLER_MAX_CLIENT_CONN: ${POOLER_MAX_CLIENT_CONN:-100}
      POOLER_POOL_MODE: transaction
      DB_POOL_SIZE: ${POOLER_DB_POOL_SIZE:-5}
    command:
    - /bin/sh
    - -c
    - /app/bin/migrate && /app/bin/supavisor eval "$$(cat /etc/pooler/pooler.exs)" && /app/bin/server
    profiles:
    - pooler
volumes:
  deno-cache: null
  dbdata: null
Or deploy it directly from the source:
git clone https://github.com/deployable-sh/stacks
cd stacks
docker compose -f supabase/compose.yaml up -d
More install options in our documentation.
Container Documentation
rest Documentation
REST API for any Postgres database
realtime Documentation
imgproxy Documentation
Fast and secure standalone server for resizing and converting remote images
Serve Supabase on your own domain behind Caddy, Nginx or Traefik. Fill in your domain and copy the result. It's a starting point, some apps need their own base URL or extra headers set too.
Proxying supabase.example.com to http://studio:3000
Add this to your Caddyfile
supabase.example.com {
	reverse_proxy http://studio:3000
}Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs <container> - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Port already in use
If deployment fails with "Bind for 0.0.0.0:5000 failed: port is already allocated", something else on your server is using that port.
- Find what's using it:
sudo ss -tlnp | grep :5000 - Stop the other service, or pick a different host port. In
5000:5000only the left number is yours to change, the right one belongs to the app.
Published on a random port
This template exposes 3000 without setting a host port,
so Docker picks a random free one on every deploy.
- Find it in the Ports column of Portainer's container list, or with
docker port <container>
Running but the page won't load
The container is up but nothing appears in your browser.
- Use your server's real IP:
http://your-server-ip:5000. The 0.0.0.0 link Portainer shows isn't a real address. - Give it a minute after first deploy, supabase can take a while to initialise.
- Make sure your firewall allows the port, e.g.
sudo ufw allow 5000
Image won't pull
Test the pull directly on the host: docker pull supabase/studio:2026.06.03-sha-0bca601
- "manifest unknown" means the tag no longer exists.
- "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect <container> --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Stack won't deploy
Compose stacks fail fast on small mistakes, and Portainer shows the reason just above the editor.
- YAML only accepts spaces for indentation, a single tab breaks the whole file.
- Relative volume paths like
./functionsoften fail in Portainer because there's no working directory. Swap them for absolute paths.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue within supabase's repo
- Template not working: Open an issue on deployable-sh/stacks
- This website not working: Open an issue on lissy93/portainer-templates
A Compose stack
Supabase is a Compose stack, a set of containers (11 of them) defined in one file and brought up together by Portainer, then started and stopped as a single app.
The services
This stack is built from 11 containers that run side by side. Here's each one, with the image it runs and anything it waits for first:
studiorunssupabase/studio:2026.06.03-sha-0bca601kong, starts after studioauthrunssupabase/gotrue:v2.189.0, starts after dbrestrunspostgrest/postgrest:v14.12, starts after dbrealtimerunssupabase/realtime:v2.102.3, starts after dbstoragerunssupabase/storage-api:v1.60.4, starts after db, restimgproxyrunsdarthsim/imgproxy:v3.30.1metarunssupabase/postgres-meta:v0.96.6, starts after dbfunctionsrunssupabase/edge-runtime:v1.74.0, starts after kongdbsupavisorrunssupabase/supavisor:2.9.5, starts after db
Ports
A port is the door the app answers on. A mapping like 5000:5000 means it's reachable on port 5000 of your server, where the left number is yours to change and the right one belongs to the app. It opens:
3000, published on a random host port5000:50009999, published on a random host port3000, published on a random host port4000, published on a random host port5000, published on a random host port5001, published on a random host port8080, published on a random host port9000, published on a random host port5432, published on a random host port
Volumes
A volume is where Supabase keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/app/edge-functionsfrom./functionson the host/app/snippetsfrom./snippetson the host/var/lib/storagefrom./storageon the host/root/.cache/denokept in thedeno-cachevolume Docker manages/home/deno/functionsfrom./functionson the host/var/lib/postgresql/datakept in thedbdatavolume Docker manages
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. Supabase takes 135 of them, all with defaults you can leave alone or tweak:
HOSTNAME, defaults to0.0.0.0STUDIO_PG_META_URL, defaults tohttp://supabase-meta:8080POSTGRES_PORT, defaults to5432POSTGRES_HOST, defaults tosupabase-dbPOSTGRES_DB, defaults topostgresPOSTGRES_PASSWORD, pulled from your own environmentPG_META_CRYPTO_KEY, pulled from your own environmentPGRST_DB_SCHEMAS, defaults topublic,storage,graphql_publicPGRST_DB_MAX_ROWS, defaults to1000PGRST_DB_EXTRA_SEARCH_PATH, defaults topublicDEFAULT_ORGANIZATION_NAME, defaults toDefault OrganizationDEFAULT_PROJECT_NAME, defaults toDefault ProjectOPENAI_API_KEY, pulled from your own environmentSUPABASE_URL, defaults tohttp://supabase-kong:5000SUPABASE_PUBLIC_URL, pulled from your own environmentSUPABASE_ANON_KEY, defaults toeyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoiYW5vbiIsImlzcyI6InN1cGFiYXNlIiwiaWF0IjoxNzAwMDAwMDAwLCJleHAiOjIwMDAwMDAwMDB9.6ldkvHM8WjwyHI_tKbJOgWu-VbulTx9jmeuEvNGSFkYSUPABASE_SERVICE_KEY, defaults toeyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJyb2xlIjoic2VydmljZV9yb2xlIiwiaXNzIjoic3VwYWJhc2UiLCJpYXQiOjE3MDAwMDAwMDAsImV4cCI6MjAwMDAwMDAwMH0.mjENke8J4x_734atFXjInx76tWeHpG_5y1KaXY_3SmgAUTH_JWT_SECRET, defaults tosuper-secret-jwt-token-with-at-least-32-characters-longSUPABASE_PUBLISHABLE_KEY, pulled from your own environmentSUPABASE_SECRET_KEY, pulled from your own environmentENABLED_FEATURES_LOGS_ALL, defaults tofalseSNIPPETS_MANAGEMENT_FOLDER, defaults to/app/snippetsEDGE_FUNCTIONS_MANAGEMENT_FOLDER, defaults to/app/edge-functionsKONG_DATABASE, defaults tooffKONG_DECLARATIVE_CONFIG, defaults to/usr/local/kong/kong.ymlKONG_DNS_ORDER, defaults toLAST,A,CNAMEKONG_DNS_NOT_FOUND_TTL, defaults to1KONG_PLUGINS, defaults torequest-transformer,cors,key-auth,acl,basic-auth,request-termination,ip-restriction,post-functionKONG_NGINX_PROXY_PROXY_BUFFER_SIZE, defaults to160kKONG_NGINX_PROXY_PROXY_BUFFERS, defaults to64 160kKONG_NGINX_WORKER_PROCESSES, defaults to2KONG_PROXY_ACCESS_LOG, defaults to/dev/stdout combinedANON_KEY_ASYMMETRIC, pulled from your own environmentSERVICE_ROLE_KEY_ASYMMETRIC, pulled from your own environmentDASHBOARD_USERNAME, pulled from your own environmentDASHBOARD_PASSWORD, pulled from your own environmentKONG_PROXY_LISTEN, defaults to0.0.0.0:5000GOTRUE_API_HOST, defaults to0.0.0.0GOTRUE_API_PORT, defaults to9999API_EXTERNAL_URL, pulled from your own environmentGOTRUE_DB_DRIVER, defaults topostgresGOTRUE_DB_DATABASE_URL, defaults topostgres://supabase_auth_admin:POSTGRES_PASSWORD@supabase-db:5432/postgresGOTRUE_SITE_URL, pulled from your own environmentGOTRUE_URI_ALLOW_LIST, pulled from your own environmentGOTRUE_DISABLE_SIGNUP, defaults tofalseGOTRUE_JWT_ADMIN_ROLES, defaults toservice_roleGOTRUE_JWT_AUD, defaults toauthenticatedGOTRUE_JWT_DEFAULT_GROUP_NAME, defaults toauthenticatedGOTRUE_JWT_EXP, defaults to3600GOTRUE_JWT_SECRET, defaults tosuper-secret-jwt-token-with-at-least-32-characters-longGOTRUE_JWT_ISSUER, defaults toAPI_EXTERNAL_URL/auth/v1GOTRUE_EXTERNAL_EMAIL_ENABLED, defaults totrueGOTRUE_EXTERNAL_ANONYMOUS_USERS_ENABLED, defaults tofalseGOTRUE_MAILER_AUTOCONFIRM, defaults totrueGOTRUE_SMTP_ADMIN_EMAIL, defaults to[email protected]GOTRUE_SMTP_HOST, pulled from your own environmentGOTRUE_SMTP_PORT, defaults to587GOTRUE_SMTP_USER, pulled from your own environmentGOTRUE_SMTP_PASS, pulled from your own environmentGOTRUE_SMTP_SENDER_NAME, defaults toSupabaseGOTRUE_MAILER_URLPATHS_INVITE, defaults to/auth/v1/verifyGOTRUE_MAILER_URLPATHS_CONFIRMATION, defaults to/auth/v1/verifyGOTRUE_MAILER_URLPATHS_RECOVERY, defaults to/auth/v1/verifyGOTRUE_MAILER_URLPATHS_EMAIL_CHANGE, defaults to/auth/v1/verifyGOTRUE_EXTERNAL_PHONE_ENABLED, defaults tofalseGOTRUE_SMS_AUTOCONFIRM, defaults tofalsePGRST_DB_URI, defaults topostgres://authenticator:POSTGRES_PASSWORD@supabase-db:5432/postgresPGRST_DB_ANON_ROLE, defaults toanonPGRST_JWT_SECRET, defaults tosuper-secret-jwt-token-with-at-least-32-characters-longPGRST_DB_USE_LEGACY_GUCS, defaults tofalsePGRST_APP_SETTINGS_JWT_SECRET, defaults tosuper-secret-jwt-token-with-at-least-32-characters-longPGRST_APP_SETTINGS_JWT_EXP, defaults to3600PORT, defaults to4000DB_HOST, defaults tosupabase-dbDB_PORT, defaults to5432DB_USER, defaults tosupabase_adminDB_PASSWORD, pulled from your own environmentDB_NAME, defaults topostgresDB_AFTER_CONNECT_QUERY, defaults toSET search_path TO _realtimeDB_ENC_KEY, defaults tosupabaserealtimeAPI_JWT_SECRET, defaults tosuper-secret-jwt-token-with-at-least-32-characters-longSECRET_KEY_BASE, pulled from your own environmentMETRICS_JWT_SECRET, defaults tosuper-secret-jwt-token-with-at-least-32-characters-longERL_AFLAGS, defaults to-proto_dist inet_tcpDNS_NODES, defaults to''RLIMIT_NOFILE, defaults to10000APP_NAME, defaults torealtimeSEED_SELF_HOST, defaults totrueRUN_JANITOR, defaults totrueDISABLE_HEALTHCHECK_LOGGING, defaults totrueANON_KEY, pulled from your own environmentSERVICE_KEY, pulled from your own environmentPOSTGREST_URL, defaults tohttp://supabase-rest:3000DATABASE_URL, defaults toecto://supabase_admin:POSTGRES_PASSWORD@supabase-db:5432/_supabaseSTORAGE_PUBLIC_URL, pulled from your own environmentREQUEST_ALLOW_X_FORWARDED_PATH, defaults totrueFILE_SIZE_LIMIT, defaults to52428800STORAGE_BACKEND, defaults tofileGLOBAL_S3_BUCKET, pulled from your own environmentFILE_STORAGE_BACKEND_PATH, defaults to/var/lib/storageTENANT_ID, defaults tosupabaseREGION, defaults tolocalENABLE_IMAGE_TRANSFORMATION, defaults totrueIMGPROXY_URL, defaults tohttp://supabase-imgproxy:5001S3_PROTOCOL_ACCESS_KEY_ID, pulled from your own environmentS3_PROTOCOL_ACCESS_KEY_SECRET, pulled from your own environmentIMGPROXY_BIND, defaults to:5001IMGPROXY_LOCAL_FILESYSTEM_ROOT, defaults to/IMGPROXY_USE_ETAG, defaults totrueIMGPROXY_AUTO_WEBP, defaults totrueIMGPROXY_MAX_SRC_RESOLUTION, defaults to16.8PG_META_PORT, defaults to8080PG_META_DB_HOST, defaults tosupabase-dbPG_META_DB_PORT, defaults to5432PG_META_DB_NAME, defaults topostgresPG_META_DB_USER, defaults tosupabase_adminPG_META_DB_PASSWORD, pulled from your own environmentCRYPTO_KEY, pulled from your own environmentJWT_SECRET, defaults tosuper-secret-jwt-token-with-at-least-32-characters-longSUPABASE_SERVICE_ROLE_KEY, pulled from your own environmentSUPABASE_PUBLISHABLE_KEYS, defaults to{"default":""}SUPABASE_SECRET_KEYS, defaults to{"default":""}SUPABASE_DB_URL, defaults topostgresql://postgres:POSTGRES_PASSWORD@supabase-db:5432/postgresVERIFY_JWT, defaults tofalsePGPORT, defaults to5432PGPASSWORD, pulled from your own environmentPGDATABASE, defaults topostgresJWT_EXP, defaults to3600CLUSTER_POSTGRES, defaults totrueVAULT_ENC_KEY, pulled from your own environmentPOOLER_TENANT_ID, defaults tosupabasePOOLER_DEFAULT_POOL_SIZE, defaults to20POOLER_MAX_CLIENT_CONN, defaults to100POOLER_POOL_MODE, defaults totransactionDB_POOL_SIZE, defaults to5
Restart policy
The restart policy here is unless-stopped, so Docker restarts Supabase after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Networking
Portainer puts these services on one shared private network, so they can find each other by name (like studio) while only the ports above are open to you.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set Supabase up. Add the template list to Portainer once, then deploying Supabase is a click rather than a wall of config.