
![Sealskin]() Sealskin
Container
Sealskin is a self-hosted, client-server platform that enables users to run powerful, containerized desktop applications streamed directly to a web browser. It uses a browser extension to intercept user actions—such as clicking a link or downloading a file and redirects them to a secure, isolated application environment running on a remote server.
Image details
Source details
Configuration
TypeContainerlinuxlinuxserver/sealskin:latest8443:8443/tcp8000:8000/tcp/config : /srv/lsio/sealskin/config/storage : /srv/lsio/sealskin/storage/var/run/docker.sock : /var/run/docker.sockPUID=1000PGID=1000TZ=Etc/UTCHOST_URL=IP or subdomain.doman.comunless-stoppedTemplate by technorabilia
Report issueNotes
Ensure to create the following volume directories on the host file system, or modify the paths in the volume mapping section under the advanced options below, as needed.
mkdir -p /srv/lsio/sealskin/config
mkdir -p /srv/lsio/sealskin/storage
Standalone Install
Select an install method, to see config/commands for deploying Sealskin
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select Sealskin, fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
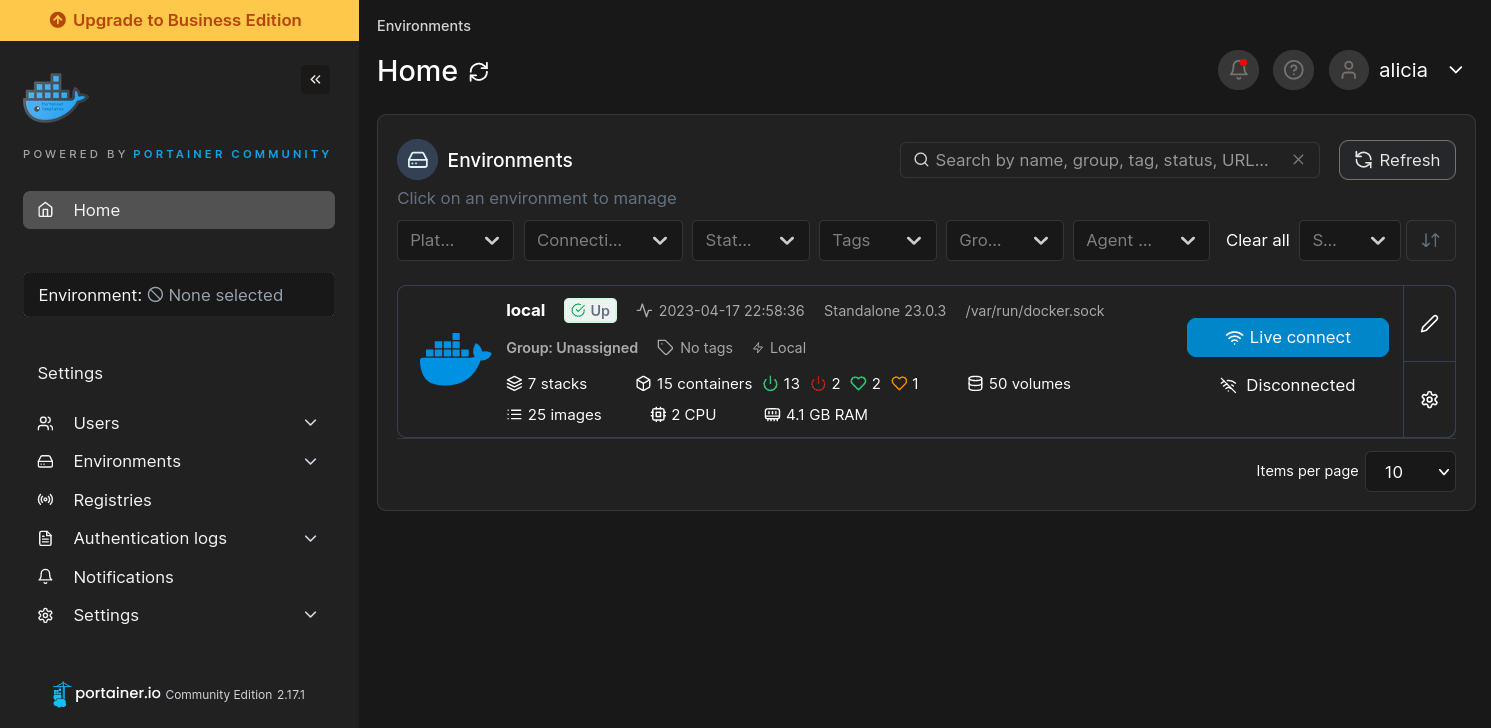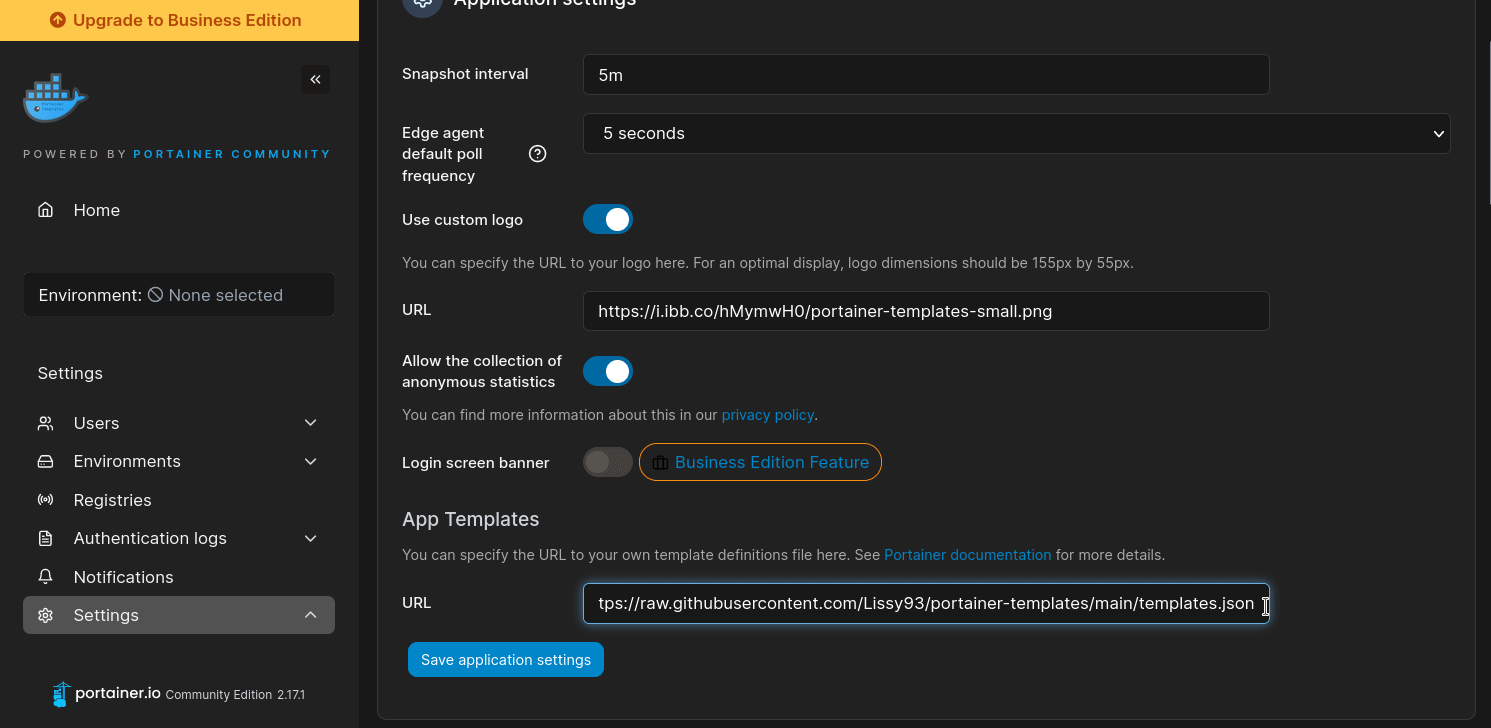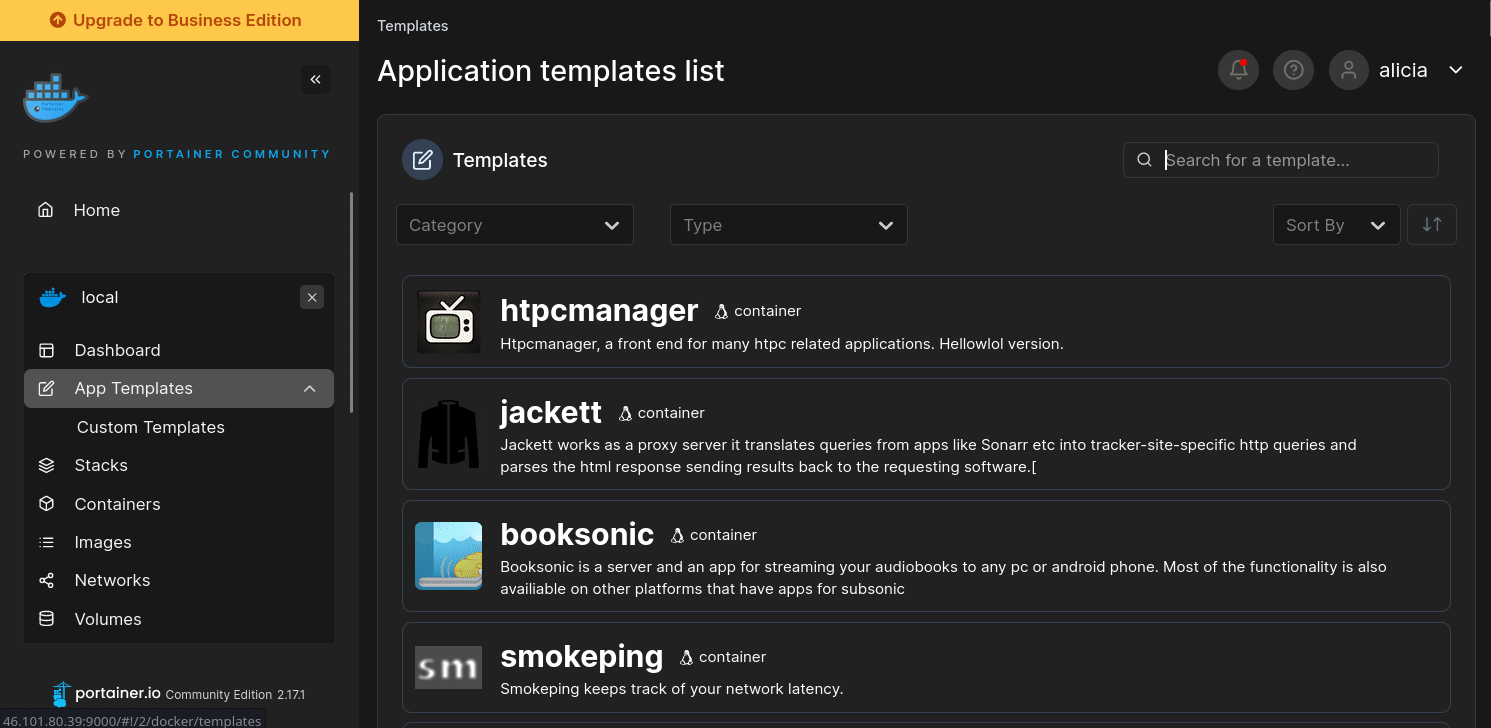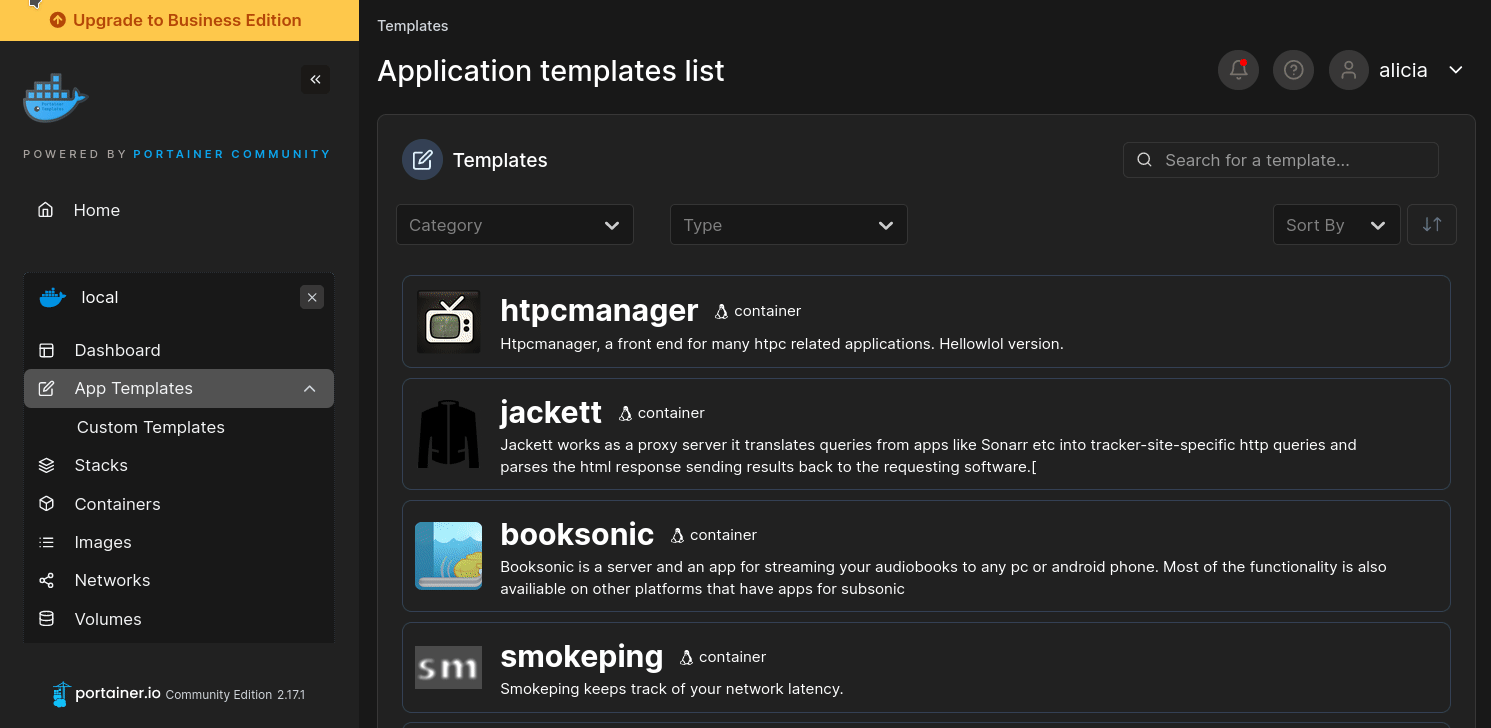
More install options in our documentation, or see selkies-project/sealskin for app-specific guidance.
The LinuxServer.io team brings you another container release featuring:
- regular and timely application updates
- easy user mappings (PGID, PUID)
- custom base image with s6 overlay
- weekly base OS updates with common layers across the entire LinuxServer.io ecosystem to minimise space usage, down time and bandwidth
- regular security updates
Find us at:
- Blog - all the things you can do with our containers including How-To guides, opinions and much more!
- Discord - realtime support / chat with the community and the team.
- Discussions - post on our community forum.
- GitHub - view the source for all of our repositories.
- Open Collective - please consider helping us by either donating or contributing to our budget
linuxserver/sealskin




Sealskin is a self-hosted browser isolation and remote application streaming platform. It runs desktop applications in isolated containers on a server you control and streams them to any browser or phone. Clients include a browser extension, mobile apps, and a web app served by the server itself. Each turns links, files, downloads, and text selections into something you open remotely instead of locally, so nothing from the web runs on the device in front of you.
Supported Architectures
We utilise the docker manifest for multi-platform awareness. More information is available from docker here and our announcement here.Simply pulling
lscr.io/linuxserver/sealskin:latest should retrieve the correct image for your arch, but you can also pull specific arch images via tags.The architectures supported by this image are:
| Architecture | Available | Tag |
|---|---|---|
| x86-64 | ✅ | amd64-\ |
| arm64 | ✅ | arm64v8-\ |
Application Setup
This image hosts the server component of the SealSkin platform: the API, the Caddy proxy, and the web app it serves. The full documentation lives at selkies-project.github.io/sealskin.Clients
| Client | Where | Notes |
|---|---|---|
| Chrome, Edge, Brave and other Chromium browsers | Chrome Web Store | Full feature set, works with the self-signed certificate. |
| Firefox | Firefox Add-ons | Requires a trusted certificate. |
| iOS | App Store | Requires a trusted certificate. |
| Android | Google Play | Requires a trusted certificate. |
| Any browser | https://<server>:8443/ | The web app: launcher, sessions, files and dashboard with nothing installed. Requires a trusted certificate. |
>!NOTE >If you are not using a trusted SSL certificate (the default is self signed in
/config/ssl) then only the Chrome extension can be used, and whatever port is mapped to 8000 must also be reachable so it can fall back to E2EE over HTTP. Firefox, the mobile apps and the web app enforce HTTPS.First run
On the first start with an empty/config the container generates a self-signed certificate for the proxy and the server's RSA key, then the server finds no administrator and writes two credentials for the built-in admin account:/config/root_keyis an application key for the web app. Openhttps://<server>:8443/and paste it in to sign in./config/admin.jsonis the key file for the browser extension and mobile apps. IfHOST_URLwas set it can be imported as is, otherwise edit it and replace the stringHOST_URLwith your server's IP or hostname.
>!NOTE >Copy both files somewhere safe and delete them from the server. They are the only copy of that private key, the server keeps just the public half.
Once signed in you can install applications from the App Store, create users and groups, and make application keys for other devices from the dashboard.
On the web the root key is the only sign-in the server handles itself. Everyone else signs in through an identity provider (OpenID Connect or SAML) or a reverse proxy that signs users in, whose groups make administrators and carry limits. See Signing in before inviting a second person. Extension and mobile users can also be given key files from the Users panel.
Scripted installation
Included in this repository is a helper script to spin up SealSkin with a trusted certificate using Duck DNS. Before using this script please navigate to https://www.duckdns.org/, log in, make a sub domain, and get your token.mkdir sealskin
cd sealskin
bash <(curl -sSL https://raw.githubusercontent.com/linuxserver/docker-sealskin/refs/heads/master/install.sh)This will set up pathing, ownership, the compose file, and a trusted wildcard SSL certificate for Duck DNS.
You can also renew your wildcard SSL certificate by running the same script again in the same directory.
cd sealskin
bash <(curl -sSL https://raw.githubusercontent.com/linuxserver/docker-sealskin/refs/heads/master/install.sh)Basic Requirements
- The container must be named
sealskin. The server inspects its own container to learn the host paths behind/configand/storage, the externally mapped ports, and the Docker network. The name is also the server's identity in its own records, so a container recreated under another name is another node. If you cannot keep the name, sethostname: sealskinorSEALSKIN_NODE_NAME. - The Docker socket is required. Every session is a container the server starts through it. If launches fail with a permission error, make the socket group writable on the host with
sudo chmod g+rw /var/run/docker.sock. PUIDandPGIDown everything. The server, its files and every session container run as that user, so/configand/storageon the host must be writable by it.- Ports. 8443 carries the web app, the API and the streamed sessions. 8000 is only needed for the Chrome self-signed fallback. 8444 is the peer listener, only publish it to join several servers into a cluster.
The server can be exposed directly to the internet, its own Caddy instance terminates TLS and authenticates every request to a session. It can also run behind a reverse proxy by setting
SEALSKIN_PUBLIC_URL and SEALSKIN_TRUSTED_PROXIES, plus SEALSKIN_HTTP_PORT for a proxy that terminates TLS, with guides for SWAG, Traefik, Nginx Proxy Manager and Caddy. Every environment variable the server reads is listed in the Settings Reference. The same image also runs on Kubernetes from the upstream manifest, with sessions as pods.NVIDIA Support
NVIDIA support requires the proprietary driver 580 or newer (no MIT/GPL kernel modules) with thenvidia-drm.modeset=1 kernel parameter set, and the NVIDIA Container Toolkit v1.20.1 or higher registered with Docker. The toolkit's refresh service creates the modeset device at boot so headless hosts need nothing more.Key & Certificate Management
The server requires several cryptographic keys to function. You can either let the container perform an automatic setup on its first run or provide your own for more control.Automatic First-Run Setup (Recommended)
On the first launch with an empty/config volume:- An init process generates the mandatory server key (
ssl/server_key.pem) and a self-signed SSL certificate for the proxy (ssl/proxy_key.pem,ssl/proxy_cert.pem). - The server detects that no administrator exists, creates the default user
admin, and writes/config/admin.jsonand/config/root_keyas described above.
Manual Pre-Configuration (Advanced)
Place the files in the/config volume before the first launch.- To use a custom Admin Key:
1.  Generate your own RSA keypair.
2.  Create a file containing only your **public key** PEM data at `/path/to/config/.config/sealskin/keys/admins/admin`.
3. The server will detect this file and write no `admin.json`. You use your private key to log in from the extension, and `admin` signs in to the web app with the root key alone.- To use a custom SSL Certificate:
* Place your certificate and private key at `/path/to/config/ssl/proxy_cert.pem` and `/path/to/config/ssl/proxy_key.pem`. This overrides the self-signed certificate and can be replaced later with a restart.- To use a custom Server E2EE Key:
*   Place your RSA private key at `/path/to/config/ssl/server_key.pem`. This is the core key for the API's end-to-end encryption and validates the server when a client is configured with its public key.
    *   **Generation Command:** `openssl genpkey -algorithm RSA -out /path/to/config/ssl/server_key.pem -pkeyopt rsa_keygen_bits:4096`
    *   **Extraction Command (public key for clients):** `openssl rsa -in server_key.pem -pubout`
Upgrading from 0.3
Nothing on disk needs changing, existing users, groups, installed apps, templates and sessions load as before and key files keep working. On the first start after the upgrade the server writes/config/root_key for the web app, sign in with it then copy and delete the file. Keep the container name sealskin or set SEALSKIN_NODE_NAME so the server keeps its identity. Collaboration rooms need application images with a Selkies release after 2.0.0, and NVIDIA hosts need the Container Toolkit v1.20.1 or higher.Usage
To help you get started creating a container from this image you can either use docker-compose or the docker cli.>!NOTE >Unless a parameter is flagged as 'optional', it is mandatory and a value must be provided.
docker-compose (recommended, click here for more info)
---
services:
  sealskin:
    image: lscr.io/linuxserver/sealskin:latest
    container_name: sealskin
    environment:
      - PUID=1000
      - PGID=1000
      - TZ=Etc/UTC
      - "HOST_URL=IP or subdomain.domain.com" #optional
    volumes:
      - /path/to/sealskin/config:/config
      - /path/to/sealskin/storage:/storage
      - /var/run/docker.sock:/var/run/docker.sock
    ports:
      - 8443:8443
      - 8000:8000 #optional
      - 8444:8444 #optional
    restart: unless-stopped
docker cli (click here for more info)
docker run -d \
  --name=sealskin \
  -e PUID=1000 \
  -e PGID=1000 \
  -e TZ=Etc/UTC \
  -e HOST_URL="IP or subdomain.domain.com" `#optional` \
  -p 8443:8443 \
  -p 8000:8000 `#optional` \
  -p 8444:8444 `#optional` \
  -v /path/to/sealskin/config:/config \
  -v /path/to/sealskin/storage:/storage \
  -v /var/run/docker.sock:/var/run/docker.sock \
  --restart unless-stopped \
  lscr.io/linuxserver/sealskin:latest
Parameters
Containers are configured using parameters passed at runtime (such as those above). These parameters are separated by a colon and indicate<external>:<internal> respectively. For example, -p 8080:80 would expose port 80 from inside the container to be accessible from the host's IP on port 8080 outside the container.| Parameter | Function |
|---|---|
-p 8443:8443 | HTTPS Sessions and API communication port. |
-p 8000 | HTTP fallback API port, only needed by the Chrome extension with a self-signed certificate. |
-p 8444 | Peer listener, only needed to join several servers into a cluster. |
-e PUID=1000 | for UserID - see below for explanation |
-e PGID=1000 | for GroupID - see below for explanation |
-e TZ=Etc/UTC | specify a timezone to use, see this list. |
-e HOSTURL=IP or subdomain.domain.com | On initial setup this will be used to fill in the default admin configuration file in the /config directory, if unset the string HOSTURL will need to be replaced. |
-v /config | All configuration files and metadata for the application. |
-v /storage | All file storage for home directories and ephemeral mounts. |
-v /var/run/docker.sock | Docker socket, required to spin up application containers. |
Environment variables from files (Docker secrets)
You can set any environment variable from a file by using a special prependFILE__.As an example:
-e FILE__MYVAR=/run/secrets/mysecretvariableWill set the environment variable
MYVAR based on the contents of the /run/secrets/mysecretvariable file.Umask for running applications
For all of our images we provide the ability to override the default umask settings for services started within the containers using the optional-e UMASK=022 setting.
Keep in mind umask is not chmod it subtracts from permissions based on it's value it does not add. Please read up here before asking for support.User / Group Identifiers
When using volumes (-v flags), permissions issues can arise between the host OS and the container, we avoid this issue by allowing you to specify the user PUID and group PGID.Ensure any volume directories on the host are owned by the same user you specify and any permissions issues will vanish like magic.
In this instance
PUID=1000 and PGID=1000, to find yours use id your_user as below:id your_userExample output:
uid=1000(your_user) gid=1000(your_user) groups=1000(your_user)Docker Mods
We publish various Docker Mods to enable additional functionality within the containers. The list of Mods available for this image (if any) as well as universal mods that can be applied to any one of our images can be accessed via the dynamic badges above.
Support Info
- Shell access whilst the container is running:
```bash
docker exec -it sealskin /bin/bash
```- To monitor the logs of the container in realtime:
```bash
docker logs -f sealskin
```- Container version number:
```bash
docker inspect -f '{{ index .Config.Labels "build_version" }}' sealskin
```- Image version number:
```bash
docker inspect -f '{{ index .Config.Labels "build_version" }}' lscr.io/linuxserver/sealskin:latest
```
Updating Info
Most of our images are static, versioned, and require an image update and container recreation to update the app inside. With some exceptions (noted in the relevant readme.md), we do not recommend or support updating apps inside the container. Please consult the Application Setup section above to see if it is recommended for the image.Below are the instructions for updating containers:
Via Docker Compose
- Update images:
* All images:

    ```bash
    docker-compose pull
    ```

* Single image:

    ```bash
    docker-compose pull sealskin
```- Update containers:
* All containers:

    ```bash
    docker-compose up -d
    ```

* Single container:

    ```bash
    docker-compose up -d sealskin
```- You can also remove the old dangling images:
```bash
docker image prune
```
Via Docker Run
- Update the image:
```bash
docker pull lscr.io/linuxserver/sealskin:latest
```- Stop the running container:
```bash
docker stop sealskin
```- Delete the container:
```bash
docker rm sealskin
```- Recreate a new container with the same docker run parameters as instructed above (if mapped correctly to a host folder, your
/configfolder and settings will be preserved) - You can also remove the old dangling images:
```bash
docker image prune
```
Image Update Notifications - Diun (Docker Image Update Notifier)
>!TIP >We recommend Diun for update notifications. Other tools that automatically update containers unattended are not recommended or supported.Building locally
If you want to make local modifications to these images for development purposes or just to customize the logic:git clone https://github.com/linuxserver/docker-sealskin.git
cd docker-sealskin
docker build \
--no-cache \
--pull \
-t lscr.io/linuxserver/sealskin:latest .The ARM variants can be built on x8664 hardware and vice versa using
lscr.io/linuxserver/qemu-staticdocker run --rm --privileged lscr.io/linuxserver/qemu-static --resetOnce registered you can define the dockerfile to use with
-f Dockerfile.aarch64.Versions
- 20.10.26: - Update docs and installer for the 0.4.0 release: web app and root key sign in, reverse proxy support, cluster peer port.
- 05.09.26: - Install Sealskin from the upstream Python wheel, rebase to Alpine 3.24.
- 11.02.26: - Rebase to Alpine 3.23.
- 19.01.26: - Fix init race condition.
- 17.01.26: - Update docs to remove network and port requirement, add link to Firefox add on.
- 08.01.26: - Improve permission fixing.
- 31.10.25: - Initial Release.
Serve Sealskin on your own domain behind Caddy, Nginx or Traefik. Fill in your domain and copy the result. It's a starting point, some apps need their own base URL or extra headers set too.
Proxying sealskin.example.com to https://Sealskin:8443
Add this to your Caddyfile
sealskin.example.com {
	reverse_proxy https://Sealskin:8443 {
		transport http {
			tls_insecure_skip_verify
		}
	}
}Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs Sealskin - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Port already in use
If deployment fails with "Bind for 0.0.0.0:8443 failed: port is already allocated", something else on your server is using that port.
- Find what's using it:
sudo ss -tlnp | grep :8443 - Stop the other service, or pick a different host port. In
8443:8443only the left number is yours to change, the right one belongs to the app.
Running but the page won't load
The container is up but nothing appears in your browser.
- Use your server's real IP:
http://your-server-ip:8000. The 0.0.0.0 link Portainer shows isn't a real address. - Give it a minute after first deploy, Sealskin can take a while to initialise.
- Make sure your firewall allows the port, e.g.
sudo ufw allow 8000
Permission denied on volumes
If the logs show "permission denied", the app can't write to its data folder on the host.
- Fix the ownership:
sudo chown -R 1000:1000 /srv/lsio/sealskin/config(and the same for the other mapped folders) - Or set the
PUIDandPGIDvariables (defaults 1000:1000) to match your own user, found withid $USER
Can't reach the Docker socket
Sealskin talks to Docker through /var/run/docker.sock. If the logs show
"permission denied while trying to connect to the Docker daemon socket", the app's user can't access it.
- Check the socket exists on the host:
ls -l /var/run/docker.sock - Run the container as root, or add the docker group's id to the container with
group_add.
Image won't pull
Test the pull directly on the host: docker pull linuxserver/sealskin:latest
- "manifest unknown" means the tag no longer exists. This template uses
latest, so try pinning a specific version instead. - "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- This image supports:
amd64, arm64 - Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect Sealskin --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue on selkies-project/sealskin
- Template not working: Open an issue on technorabilia/portainer-templates
- This website not working: Open an issue on lissy93/portainer-templates
A single container
Sealskin runs as one container, the simplest kind of app here. Just the one image to pull and nothing else wired up alongside it.
The app image
An image is the app packed up ready to go, everything Sealskin needs bundled into one download. This template pulls linuxserver/sealskin:latest, which Docker fetches once (about 84 MB) and then starts your own copy from.
Where the image comes from
Docker pulls its images from registries, public libraries of ready-built apps. Sealskin's comes from Docker Hub, published by linuxserver.
Version tags
The bit after the colon in the image name is the version tag. Here it's latest, which always points at the newest build, so a redeploy can bump you to a newer release without you asking. Newest right now is 0.4.0. Pin a specific tag if you would rather stay on one version.
Which machines it runs on
Every image is built for particular CPU types. This one ships for amd64, arm64, so it runs on both regular x86 servers and ARM boards like a Raspberry Pi.
Ports
A port is the door the app answers on. A mapping like 8443:8443 means it's reachable on port 8443 of your server, where the left number is yours to change and the right one belongs to the app. Once it's running, open http://your-server-ip:8000 in a browser. It opens:
8443:84438000:8000, likely the web interface
Volumes
A volume is where Sealskin keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/configfrom/srv/lsio/sealskin/configon the host/storagefrom/srv/lsio/sealskin/storageon the host/var/run/docker.sockfrom/var/run/docker.sockon the host (a socket it talks to, not storage)
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. Sealskin takes 4 of them, all with defaults you can leave alone or tweak:
PUID, defaults to1000. Run 'id [USER]' for the owner of the host volume directories to get the UID to use here.PGID, defaults to1000. Run 'id [USER]' for the owner of the host volume directories to get the GID to use here.TZ, defaults toEtc/UTC. Specify a timezone to use, see this list.HOST_URL, defaults toIP or subdomain.doman.com. On initial setup this will be used to fill in the default admin configuration file in the /config directory, if unset the string HOSTURL will need to be replaced. [OPTIONAL]
Restart policy
The restart policy here is unless-stopped, so Docker restarts Sealskin after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Users and permissions
The PUID and PGID settings tell it which user and group to act as on your host. Point them at your own account (find yours with id $USER) so the files it writes into your mounted folders come out owned by you rather than root.
Networking
Nothing custom is set, so Sealskin sits on Docker's default bridge network: its own private space that reaches the outside world only through the ports it publishes.
Container name
Once it's deployed, Portainer names the container Sealskin. That's what you'll spot in the containers list and use in commands like docker logs Sealskin.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Open source license
Sealskin is open source, released under the MPL-2.0 license. In plain terms the code is out in the open, so you're free to run it and change it to fit what you need.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set Sealskin up. Add the template list to Portainer once, then deploying Sealskin is a click rather than a wall of config.