
![Penpot]() Penpot
Stack
Penpot - the open-source design and prototyping platform (the Figma alternative): SVG-native, web-based, with real design-to-dev handoff. MPL-2.0. Frontend + backend + exporter on a managed Postgres and a noeviction Valkey.
Configuration
TypeComposelinuxPENPOT_OBJECTS_STORAGE_BACKEND=fsPENPOT_PUBLIC_URI=http://localhost:5000PENPOT_SECRET_KEY=''REDIS_AUTH=# openssl rand -hex 24S3_ACCESS_KEY=''S3_BUCKET_NAME=''S3_ENDPOINT=''S3_REGION=us-east-1S3_SECRET_KEY=''Template by deployable-sh·Source
Report issueServices
frontend
Configuration
Imagepenpotapp/frontend:2.16.08080PENPOT_FLAGS=disable-registration-domain-whitelist disable-email-verificationPENPOT_PUBLIC_URI=${PENPOT_PUBLIC_URI:-http://localhost:5000}PENPOT_BACKEND_URI=http://backend:6060PENPOT_EXPORTER_URI=http://exporter:6061unless-stoppedImage details
web
Configuration
Imagecaddy:2-alpinecaddy,reverse-proxy,--from,:5000,--to,frontend:80805000:5000unless-stoppedImage details
backend
Configuration
Imagepenpotapp/backend:2.16.06060/opt/data/assets : assetsPENPOT_FLAGS=disable-registration-domain-whitelist disable-email-verification enable-prepl-serverPENPOT_PUBLIC_URI=${PENPOT_PUBLIC_URI:-http://localhost:5000}PENPOT_SECRET_KEY=${PENPOT_SECRET_KEY}PENPOT_DATABASE_URI=postgresql://db:5432/penpotPENPOT_DATABASE_USERNAME=penpotPENPOT_DATABASE_PASSWORD=penpot-local-onlyPENPOT_REDIS_URI=redis://broker:6379/0PENPOT_OBJECTS_STORAGE_BACKEND=${PENPOT_OBJECTS_STORAGE_BACKEND:-fs}PENPOT_OBJECTS_STORAGE_FS_DIRECTORY=/opt/data/assetsAWS_ACCESS_KEY_ID=${S3_ACCESS_KEY:-}AWS_SECRET_ACCESS_KEY=${S3_SECRET_KEY:-}PENPOT_OBJECTS_STORAGE_S3_REGION=${S3_REGION:-us-east-1}PENPOT_OBJECTS_STORAGE_S3_BUCKET=${S3_BUCKET_NAME:-}PENPOT_OBJECTS_STORAGE_S3_ENDPOINT=${S3_ENDPOINT:-}PENPOT_TELEMETRY_ENABLED=falseunless-stoppedImage details
exporter
Configuration
Imagepenpotapp/exporter:2.16.06061PENPOT_PUBLIC_URI=http://frontend:8080PENPOT_SECRET_KEY=${PENPOT_SECRET_KEY}PENPOT_REDIS_URI=redis://broker:6379/0unless-stoppedImage details
broker
Configuration
Imagevalkey/valkey:8valkey-server,--maxmemory-policy,noeviction,--protected-mode,no6379unless-stoppedImage details
db
Configuration
Imagepostgres:15/var/lib/postgresql/data : dbdataPOSTGRES_USER=penpotPOSTGRES_PASSWORD=penpot-local-onlyPOSTGRES_DB=penpotunless-stoppedImage details
Standalone Install
Select an install method, to see config/commands for deploying Penpot
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
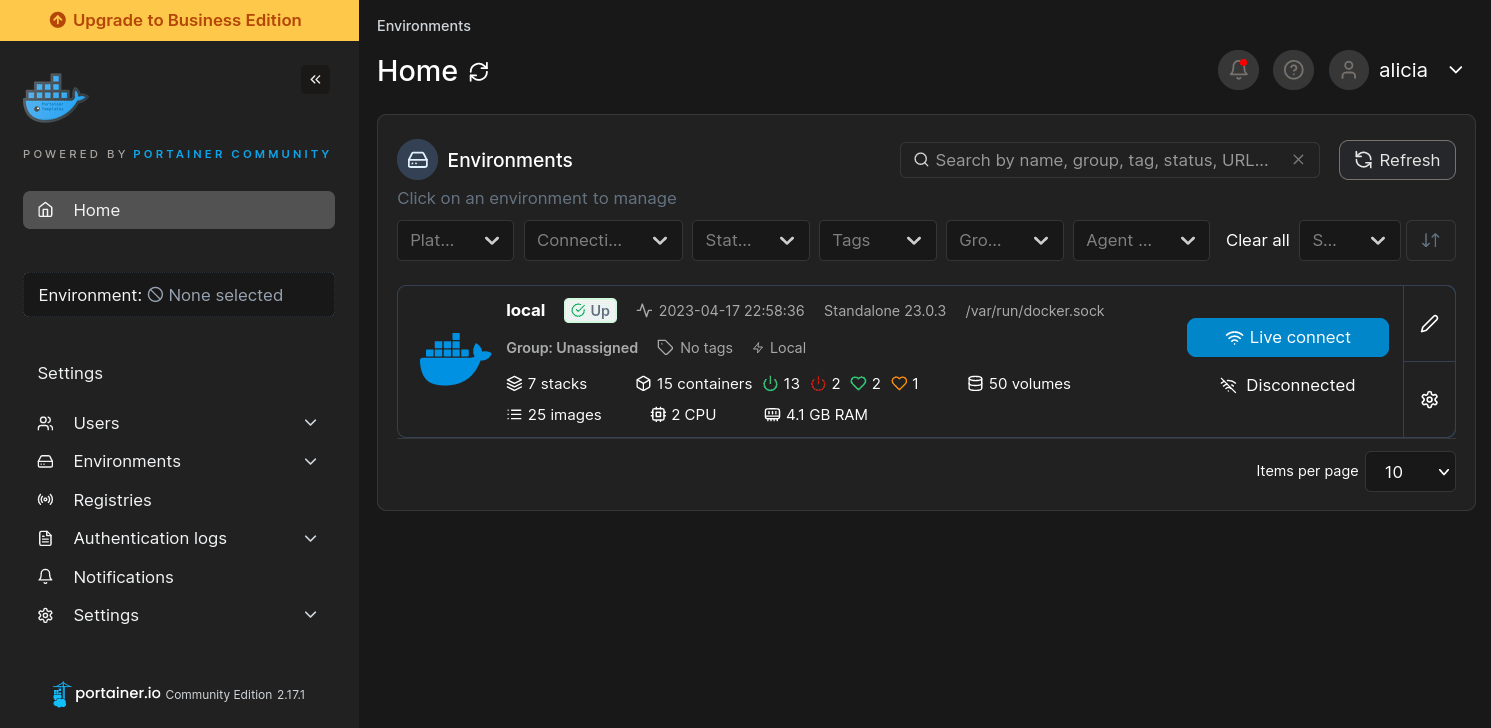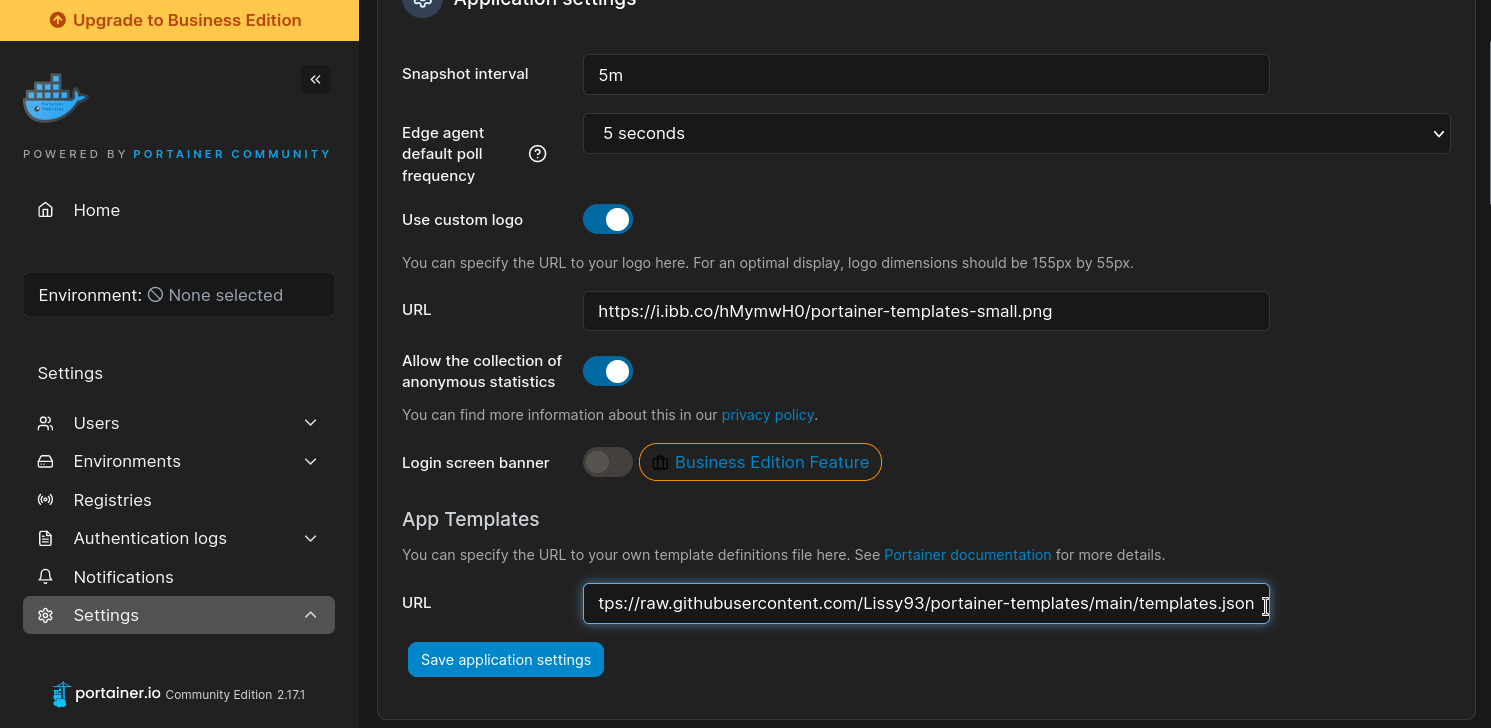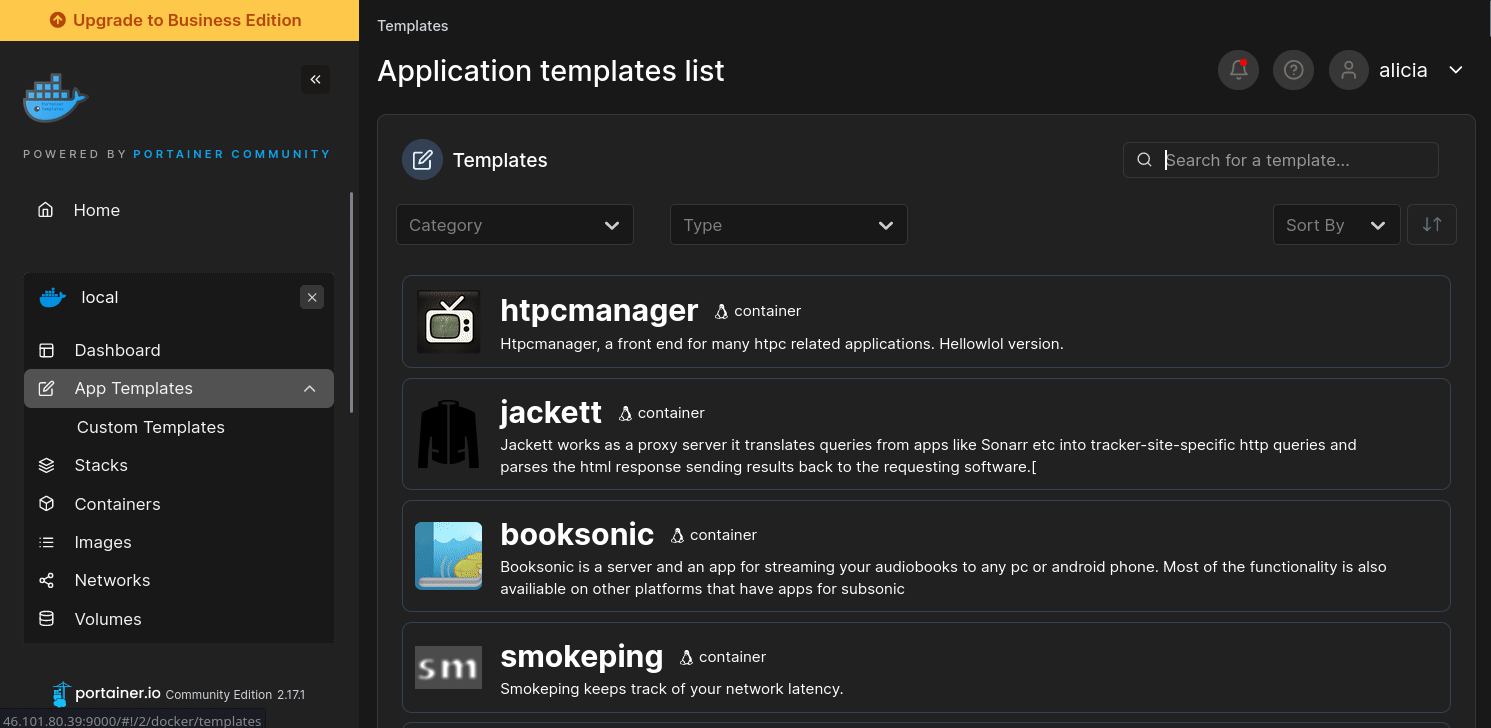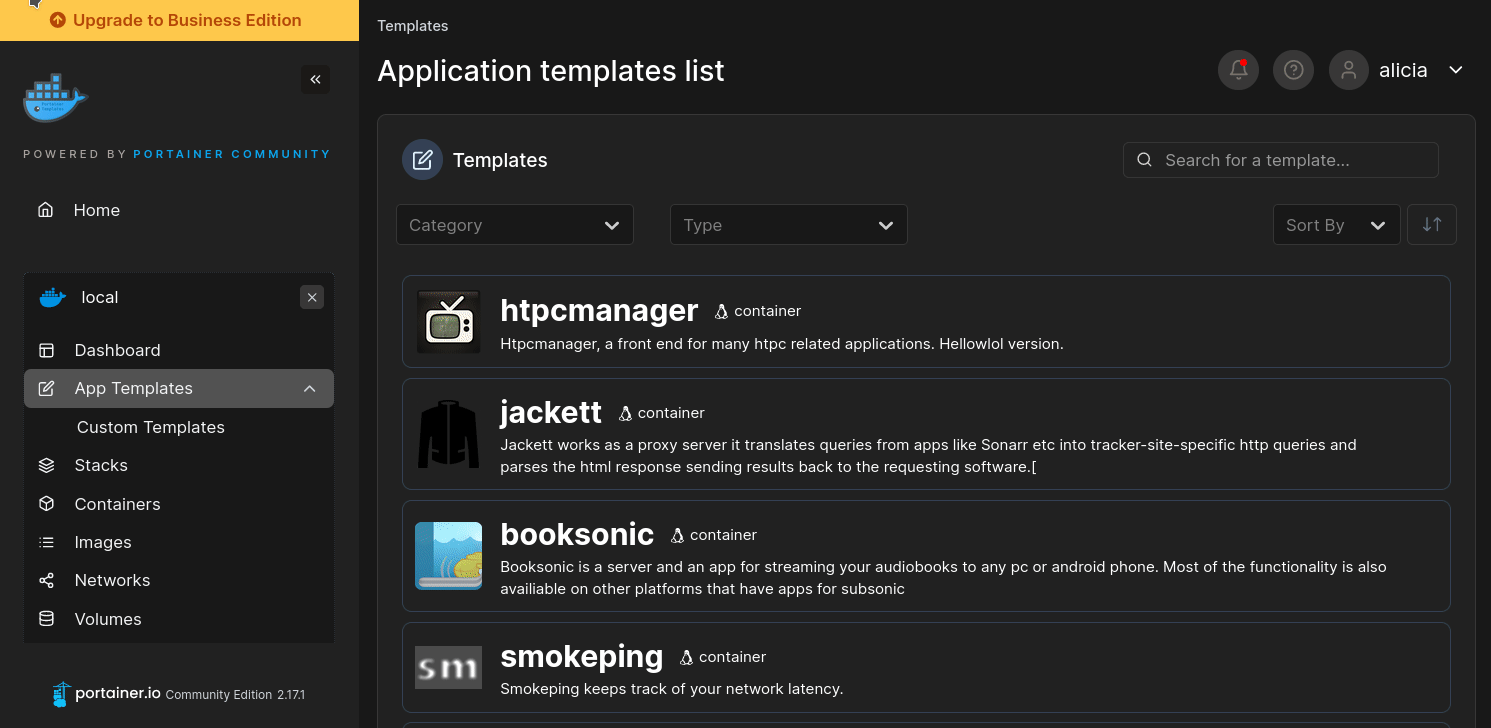
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select Penpot, fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
Original stackfile
The compose file this template deploys, straight from its repo:
name: penpot

services:
  frontend:
    image: penpotapp/frontend:2.16.0
    restart: unless-stopped
    environment:
      PENPOT_FLAGS: disable-registration-domain-whitelist disable-email-verification
      PENPOT_PUBLIC_URI: ${PENPOT_PUBLIC_URI:-http://localhost:5000}
      PENPOT_BACKEND_URI: http://backend:6060
      PENPOT_EXPORTER_URI: http://exporter:6061
    ports:
      - "8080"
    depends_on:
      - backend
      - exporter

  web:
    image: caddy:2-alpine
    command: ["caddy", "reverse-proxy", "--from", ":5000", "--to", "frontend:8080"]
    restart: unless-stopped
    ports:
      - "5000:5000"
    depends_on:
      - frontend

  backend:
    image: penpotapp/backend:2.16.0
    restart: unless-stopped
    environment:
      PENPOT_FLAGS: disable-registration-domain-whitelist disable-email-verification enable-prepl-server
      PENPOT_PUBLIC_URI: ${PENPOT_PUBLIC_URI:-http://localhost:5000}
      PENPOT_SECRET_KEY: ${PENPOT_SECRET_KEY}
      PENPOT_DATABASE_URI: postgresql://db:5432/penpot
      PENPOT_DATABASE_USERNAME: penpot
      PENPOT_DATABASE_PASSWORD: penpot-local-only
      PENPOT_REDIS_URI: redis://broker:6379/0
      PENPOT_OBJECTS_STORAGE_BACKEND: ${PENPOT_OBJECTS_STORAGE_BACKEND:-fs}
      PENPOT_OBJECTS_STORAGE_FS_DIRECTORY: /opt/data/assets
      AWS_ACCESS_KEY_ID: ${S3_ACCESS_KEY:-}
      AWS_SECRET_ACCESS_KEY: ${S3_SECRET_KEY:-}
      PENPOT_OBJECTS_STORAGE_S3_REGION: ${S3_REGION:-us-east-1}
      PENPOT_OBJECTS_STORAGE_S3_BUCKET: ${S3_BUCKET_NAME:-}
      PENPOT_OBJECTS_STORAGE_S3_ENDPOINT: ${S3_ENDPOINT:-}
      PENPOT_TELEMETRY_ENABLED: "false"
    ports:
      - "6060"
    volumes:
      - assets:/opt/data/assets
    depends_on:
      - db
      - broker

  exporter:
    image: penpotapp/exporter:2.16.0
    restart: unless-stopped
    environment:
      PENPOT_PUBLIC_URI: http://frontend:8080
      PENPOT_SECRET_KEY: ${PENPOT_SECRET_KEY}
      PENPOT_REDIS_URI: redis://broker:6379/0
    ports:
      - "6061"
    depends_on:
      - broker

  broker:
    image: valkey/valkey:8
    command: ["valkey-server", "--maxmemory-policy", "noeviction", "--protected-mode", "no"]
    restart: unless-stopped
    ports:
      - "6379"

  db:
    image: postgres:15
    restart: unless-stopped
    environment:
      POSTGRES_USER: penpot
      POSTGRES_PASSWORD: penpot-local-only
      POSTGRES_DB: penpot
    volumes:
      - dbdata:/var/lib/postgresql/data

volumes:
  assets:
  dbdata:
Or deploy it directly from the source:
git clone https://github.com/deployable-sh/stacks
cd stacks
docker compose -f penpot/compose.yaml up -d
More install options in our documentation.
Container Documentation
frontend Documentation
Penpot frontend
web Documentation
Caddy 2 is a powerful, enterprise-ready, open source web server with automatic HTTPS written in Go.
backend Documentation
Penpot backend
exporter Documentation
Penpot exporter
broker Documentation
Valkey is a high-performance data structure server that primarily serves key/value workloads.
db Documentation
The PostgreSQL object-relational database system provides reliability and data integrity.
Serve Penpot on your own domain behind Caddy, Nginx or Traefik. Fill in your domain and copy the result. It's a starting point, some apps need their own base URL or extra headers set too.
Proxying penpot.example.com to http://frontend:8080
Add this to your Caddyfile
penpot.example.com {
	reverse_proxy http://frontend:8080
}Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs <container> - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Port already in use
If deployment fails with "Bind for 0.0.0.0:5000 failed: port is already allocated", something else on your server is using that port.
- Find what's using it:
sudo ss -tlnp | grep :5000 - Stop the other service, or pick a different host port. In
5000:5000only the left number is yours to change, the right one belongs to the app.
Published on a random port
This template exposes 8080 without setting a host port,
so Docker picks a random free one on every deploy.
- Find it in the Ports column of Portainer's container list, or with
docker port <container>
Running but the page won't load
The container is up but nothing appears in your browser.
- Use your server's real IP:
http://your-server-ip:5000. The 0.0.0.0 link Portainer shows isn't a real address. - Give it a minute after first deploy, penpot can take a while to initialise.
- Make sure your firewall allows the port, e.g.
sudo ufw allow 5000
Image won't pull
Test the pull directly on the host: docker pull penpotapp/frontend:2.16.0
- "manifest unknown" means the tag no longer exists.
- "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect <container> --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Stack won't deploy
Compose stacks fail fast on small mistakes, and Portainer shows the reason just above the editor.
- YAML only accepts spaces for indentation, a single tab breaks the whole file.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue within penpot's repo
- Template not working: Open an issue on deployable-sh/stacks
- This website not working: Open an issue on lissy93/portainer-templates
A Compose stack
Penpot is a Compose stack, a set of containers (6 of them) defined in one file and brought up together by Portainer, then started and stopped as a single app.
The services
This stack is built from 6 containers that run side by side. Here's each one, with the image it runs and anything it waits for first:
frontendrunspenpotapp/frontend:2.16.0, starts after backend, exporterwebrunscaddy:2-alpine, starts after frontendbackendrunspenpotapp/backend:2.16.0, starts after db, brokerexporterrunspenpotapp/exporter:2.16.0, starts after brokerbrokerrunsvalkey/valkey:8dbrunspostgres:15
Ports
A port is the door the app answers on. A mapping like 5000:5000 means it's reachable on port 5000 of your server, where the left number is yours to change and the right one belongs to the app. It opens:
8080, published on a random host port5000:50006060, published on a random host port6061, published on a random host port6379, published on a random host port
Volumes
A volume is where Penpot keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/opt/data/assetskept in theassetsvolume Docker manages/var/lib/postgresql/datakept in thedbdatavolume Docker manages
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. Penpot takes 20 of them, all with defaults you can leave alone or tweak:
PENPOT_FLAGS, defaults todisable-registration-domain-whitelist disable-email-verification enable-prepl-serverPENPOT_PUBLIC_URI, defaults tohttp://frontend:8080PENPOT_BACKEND_URI, defaults tohttp://backend:6060PENPOT_EXPORTER_URI, defaults tohttp://exporter:6061PENPOT_SECRET_KEY, pulled from your own environmentPENPOT_DATABASE_URI, defaults topostgresql://db:5432/penpotPENPOT_DATABASE_USERNAME, defaults topenpotPENPOT_DATABASE_PASSWORD, defaults topenpot-local-onlyPENPOT_REDIS_URI, defaults toredis://broker:6379/0PENPOT_OBJECTS_STORAGE_BACKEND, defaults tofsPENPOT_OBJECTS_STORAGE_FS_DIRECTORY, defaults to/opt/data/assetsAWS_ACCESS_KEY_ID, pulled from your own environmentAWS_SECRET_ACCESS_KEY, pulled from your own environmentPENPOT_OBJECTS_STORAGE_S3_REGION, defaults tous-east-1PENPOT_OBJECTS_STORAGE_S3_BUCKET, pulled from your own environmentPENPOT_OBJECTS_STORAGE_S3_ENDPOINT, pulled from your own environmentPENPOT_TELEMETRY_ENABLED, defaults tofalsePOSTGRES_USER, defaults topenpotPOSTGRES_PASSWORD, defaults topenpot-local-onlyPOSTGRES_DB, defaults topenpot
Restart policy
The restart policy here is unless-stopped, so Docker restarts Penpot after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Networking
Portainer puts these services on one shared private network, so they can find each other by name (like frontend) while only the ports above are open to you.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set Penpot up. Add the template list to Portainer once, then deploying Penpot is a click rather than a wall of config.