
![Murmur]() Murmur
Container
Mumble is a voicechat program for gamers written on top of Qt and Opus. Murmur is the server backend for Mumble.
Image details
Source details
Configuration
TypeContainerlinuxgoofball222/murmur:latest64738:64738/tcp64738:64738/udp/etc/localtime : /etc/localtime:ro/opt/murmur/config : /portainer/Files/Config/Murmur/opt/murmur/data : /portainer/Files/Murmur/data/opt/murmur/log : /portainer/Files/Murmur/logPUID=1000PGID=100TZ=''unless-stoppedTemplate by xneo1
Standalone Install
Select an install method, to see config/commands for deploying Murmur
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
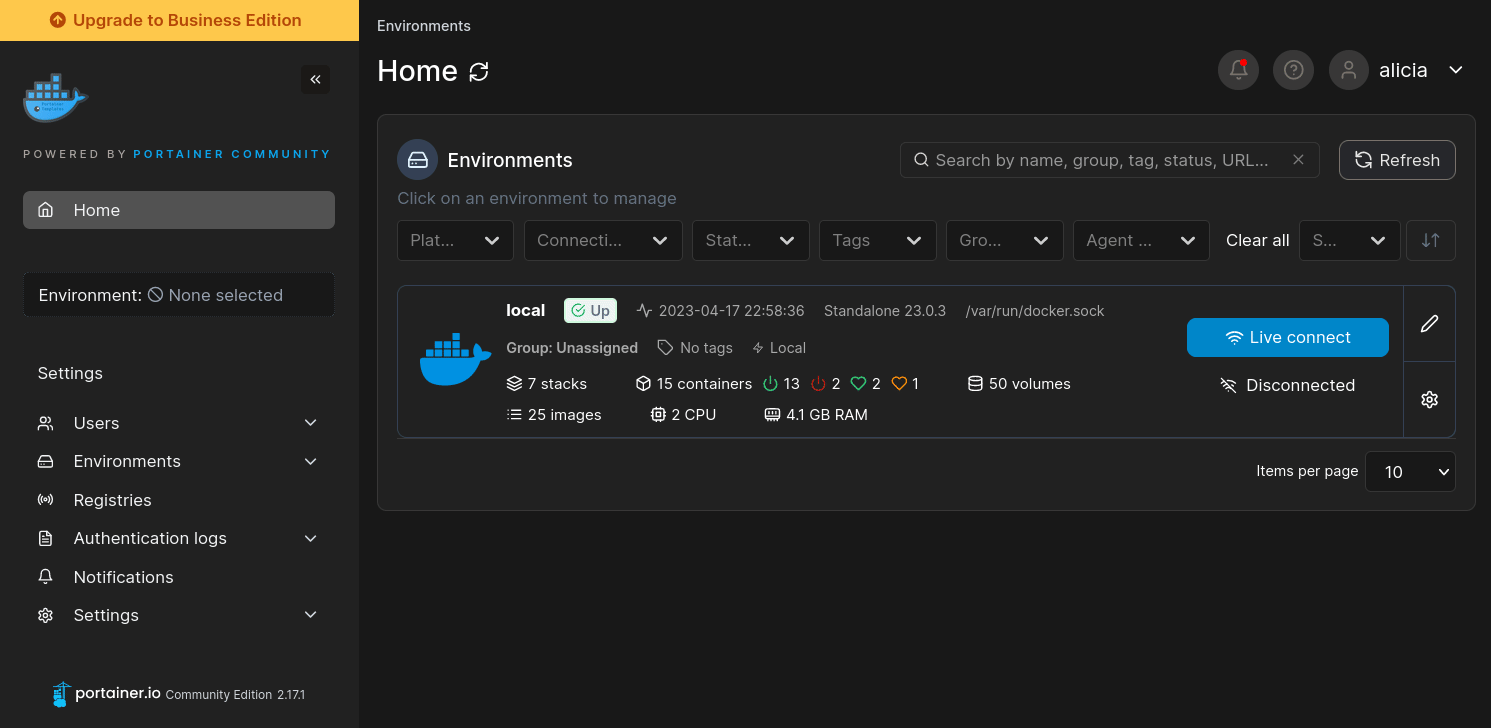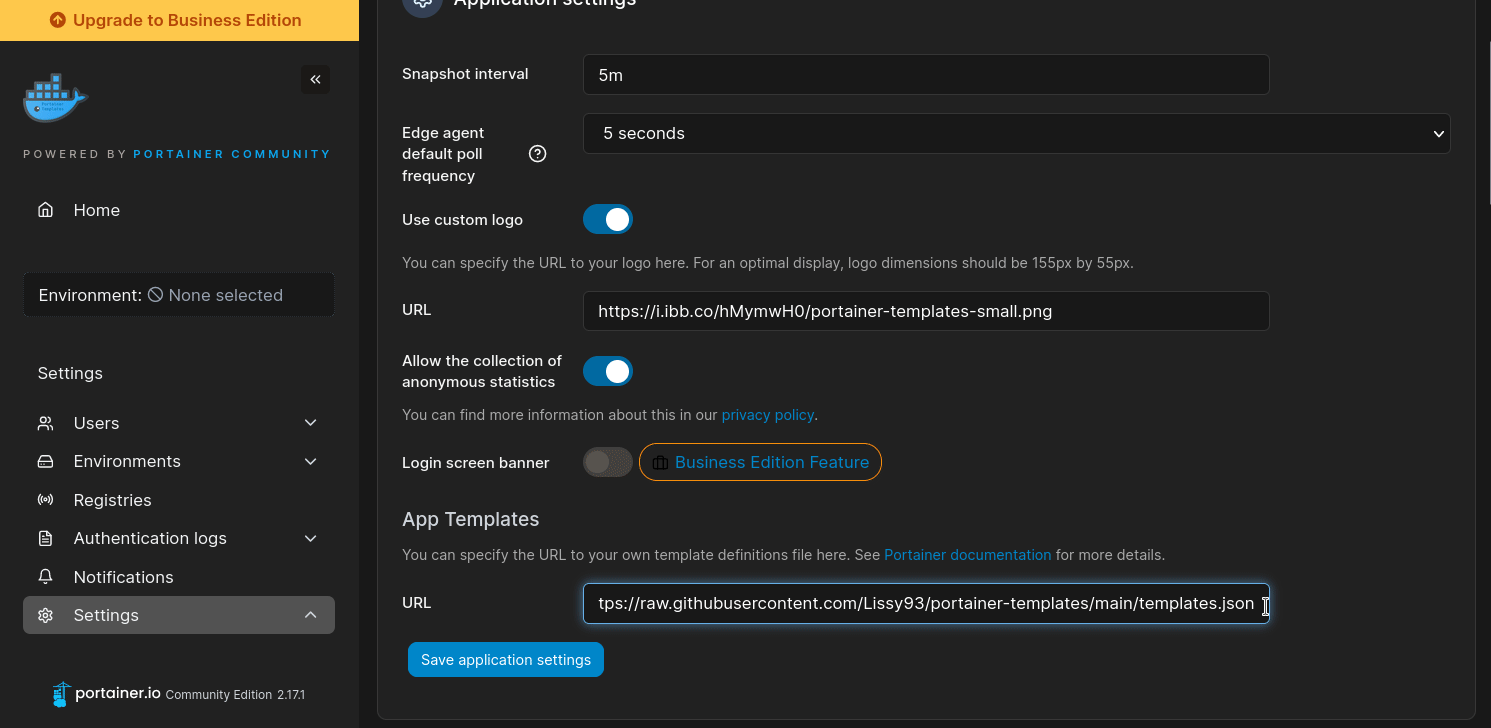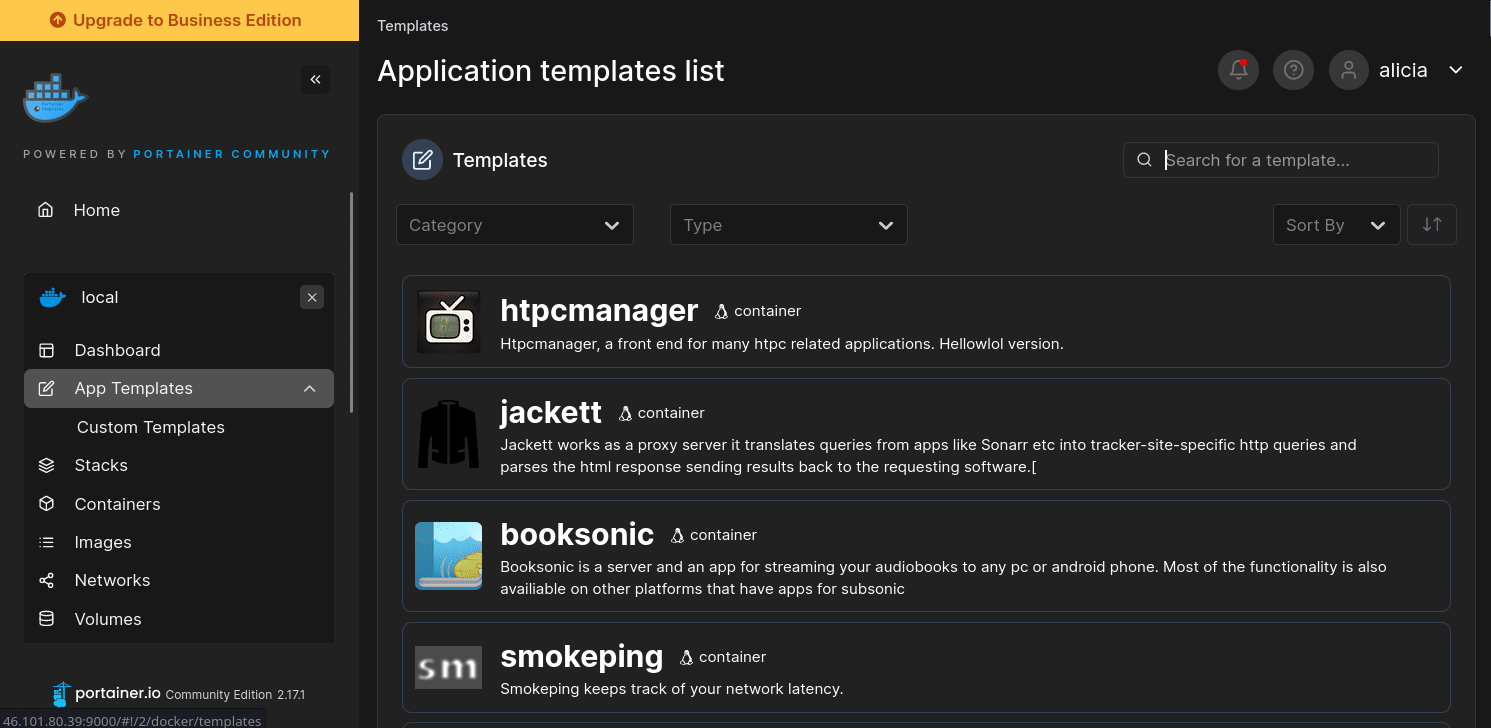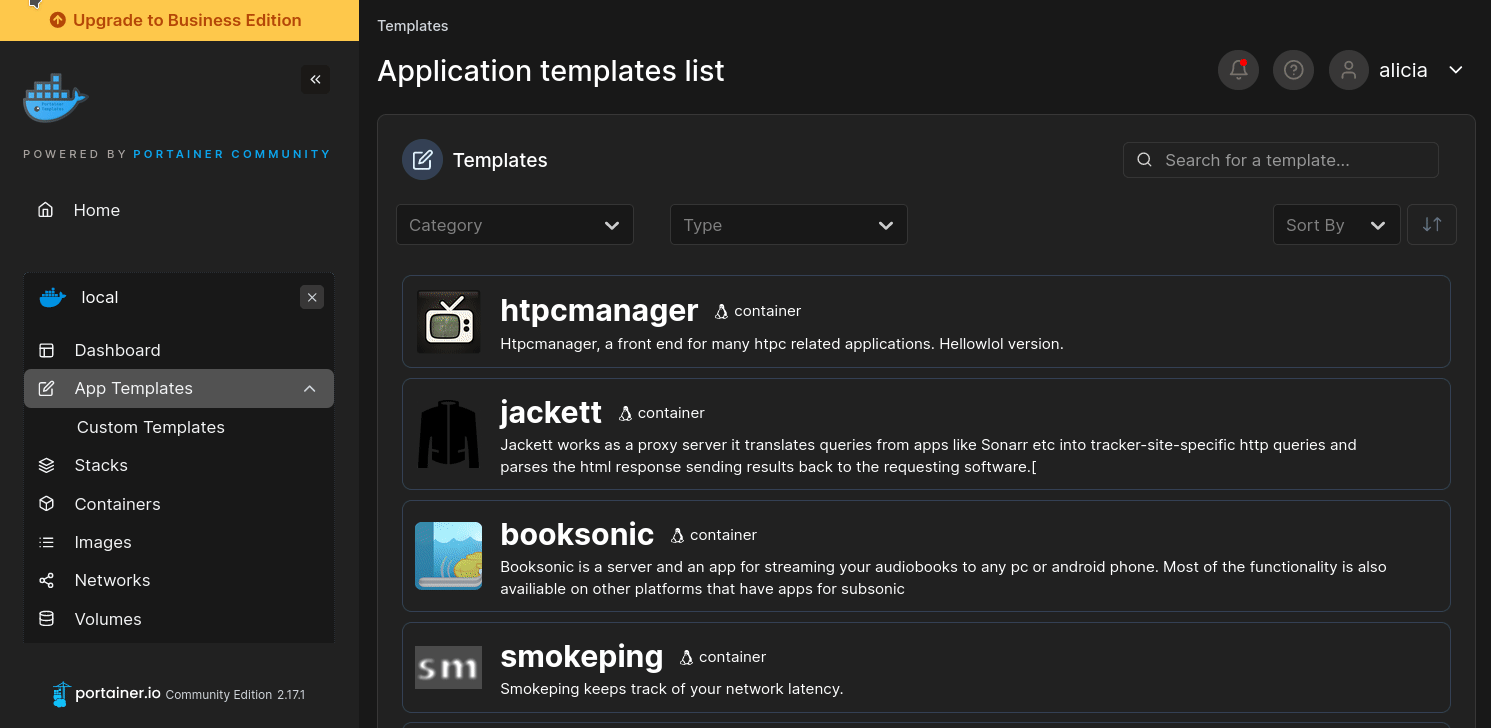
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select Murmur, fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
More install options in our documentation, or see goofball222/murmur for app-specific guidance.
Murmur Docker Container


| Docker Tag | Murmur Version | Description | Release Date |
|---|---|---|---|
| latest | 1.3.4 | Latest stable release | 2021-02-10 |
| 1.3.4 | 1.3.4 | Static stable release tag/image | 2021-02-10 |
Usage
This container exposes four volumes:/opt/murmur/cert- Murmur SSL certificate files/opt/murmur/config- Murmur configuration files/opt/murmur/data- Murmur database and other data files/opt/murmur/log- Murmur log for troubleshooting
This container exposes two ports:
64738/tcpMurmur server TCP port64738/udpMurmur server UDP port
The most basic way to run this container:
$ docker run --name murmur -d \
    -p 64738:64738/udp -p 64738:64738 \
    goofball222/murmur
```

---

**Recommended: run via [Docker Compose](https://docs.docker.com/compose/):**

Have the container store the config & logs on a local file-system or in a specific, known data volume (recommended for persistence and
 troubleshooting):


```bash

version: '3'

services:
  murmur:
    image: goofball222/murmur
    container_name: murmur
    ports:
      - 64738:64738
      - 64738:64738/udp
    volumes:
      - /etc/localtime:/etc/localtime:ro
      - ./cert:/opt/murmur/cert
      - ./config:/opt/murmur/config
      - ./data:/opt/murmur/data
      - ./log:/opt/murmur/log
    environment:
      - TZ=UTC
Example
docker-compose.yml fileEnvironment variables:
| Variable | Default | Description |
|---|---|---|
DEBUG | false | Set to true for extra entrypoint script verbosity for debugging |
MURMUROPTS | unset | Any additional custom run flags for the container murmur.x86 process |
MURMURSUPW | unset | Used to set/change the superuser password on the command line. NB/IMPORTANT: By design Murmur will not fully start or accept connections with the -supw command line option set. Start the container once to change the password, then stop the container and remove the variable. |
PGID | 999 | Specifies the GID for the container internal murmur group (used for file ownership) |
PUID | 999 | Specifies the UID for the container internal murmur user (used for process and file ownership) |
RUNCHOWN | true | Set to false to disable the container automatic chown at startup. Speeds up startup process on overlay2 Docker hosts. NB/IMPORTANT: It's critical that you insure directory/data permissions on all mapped volumes are correct before disabling this or murmur will not start. |
SSL custom certificate support (LetsEncrypt, etc.):
- Map the Docker host cert storage location or volume to the
/opt/murmur/certvolume exposed by the container - Must contain a PEM format SSL private key corresponding to the SSL certificate to be installed.
privkey.pem. - Must contain a PEM format SSL certificate file with the full certification chain. LetsEncrypt handles this automatically, other providers may need manual work (https://www.digicert.com/ssl-support/pem-ssl-creation.htm).
fullchain.pem.- Start the container. sslCert and sslKey paths in murmur.ini are updated automatically during startup if SSL certificate files are detected. Status, errors, etc. can be found in the container log, IE:
docker logs <containername>
If you don't want to use a custom SSL certificate then the
/opt/murmur/cert volume can be left unmapped. Alternatively if the privkey.pem and/or fullchain.pem file are not present SSL customization will be skipped.To revert from a custom cert to a Murmur self-signed certificate: stop the container, rename or remove both privkey.pem and fullchain.pem from
/DATA_VOLUME/murmur/cert. Then edit the murmur.ini file in /DATA_VOLUME/murmur/config and change the lines sslCert=/opt/murmur/cert/fullchain.pem to ;sslCert= & sslKey=/opt/murmur/cert/privkey.pem to ;sslKey=, save the file, and restart the container.Serve Murmur on your own domain behind Caddy, Nginx or Traefik. Fill in your domain and copy the result. It's a starting point, some apps need their own base URL or extra headers set too.
Proxying murmur.example.com to http://murmur:64738
Add this to your Caddyfile
murmur.example.com {
	reverse_proxy http://murmur:64738
}Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs murmur - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Port already in use
If deployment fails with "Bind for 0.0.0.0:64738 failed: port is already allocated", something else on your server is using that port.
- Find what's using it:
sudo ss -tlnp | grep :64738 - Stop the other service, or pick a different host port. In
64738:64738only the left number is yours to change, the right one belongs to the app.
Running but the page won't load
The container is up but nothing appears in your browser.
- Use your server's real IP:
http://your-server-ip:64738. The 0.0.0.0 link Portainer shows isn't a real address. - Give it a minute after first deploy, murmur can take a while to initialise.
- Make sure your firewall allows the port, e.g.
sudo ufw allow 64738
Permission denied on volumes
If the logs show "permission denied", the app can't write to its data folder on the host.
- Fix the ownership:
sudo chown -R 1000:100 /etc/localtime:ro(and the same for the other mapped folders) - Or set the
PUIDandPGIDvariables (defaults 1000:100) to match your own user, found withid $USER
Image won't pull
Test the pull directly on the host: docker pull goofball222/murmur:latest
- "manifest unknown" means the tag no longer exists. This template uses
latest, so try pinning a specific version instead. - "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- This image supports:
amd64 - Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect murmur --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Required settings are blank
TZ has no default value, and murmur may crash or misbehave if left empty.
- Fill it in on the deploy screen before hitting deploy.
Upstream project is archived
The developers have archived goofball222/murmur, so bugs and security issues won't be fixed.
- It'll keep working for now, but consider the similar apps below for a maintained alternative.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue on goofball222/murmur
- Template not working: Open an issue on xneo1/portainer_templates
- This website not working: Open an issue on lissy93/portainer-templates
A single container
Murmur runs as one container, the simplest kind of app here. Just the one image to pull and nothing else wired up alongside it.
The app image
An image is the app packed up ready to go, everything Murmur needs bundled into one download. This template pulls goofball222/murmur:latest, which Docker fetches once (about 18 MB) and then starts your own copy from.
Where the image comes from
Docker pulls its images from registries, public libraries of ready-built apps. Murmur's comes from Docker Hub, published by goofball222.
Version tags
The bit after the colon in the image name is the version tag. Here it's latest, which always points at the newest build, so a redeploy can bump you to a newer release without you asking. Newest right now is 1.3.4. Pin a specific tag if you would rather stay on one version.
Which machines it runs on
Every image is built for particular CPU types. This one ships for amd64, so it runs on regular x86 PCs and servers, though not ARM boards like a Raspberry Pi.
Ports
A port is the door the app answers on. A mapping like 64738:64738 means it's reachable on port 64738 of your server, where the left number is yours to change and the right one belongs to the app. It opens:
64738:6473864738:64738over UDP
Volumes
A volume is where Murmur keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/etc/localtimefrom/etc/localtime:roon the host/opt/murmur/configfrom/portainer/Files/Config/Murmuron the host/opt/murmur/datafrom/portainer/Files/Murmur/dataon the host/opt/murmur/logfrom/portainer/Files/Murmur/logon the host
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. Murmur takes 3 of them, and one needs a value before it'll start properly:
PUID, defaults to1000PGID, defaults to100TZ, needs a value
Restart policy
The restart policy here is unless-stopped, so Docker restarts Murmur after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Users and permissions
The PUID and PGID settings tell it which user and group to act as on your host. Point them at your own account (find yours with id $USER) so the files it writes into your mounted folders come out owned by you rather than root.
Networking
Nothing custom is set, so Murmur sits on Docker's default bridge network: its own private space that reaches the outside world only through the ports it publishes.
Container name
Once it's deployed, Portainer names the container murmur. That's what you'll spot in the containers list and use in commands like docker logs murmur.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Open source license
Murmur is open source, released under the Apache-2.0 license. In plain terms the code is out in the open, so you're free to run it and change it to fit what you need.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set Murmur up. Add the template list to Portainer once, then deploying Murmur is a click rather than a wall of config.