
![Boinc]() Boinc
Container
BOINC is a platform for high-throughput computing on a large scale (thousands or millions of computers). It can be used for volunteer computing (using consumer devices) or grid computing (using organizational resources). It supports virtualized, parallel, and GPU-based applications.
Image details
Configuration
TypeContainerlinuxlinuxserver/boinc:latest8080:8080/tcp8181:8181/tcp/config : /srv/lsio/boinc/configPUID=1000PGID=1000TZ=Etc/UTCPASSWORD=unless-stoppedTemplate by technorabilia
Notes
Ensure to create the following volume directories on the host file system, or modify the paths in the volume mapping section under the advanced options below, as needed.
mkdir -p /srv/lsio/boinc/config
Standalone Install
Select an install method, to see config/commands for deploying Boinc
Install on Portainer
Import all app templates into your Portainer instance, for easy 1-click deploys
- Ensure both Docker and Portainer are installed, and up-to-date
- Log into your Portainer web UI
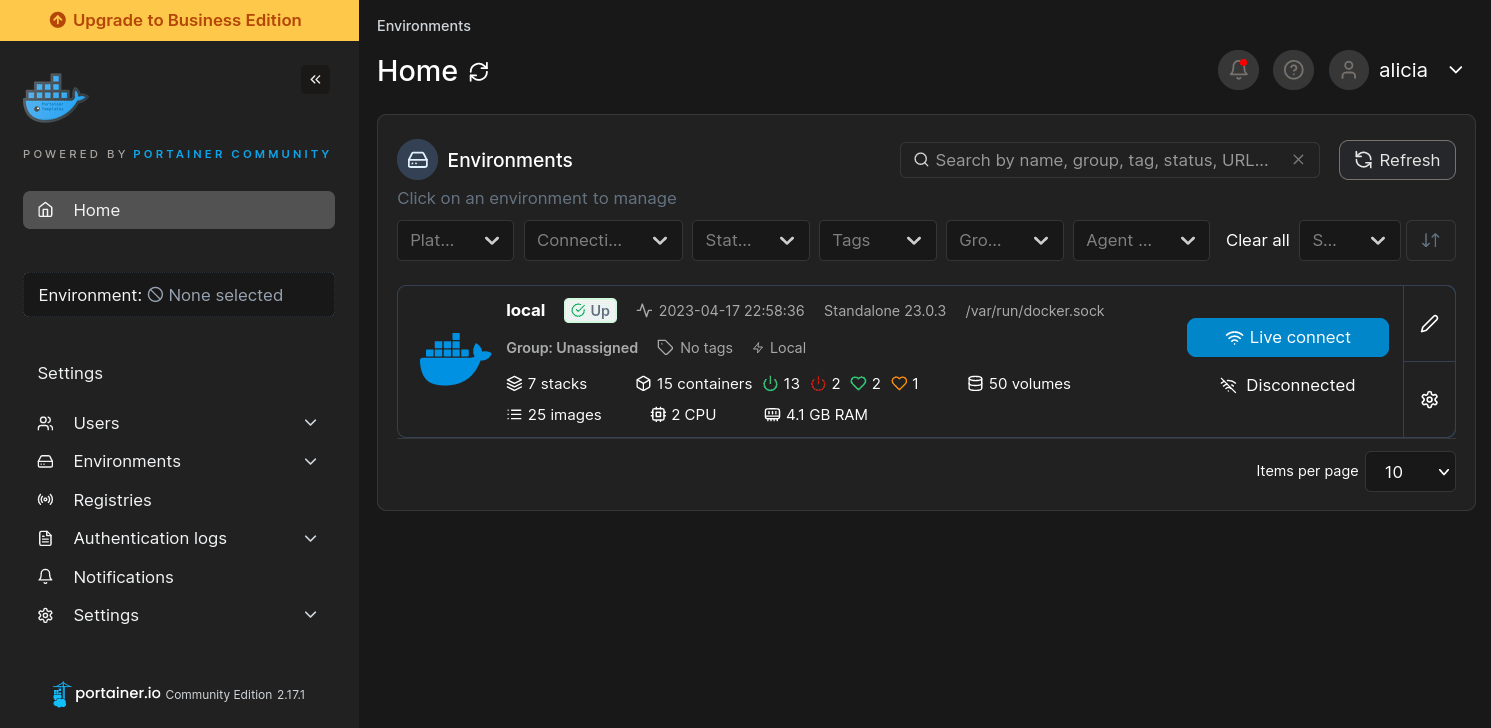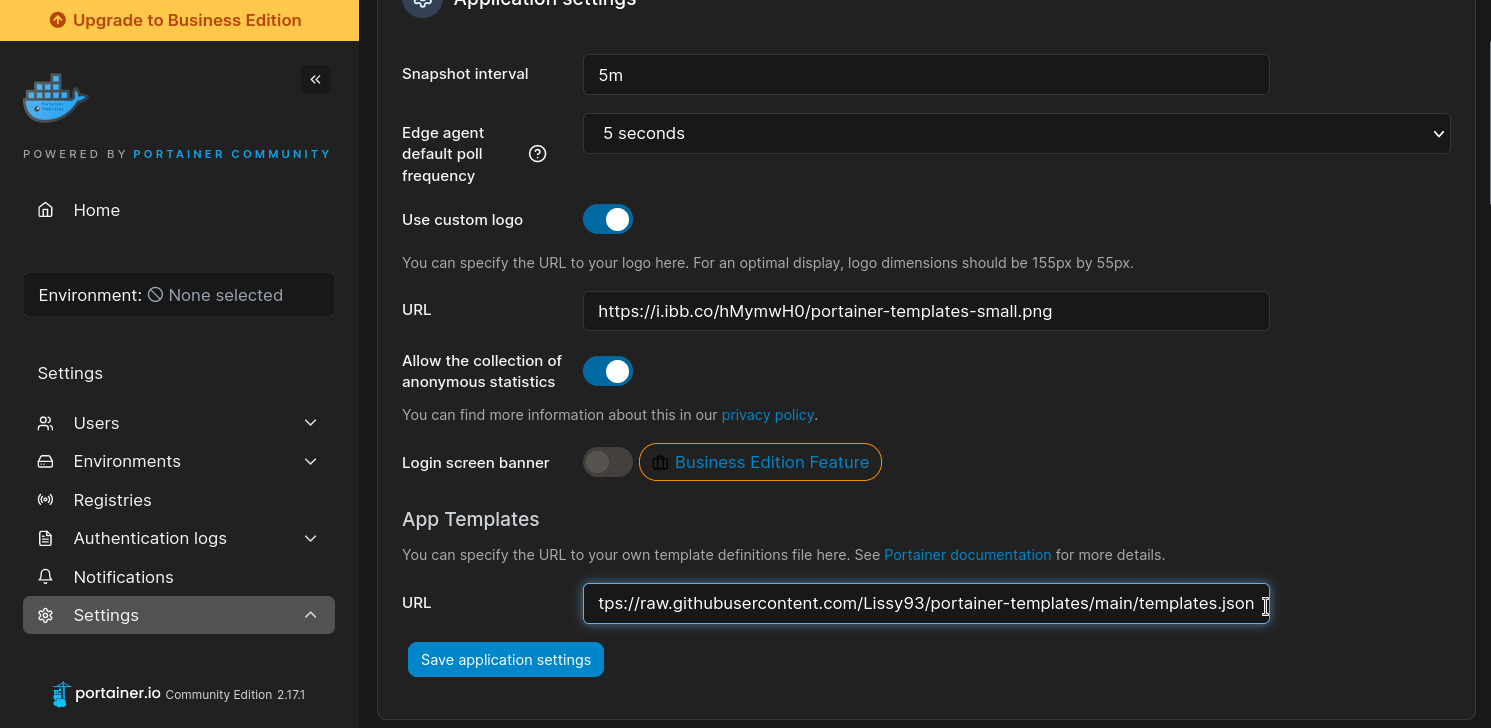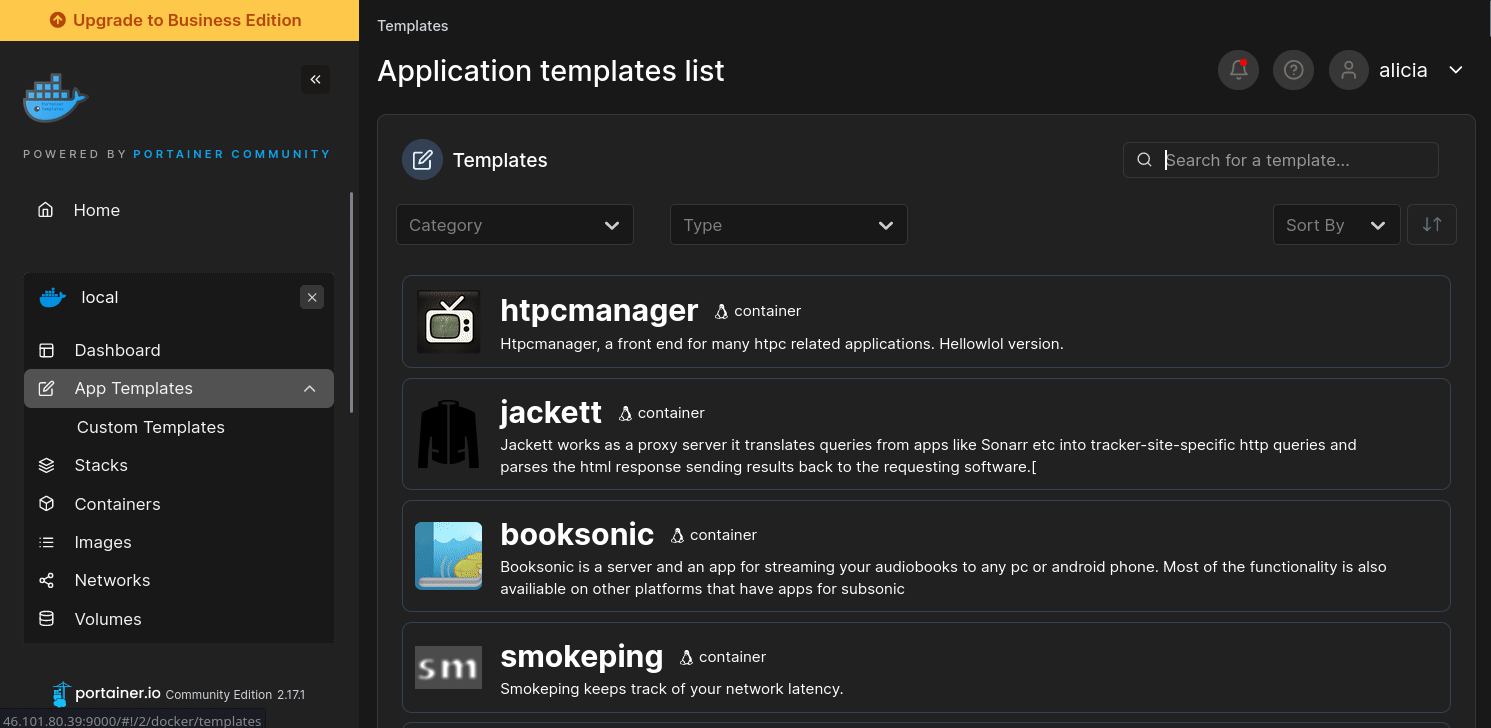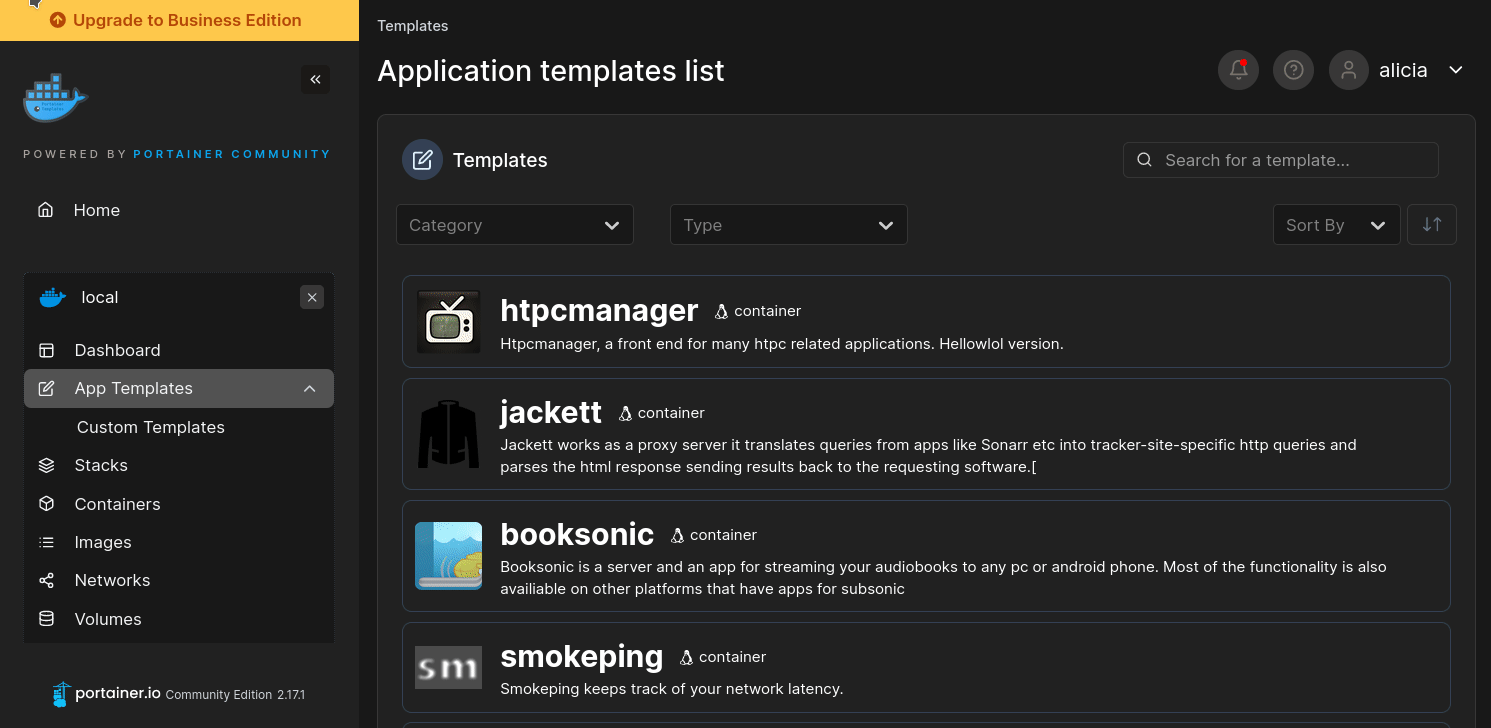
- Under Settings → App Templates, paste the below URL
- Head to Home → App Templates, and the list of apps will show up
- Select Boinc, fill in any config options, and hit Deploy
Template Import URL
https://raw.githubusercontent.com/Lissy93/portainer-templates/main/templates.json
Show Me
More install options in our documentation.


The LinuxServer.io team brings you another container release featuring:
- regular and timely application updates
- easy user mappings (PGID, PUID)
- custom base image with s6 overlay
- weekly base OS updates with common layers across the entire LinuxServer.io ecosystem to minimise space usage, down time and bandwidth
- regular security updates
Find us at:
- Blog - all the things you can do with our containers including How-To guides, opinions and much more!
- Discord - realtime support / chat with the community and the team.
- Discourse - post on our community forum.
- GitHub - view the source for all of our repositories.
- Open Collective - please consider helping us by either donating or contributing to our budget
linuxserver/boinc


BOINC is a platform for high-throughput computing on a large scale (thousands or millions of computers). It can be used for volunteer computing (using consumer devices) or grid computing (using organizational resources). It supports virtualized, parallel, and GPU-based applications.
Supported Architectures
We utilise the docker manifest for multi-platform awareness. More information is available from docker here and our announcement here.Simply pulling
lscr.io/linuxserver/boinc:latest should retrieve the correct image for your arch, but you can also pull specific arch images via tags.The architectures supported by this image are:
| Architecture | Available | Tag |
|---|---|---|
| x86-64 | ✅ | amd64-\ |
| arm64 | ✅ | arm64v8-\ |
Application Setup
The container can be accessed at:- https://yourhost:8181/
Strict reverse proxies
This image uses a self-signed certificate by default. This naturally means the scheme ishttps.
If you are using a reverse proxy which validates certificates, you need to disable this check for the container.Hardware Acceleration
Many desktop applications need access to a GPU to function properly and even some Desktop Environments have compositor effects that will not function without a GPU. However this is not a hard requirement and all base images will function without a video device mounted into the container.Intel/ATI/AMD
To leverage hardware acceleration you will need to mount /dev/dri video device inside of the container.--device=/dev/dri:/dev/driWe will automatically ensure the abc user inside of the container has the proper permissions to access this device.
Nvidia
Hardware acceleration users for Nvidia will need to install the container runtime provided by Nvidia on their host, instructions can be found here: https://github.com/NVIDIA/nvidia-container-toolkitWe automatically add the necessary environment variable that will utilise all the features available on a GPU on the host. Once nvidia-container-toolkit is installed on your host you will need to re/create the docker container with the nvidia container runtime
--runtime=nvidia and add an environment variable -e NVIDIA_VISIBLE_DEVICES=all (can also be set to a specific gpu's UUID, this can be discovered by running nvidia-smi --query-gpu=gpu_name,gpu_uuid --format=csv ). NVIDIA automatically mounts the GPU and drivers from your host into the container.Arm Devices
Best effort is made to install tools to allow mounting in /dev/dri on Arm devices. In most cases if /dev/dri exists on the host it should just work. If running a Raspberry Pi 4 be sure to enabledtoverlay=vc4-fkms-v3d in your usercfg.txt.This container is based on Docker Baseimage Selkies, which streams a desktop or single application to your web browser. Only the essentials are covered below, the full platform documentation lives at docs.linuxserver.io/selkies.
Start Minimal
Most support issues we see stem from large run configurations assembled from years of forum posts. These containers are designed to work with almost nothing. Start with the minimal command below, confirm it works, then add your options (volumes, env vars, GPU flags) one at a time:docker run --rm -it \
--shm-size=1gb \
-p 8181:8181 \
lscr.io/linuxserver/boinc:latest bashOpen https://localhost:8181 (note the
https) and accept the self signed certificate warning. The trailing bash gives you a shell inside the container, ctrl+d exits and cleans everything up. If a bigger setup misbehaves, return to this command to isolate the problem, see the Quickstart and Troubleshooting guides.GPU Acceleration
A GPU is optional, the CPU pipeline is fast enough for smooth sessions on modest hardware. When a GPU is mounted into the container it is automatically detected and configured for zero copy rendering and encoding, setAUTO_GPU=false to disable this behavior.Intel / AMD (open source drivers), one flag is all it takes:
docker run --rm -it \
  --shm-size=1gb \
  -p 8181:8181 \
  --device /dev/dri \
  lscr.io/linuxserver/boinc:latest bash
Nvidia (proprietary drivers, not available on Alpine based images):
Requires host driver 580 or newer installed from the
.run file downloaded directly from Nvidia. On drivers older than 595.80 you may also need kernel parameters and a dummy plug, see GPU Acceleration before opening an issue.docker run --rm -it \
--shm-size=1gb \
-p 8181:8181 \
--runtime nvidia \
--gpus all \
--device /dev/nvidia-modeset \
lscr.io/linuxserver/boinc:latest bashCompose examples, multi GPU selection (
DRINODE/DRI_NODE), Unraid notes, and a step by step debugging loop are in the GPU Acceleration guide.Security
>!WARNING >This container provides privileged access to the host system. Do not expose it to the Internet unless you have secured it properly.HTTPS is required. Modern browser features used for video and audio (WebCodecs) only work in a secure context. Port
8181 serves HTTPS directly, the HTTP port exists only to sit behind a reverse proxy.By default there is no authentication. Setting the
CUSTOM_USER and PASSWORD environment variables enables HTTP basic auth, which is suitable only for a trusted local network. For internet exposure, place the container behind a reverse proxy with robust authentication, such as SWAG. Keep in mind the web interface includes a terminal with passwordless sudo, anyone who can reach the GUI can gain root inside the container.Authentication options, sharing link behavior, container isolation, and the lockdown variables for kiosk style deployments are covered in Security and Hardening.
Language Support - Internationalization
To launch the session in a different language, set theLC_ALL environment variable, e.g. -e LC_ALL=zh_CN.UTF-8 (Chinese), ja_JP.UTF-8 (Japanese), ko_KR.UTF-8 (Korean), ar_AE.UTF-8 (Arabic), ru_RU.UTF-8 (Russian), es_MX.UTF-8 (Spanish Latin America), de_DE.UTF-8 (German), fr_FR.UTF-8 (French), nl_NL.UTF-8 (Dutch), it_IT.UTF-8 (Italian).Beyond Running the App
This image inherits every capability of the Selkies platform, all documented in depth on the docs site:- Configuration Reference - every environment variable: ports, subfolder reverse proxy, custom dashboards, watermarking, and the full set of
SELKIES_*stream, feature, and UI settings with their|lockedsyntax. - Using the Web Client - file transfer, clipboard sync, audio and microphone, up to four gamepads, session sharing, and mobile touch support.
- Installing Applications - persistent user installed apps with proot-apps (
proot-apps install filezilla) or native packages at boot with Docker mods. - Docker in Docker and host Docker control - run
--privilegedfor an isolated DinD setup, or mount/var/run/docker.sockto manage the host. - Reverse Proxy - proxying websockets and subfolders correctly.
- SealSkin - turnkey multi user VDI orchestration with browser extension and mobile apps, this image is fully compatible.
- Pelorus - expose the session to AI agents via a computer use API and accessibility stack.
Usage
To help you get started creating a container from this image you can either use docker-compose or the docker cli.>!NOTE >Unless a parameter is flagged as 'optional', it is mandatory and a value must be provided.
docker-compose (recommended, click here for more info)
---
services:
  boinc:
    image: lscr.io/linuxserver/boinc:latest
    container_name: boinc
    environment:
      - PUID=1000
      - PGID=1000
      - TZ=Etc/UTC
      - PASSWORD= #optional
    volumes:
      - /path/to/boinc/config:/config
    ports:
      - 8080:8080
      - 8181:8181
    devices:
      - /dev/dri:/dev/dri #optional
    shm_size: "1gb"
    restart: unless-stopped
docker cli (click here for more info)
docker run -d \
  --name=boinc \
  -e PUID=1000 \
  -e PGID=1000 \
  -e TZ=Etc/UTC \
  -e PASSWORD= `#optional` \
  -p 8080:8080 \
  -p 8181:8181 \
  -v /path/to/boinc/config:/config \
  --device /dev/dri:/dev/dri `#optional` \
  --shm-size="1gb" \
  --restart unless-stopped \
  lscr.io/linuxserver/boinc:latest
Parameters
Containers are configured using parameters passed at runtime (such as those above). These parameters are separated by a colon and indicate<external>:<internal> respectively. For example, -p 8080:80 would expose port 80 from inside the container to be accessible from the host's IP on port 8080 outside the container.| Parameter | Function |
|---|---|
-p 8080:8080 | Boinc desktop gui HTTP (only to be used by reverse proxies and not direct access). |
-p 8181:8181 | Boinc desktop gui HTTPS. |
-e PUID=1000 | for UserID - see below for explanation |
-e PGID=1000 | for GroupID - see below for explanation |
-e TZ=Etc/UTC | specify a timezone to use, see this list. |
-e PASSWORD= | Optionally set a password for the gui. |
-v /config | Where BOINC should store its database and config. |
--device /dev/dri | Only needed if you want to use your Intel GPU (vaapi). |
--shm-size= | Recommended for all desktop images. |
Environment variables from files (Docker secrets)
You can set any environment variable from a file by using a special prependFILE__.As an example:
-e FILE__MYVAR=/run/secrets/mysecretvariableWill set the environment variable
MYVAR based on the contents of the /run/secrets/mysecretvariable file.Umask for running applications
For all of our images we provide the ability to override the default umask settings for services started within the containers using the optional-e UMASK=022 setting.
Keep in mind umask is not chmod it subtracts from permissions based on it's value it does not add. Please read up here before asking for support.User / Group Identifiers
When using volumes (-v flags), permissions issues can arise between the host OS and the container, we avoid this issue by allowing you to specify the user PUID and group PGID.Ensure any volume directories on the host are owned by the same user you specify and any permissions issues will vanish like magic.
In this instance
PUID=1000 and PGID=1000, to find yours use id your_user as below:id your_userExample output:
uid=1000(your_user) gid=1000(your_user) groups=1000(your_user)Docker Mods


We publish various Docker Mods to enable additional functionality within the containers. The list of Mods available for this image (if any) as well as universal mods that can be applied to any one of our images can be accessed via the dynamic badges above.
Support Info
- Shell access whilst the container is running:
```bash
docker exec -it boinc /bin/bash
```- To monitor the logs of the container in realtime:
```bash
docker logs -f boinc
```- Container version number:
```bash
docker inspect -f '{{ index .Config.Labels "build_version" }}' boinc
```- Image version number:
```bash
docker inspect -f '{{ index .Config.Labels "build_version" }}' lscr.io/linuxserver/boinc:latest
```
Updating Info
Most of our images are static, versioned, and require an image update and container recreation to update the app inside. With some exceptions (noted in the relevant readme.md), we do not recommend or support updating apps inside the container. Please consult the Application Setup section above to see if it is recommended for the image.Below are the instructions for updating containers:
Via Docker Compose
- Update images:
* All images:

    ```bash
    docker-compose pull
    ```

* Single image:

    ```bash
    docker-compose pull boinc
```- Update containers:
* All containers:

    ```bash
    docker-compose up -d
    ```

* Single container:

    ```bash
    docker-compose up -d boinc
```- You can also remove the old dangling images:
```bash
docker image prune
```
Via Docker Run
- Update the image:
```bash
docker pull lscr.io/linuxserver/boinc:latest
```- Stop the running container:
```bash
docker stop boinc
```- Delete the container:
```bash
docker rm boinc
```- Recreate a new container with the same docker run parameters as instructed above (if mapped correctly to a host folder, your
/configfolder and settings will be preserved) - You can also remove the old dangling images:
```bash
docker image prune
```
Image Update Notifications - Diun (Docker Image Update Notifier)
>!TIP >We recommend Diun for update notifications. Other tools that automatically update containers unattended are not recommended or supported.Building locally
If you want to make local modifications to these images for development purposes or just to customize the logic:git clone https://github.com/linuxserver/docker-boinc.git
cd docker-boinc
docker build \
--no-cache \
--pull \
-t lscr.io/linuxserver/boinc:latest .The ARM variants can be built on x8664 hardware and vice versa using
lscr.io/linuxserver/qemu-staticdocker run --rm --privileged lscr.io/linuxserver/qemu-static --resetOnce registered you can define the dockerfile to use with
-f Dockerfile.aarch64.Versions
- 19.04.26: - Rebase to resolute, make Wayland default disable with PIXELFLUXWAYLAND=false.
- 28.12.25: - Add Wayland init logic.
- 07.07.25: - Rebase to selkies. Breaking change: HTTPS is now required. Use port 8181 with HTTPS for direct access. Reverse proxies can connect to 8080 over http as long as it's served over HTTPS to the user.
- 19.08.24: - Rebase to noble.
- 10.02.24: - Update Readme with new env vars and ingest proper PWA icon.
- 03.04.23: - Rebase to KasmVNC base image. Deprecate armhf build as the new base does not support it. Add bzip2 and xz-utils.
- 14.11.22: - Fix opencl driver.
- 18.09.22: - Rebase to jammy.
- 24.02.22: - Rebase to focal.
- 31.01.22: - Improve device permissions setting verbosity.
- 23.03.21: - Rebase to rdesktop-web baseimage. Deprecate
GUAC_USERandGUAC_PASSenv vars. Existing users can set the new varPASSWORDfor the userabc. - 01.04.20: - Install boinc from ppa.
- 17.03.20: - Add armhf and aarch64 builds and switch to multi-arch image.
- 16.03.20: - Clean up old pid files.
- 15.03.20: - Initial release.
Serve Boinc on your own domain behind Caddy, Nginx or Traefik. Fill in your domain and copy the result. It's a starting point, some apps need their own base URL or extra headers set too.
Proxying boinc.example.com to http://Boinc:8080
Add this to your Caddyfile
boinc.example.com {
	reverse_proxy http://Boinc:8080
}Check the logs first
Nine times out of ten the logs tell you exactly what went wrong.
- In Portainer, go to Containers, click the container, then Logs. Or run
docker logs Boinc - Exit codes help too:
137means killed, usually out of memory.126or127means the command inside the image is broken.
Port already in use
If deployment fails with "Bind for 0.0.0.0:8080 failed: port is already allocated", something else on your server is using that port.
- Find what's using it:
sudo ss -tlnp | grep :8080 - Stop the other service, or pick a different host port. In
8080:8080only the left number is yours to change, the right one belongs to the app.
Running but the page won't load
The container is up but nothing appears in your browser.
- Use your server's real IP:
http://your-server-ip:8080. The 0.0.0.0 link Portainer shows isn't a real address. - Give it a minute after first deploy, Boinc can take a while to initialise.
- Make sure your firewall allows the port, e.g.
sudo ufw allow 8080
Permission denied on volumes
If the logs show "permission denied", the app can't write to its data folder on the host.
- Fix the ownership:
sudo chown -R 1000:1000 /srv/lsio/boinc/config - Or set the
PUIDandPGIDvariables (defaults 1000:1000) to match your own user, found withid $USER
Image won't pull
Test the pull directly on the host: docker pull linuxserver/boinc:latest
- "manifest unknown" means the tag no longer exists. This template uses
latest, so try pinning a specific version instead. - "toomanyrequests" is the Docker Hub rate limit. Log in with
docker loginto raise it. - "no space left on device" means a full disk. Reclaim space with
docker system prune
"exec format error"
This means the image was built for a different CPU architecture than your server.
- This image supports:
amd64, arm64 - Check yours with
uname -m: x86_64 is amd64, aarch64 is arm64. Raspberry Pi and other ARM boards are the usual culprits.
Container keeps restarting
The unless-stopped restart policy relaunches the app after every crash, so the real error can scroll past.
- Check the logs right after a restart, the last few lines before it died are the useful ones.
- Get the exit code with
docker inspect Boinc --format '{{.State.ExitCode}}' - Still stuck? Redeploy once with the restart policy set to
noso the failure stays visible.
Required settings are blank
PASSWORD has no default value, and Boinc may crash or misbehave if left empty.
- Fill it in on the deploy screen before hitting deploy.
Raise an issue
Found something which isn't working as it should? Here's how to report it.
- Bug within the app: Open an issue within Boinc's repo
- Template not working: Open an issue on technorabilia/portainer-templates
- This website not working: Open an issue on lissy93/portainer-templates
A single container
Boinc runs as one container, the simplest kind of app here. Just the one image to pull and nothing else wired up alongside it.
The app image
An image is the app packed up ready to go, everything Boinc needs bundled into one download. This template pulls linuxserver/boinc:latest, which Docker fetches once (about 1009 MB) and then starts your own copy from.
Where the image comes from
Docker pulls its images from registries, public libraries of ready-built apps. Boinc's comes from Docker Hub, published by linuxserver.
Version tags
The bit after the colon in the image name is the version tag. Here it's latest, which always points at the newest build, so a redeploy can bump you to a newer release without you asking. Newest right now is 8.2.8. Pin a specific tag if you would rather stay on one version.
Which machines it runs on
Every image is built for particular CPU types. This one ships for amd64, arm64, so it runs on both regular x86 servers and ARM boards like a Raspberry Pi.
Ports
A port is the door the app answers on. A mapping like 8080:8080 means it's reachable on port 8080 of your server, where the left number is yours to change and the right one belongs to the app. Once it's running, open http://your-server-ip:8080 in a browser. It opens:
8080:8080, likely the web interface8181:8181
Volumes
A volume is where Boinc keeps its files so they survive an update or a restart. Without one, anything it saves would sit inside the container and vanish the moment it's recreated. This template mounts:
/configfrom/srv/lsio/boinc/configon the host
Environment variables
Environment variables are the settings you hand over when you deploy, things like a password or a timezone. Boinc takes 4 of them, and one needs a value before it'll start properly:
PUID, defaults to1000. Run 'id [USER]' for the owner of the host volume directories to get the UID to use here.PGID, defaults to1000. Run 'id [USER]' for the owner of the host volume directories to get the GID to use here.TZ, defaults toEtc/UTC. Specify a timezone to use, see this list.PASSWORD, needs a value. Optionally set a password for the gui. [OPTIONAL]
Restart policy
The restart policy here is unless-stopped, so Docker restarts Boinc after a crash or reboot, but leaves it off when you stop it on purpose. You can change this on the deploy screen. The choices are no (never restart), on-failure (only after a crash), unless-stopped (restart unless you stop it), and always (bring it back no matter what).
Users and permissions
The PUID and PGID settings tell it which user and group to act as on your host. Point them at your own account (find yours with id $USER) so the files it writes into your mounted folders come out owned by you rather than root.
Networking
Nothing custom is set, so Boinc sits on Docker's default bridge network: its own private space that reaches the outside world only through the ports it publishes.
Container name
Once it's deployed, Portainer names the container Boinc. That's what you'll spot in the containers list and use in commands like docker logs Boinc.
Platform
The platform is linux, the kind of system the container is built to run on. Docker and Portainer handle this on a normal Linux server.
Portainer app templates
Zooming out, this whole page comes from a Portainer app template: a short recipe telling Portainer how to set Boinc up. Add the template list to Portainer once, then deploying Boinc is a click rather than a wall of config.